


shikoshib/winerr
A fast and accurate Windows fake error messages generator made with HTML5 Canvas
kyju.org
Horribly misusing Rust features to provide provable memory safety and tracing garbage collection for pointer soup.
Facebook's Most Dangerous Product
Third-party image hosting is never entirely reliable · Carelessly
Third-party image hosting is never entirely reliable — Carelessly
Open-source and .NET - it's not picking up
I have been sitting on this for a while, and had dozens of discussions about it too. The things I'm about to say here are a result of a journey. Yes, this is criticism; but from a respecting and caring place, coming from a long time OSS contributor in several software ecosystems, including .NET.
Wikipedia blacklists Archive.today, starts removing 695,000 archive links
If DDoSing a blog wasn't bad enough, archive site also tampered with web snapshots.
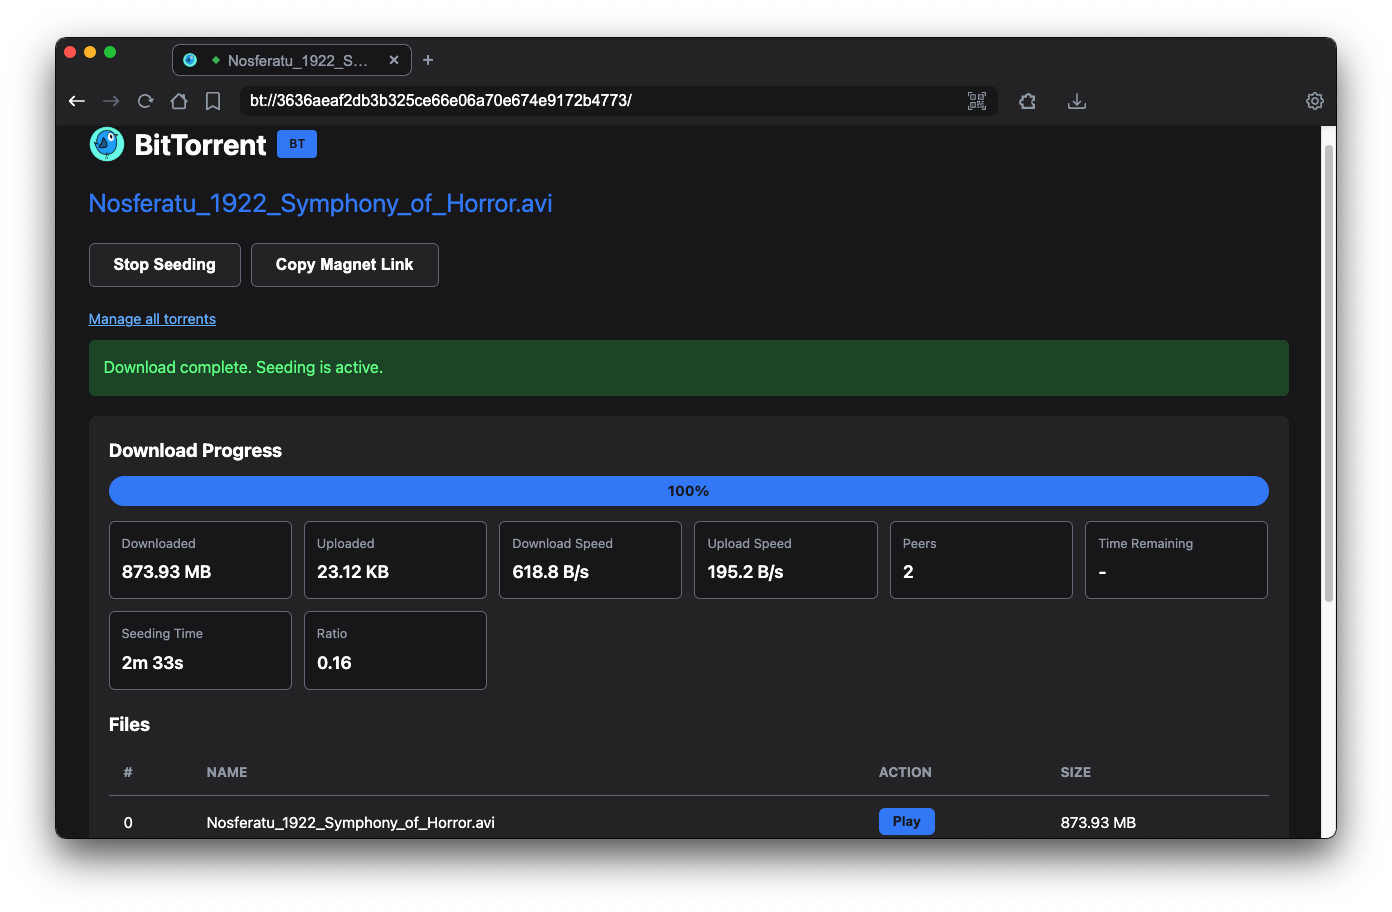
Peersky Browser (@peersky@mastodon.social)
Attached: 4 images 🚀 #PeerSky v1.0.0-beta.26 is here! - Opt-in BitTorrent seeding and management UI - Offline KaTeX math rendering and scientific markdown templates in p2pmd - Tests for IPFS, Hyper, HS, BitTorrent, and Extensions - Download management page with live popup tracking - Periodic IPFS CID re-providing and DHT stack overflow fix - Linux AppImage segfault fix - Extension stability fixes Try it out! 👉 https://peersky.p2plabs.xyz/
A new Anthropic model found security problems ‘in every major operating system and web browser’
Nvidia, Google, Apple, Microsoft, and others will use Claude Mythos Preview to spot vulnerabilities in their systems.

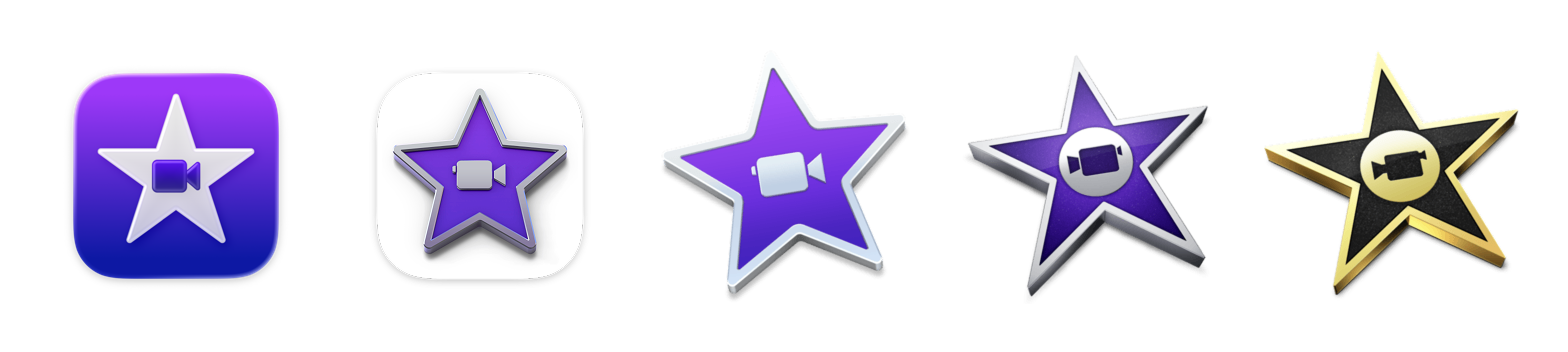
Something’s Rotten in the State of macOS Icon Design
Writing about the big beautiful mess that is making things for the world wide web.
Computers for Cynics 2 - It All Went Wrong at Xerox PARC
Computers for Cynics 2 - It All Went Wrong at Xerox PARC
Computers for Cynics 2 - It All Went Wrong at Xerox PARC
What do you think, @zicklag.dev and @expede.wtf?

Capability Chains: A Protocol-Level Extension of Object Capabilities, Draft 2
leaflet.pubOh dear lord, I knew it was bad, but didn't know it was this bad: hackers.pub/@fedify/2026/why-activitypub-… (I've mostly just contributed to activitypub projects that already existed, so didn't usually need to experience these specific pains)

Why implementing ActivityPub is hard, and why it doesn't have to be
hackers.pubwhy they’re bad? just ask claude. it ran into the same exact things i’ve ran into. until all of these are fixed imo its perfectly acceptable for developers to ignore permission sets. they’re just not baked until they’re understandable read this transcript: claude.ai/share/dbd3e30d-958d-4ac8-a3fc…

Claude
claude.ai

