

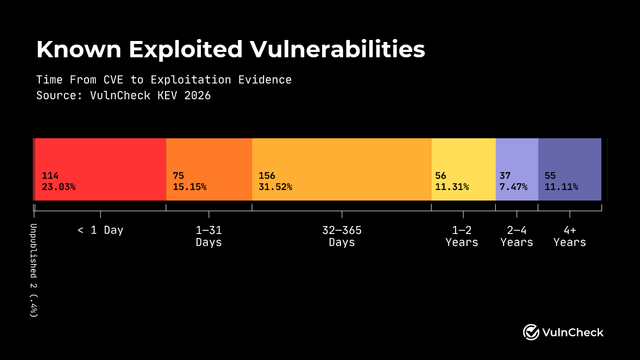
Thinking through how the conventional OSS security embargoes no longer buy us time, and what open source maintainers might do instead to respond
An Update on OpenTitan
Robin Berjon (@robin.berjon.com)
Again, we can try to be generous. But this fits a pattern. When people found issues in their open source code, instead of fixing them they went closed source. When they had an XSS vulnerability right at launch it took over a day for them to acknowledge and close it.


Former Apple Developer Explains Why The Company's Software Is Struggling - BGR
In recent months, Apple's software development has been called into question like never before. Between a critical security bug in macOS, a brand-new product being…
Tock OS A Rust Based Open Platform for Transparent and Secure Root of Trust Devices
What Happened to HackerOne?
The rise and fall of the largest bug bounty platform in the world
OpenAI #16: A History and a Proposal
The real news today is that Anthropic has partnered with the top companies in cybersecurity to try and patch everyone’s systems to fix all the thousands of zero-day exploits found by their new model Claude Mythos.
Be alert: targeted attacks on prominent Rustaceans | Rust Blog
Empowering everyone to build reliable and efficient software.
Anthony Fu
It’s not a secret that open-source projects are now a critical part of almost every software project. While most open-source projects are maintained by volunteers, the sustainability of these projects becomes a big concern. The recent xz/liblzma vulnerability accident is a great example that shows the importance of open-source projects and how severe the problem could be.
A new Anthropic model found security problems ‘in every major operating system and web browser’
Nvidia, Google, Apple, Microsoft, and others will use Claude Mythos Preview to spot vulnerabilities in their systems.

Hackathon on Decentralised Media - TEP (Trusted European Platforms) Bluesky, Nostr · Luma
Every year, thousands of developers of free and open-source software from all over the world gather at FOSDEM. For two weeks around this event – from the 26th…

NSF investing in secure open-source ecosystems
Open-source software is ubiquitous, supporting artificial intelligence, data science, cloud computing, telecommunications and scientific research tools. Despite these benefits, the number of open-source developers is relatively small, and many projects lack sufficient resources, slowing the pace of innovation and making maintenance difficult. In addition, weaknesses in open-source software, such as security flaws, supply chain risks or insider threats, can spread across many connected systems. In extreme cases, these weaknesses could lead to large-scale failures that affect national or global systems.
Microsoft Struggling With Hundreds of AI-Discovered Security Bugs — ProPublica
Anthropic’s Mythos has flagged bugs faster than Microsoft can fix them. Documents reviewed by ProPublica reveal the tech giant's “mad dash” behind the scenes to patch holes before hackers can find and exploit them.

The just-announced Open Source Endowment is now on Bluesky, and we're open to your ideas on how to identify critical OSS projects 🙏

Open Source Endowment
We heard the Bluesky community cares about Open Source, so we showed up 👋 Our endowment dedicated to supporting Open Source maintainers is already at $729k, and we're developing a model for distributing our first funding round. Have ideas on how to identify critical OSS projects? We're listening.
