

Operating atproto-entryway: the account service and OAuth authorization server in front of one or more PDS instances. What it owns, keys, pairing a member PDS, the full environment reference, reconciliation, and the traps.
Embracing ATProto, part 1: Setting up a PDS
In this series of posts, I'll explore my journey into setting up my workflows and services for atproto. The first step is setting up my PDS. Let's start with a bit of explanation for all this lingo.

Building AIP: An ATProtocol Authorization Gateway - Nick's Blog
OAuth is the first challenge developers face in the atmosphere. This post is about AIP, the authorization gateway we built at Graze Social to alleviate some of the pain.
OAuth Roadmap · bluesky-social atproto · Discussion #2656
OAuth is nigh! Protocol support has been a long time coming and we are pumped. It should greatly improve the user and developer experiences building secure apps and integrations on atproto. And cou...
OAuth for AT Protocol | Bluesky
We are very happy to release the initial specification of OAuth for AT Protocol! This is expected to be the primary authentication and authorization system between atproto client apps and PDS instances going forward, replacing the current flow using App Passwords and createSession over time.
ATProto Integration - poke_around
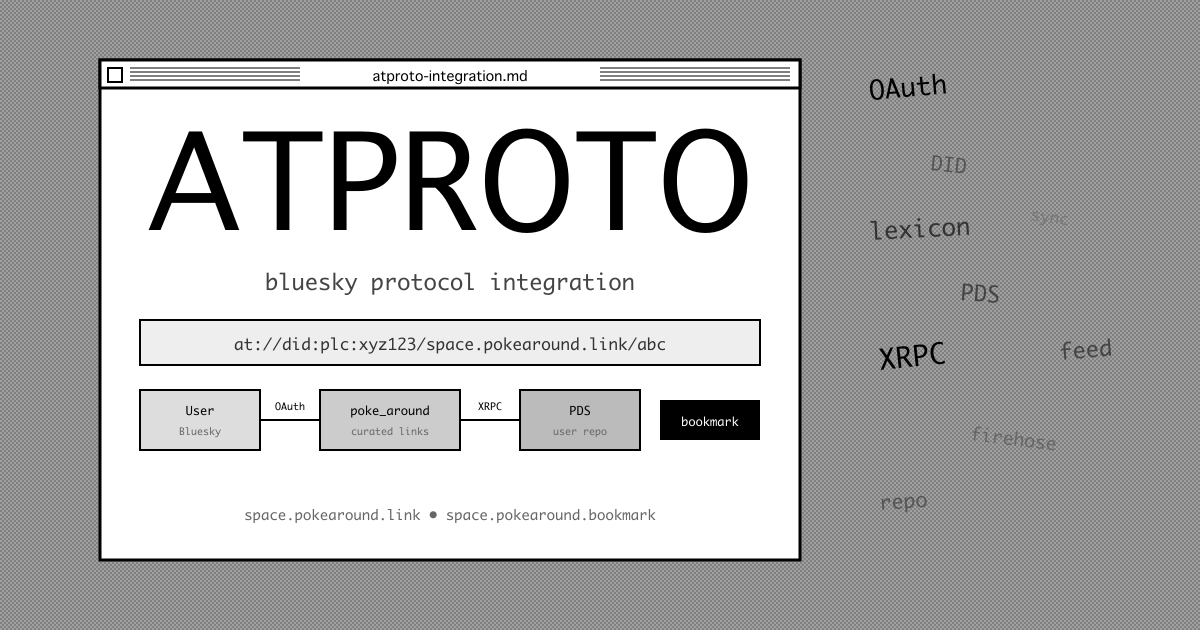
OAuth, PDS sync, custom lexicons, and user bookmarking via the AT Protocol.
Adversarial ATProto PDS Migration | Blog
An ATProto account lives on a Personal Data Server (PDS), and that service needs to be hosted somewhere by someone. There are a lot of options here, like a Raspberry Pi in your closet, a rented VPS in a datacentre, or a batteries-included service like bsky.social.
Beyond the Statusphere: Part 2, ATProto OAuth, the TLDR - Hitchhiker's Guide to the Atmosphere
Gain a working knowledge of ATProto OAuth and feel confident implementing it in your projects.
Beyond the Statusphere: Part 2, ATProto OAuth, the TLDR - Hitchhiker's Guide to the Atmosphere
Gain a working knowledge of ATProto OAuth and feel confident implementing it in your projects.
OAuth for ATProto Apps Part 2: Mobile Implementation - Lost in Inference
Part 2 of a 2-part series on implementing OAuth authentication for ATProto (Bluesky) applications.
Who Actually Owns Your ATProto Identity? Hint: It's Probably Not You
ATProto gives your PDS operator full control of your signing and rotation keys, letting them impersonate you across every app in the ecosystem or kill

Building OAuth Authentication for ATProto apps: Part 1, the web use-case - Building on atproto
In this follow-up OAuth implementation guide I dive a bit deeper into the actual implementation details of building authentication for your web or mobile app that builds on top of ATProto.
PDS operator guide — atproto-crates
Operating atproto-pds: production status, endpoint surface, storage profiles, build flags, the full environment variable reference, and the deployment modes that are deliberately not wired up.
the single most important part of atproto is the PDS as a user-controlled auth and storage layer to which clients can connect directly. death to appviews

Authenticated Transfer Enables Orchestration - nekomimi
blog.nekomimi.petAnother OIDC gateway approach for using your atproto account to login to many different things tangled.org/bkb.arcnode.xyz/atauth Nice work @bkb.arcnode.xyz!

bkb
Giving @tangled.org a try. Updates to the atauth OIDC gateway are live. Passkey login for all apps -- Sign in with biometrics or a security key on every app 8 security fixes enforced session expiry Multi-arch Docker on GHCR One docker pull for amd64 and arm64 (Pi, Apple Silicon)
here's my take on a minimal oauth browser client for atproto! no special API client class — just use plain `fetch` to make requests and a service worker automatically handles authorization headers/token refreshes/dpop retries/etc. (very experimental, not tested in production, use at your own risk)

jakelazaroff.com/atsw
tangled.org

