


MFA was supposed to solve our security problems, so why do attackers keep getting around it?
Rublon Multi-Factor Authentication (MFA) - Secure Remote Access
Start your Free Trial today. Secure access to networks, servers, VPNs, and applications using Two-Factor Authentication (MFA/2FA).

New Password Reset Policy to Enhance Account Security
Protecting DNSimple accounts with new security measures, including mandatory password resets for users without MFA.
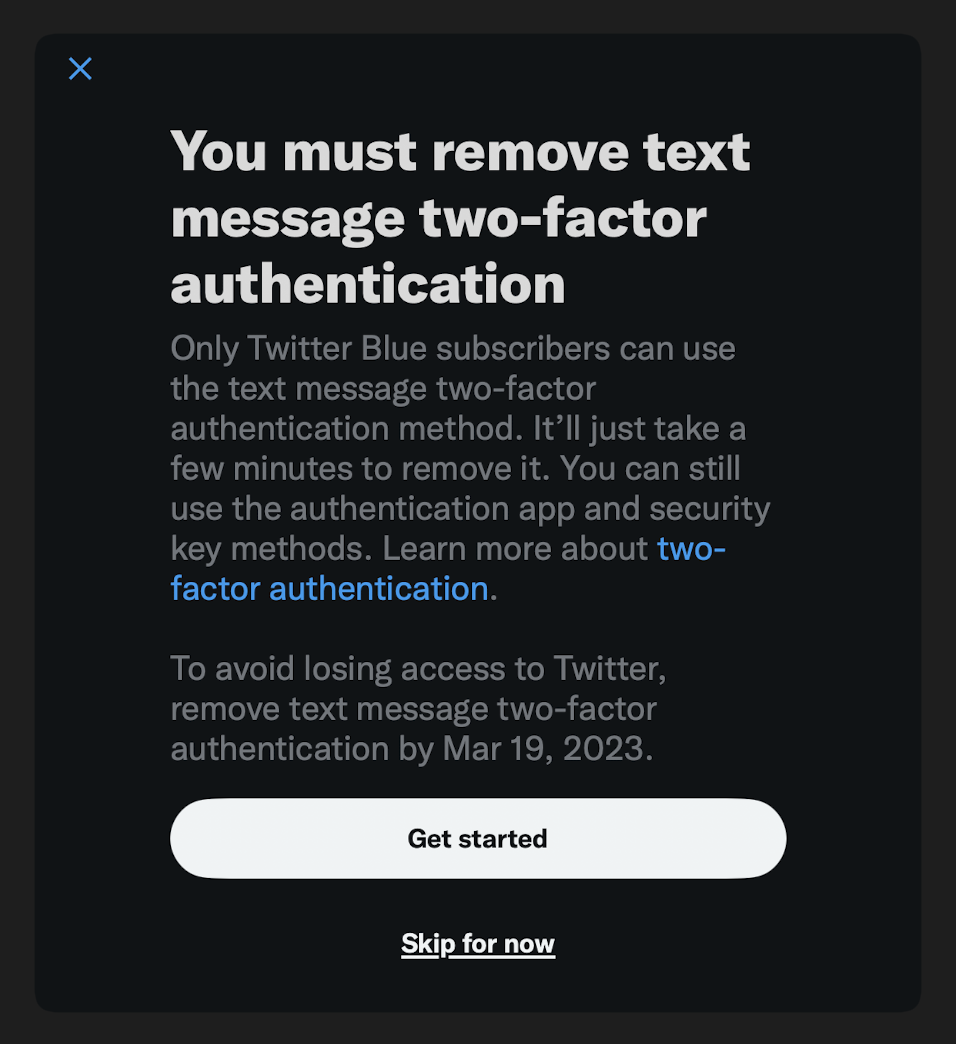
Twitter’s Decision to Limit SMS 2FA is Dangerous
Some background on me: I’m a software engineer working in what I call “usable security”. I’m passionate about this field because advancements can tangibly improve people’s lives, making their computing experiences easier and accounts more secure at the same time. This post contains some of my personal thoughts. It does not represent anyone else or [...]
'Zero Login:' The Rise of Invisible Identity
Will new authentication technologies that recognize users on the basis of their behaviors finally mean the death of the despised password?
Announcing the Security Education Companion
The need for robust personal digital security is growing every day. From grassroots groups to civil society organizations to individual EFF members, people from across our community are voicing a
Account compromise of “unprecedented scale” uses everyday home devices
Credential-stuffing attack uses proxies to hide bad behavior.

Frequent password changes are the enemy of security, FTC technologist says
Contrary to what you've been told, frequent changes can be counterproductive.
Blog | 1Password
Expert articles, security news, product updates, guides, and research from 1Password on password management, privacy, and digital security.
1Password
1Password is a multi-platform subscription-based password manager developed by AgileBits Inc. It is often used due to the combination of a master password with a...
How Apple, Google, and Microsoft will kill passwords and phishing in one stroke
You've heard for years that easier, more secure logins are imminent. That day is here.

New Gmail Attack Bypasses Passwords and 2FA To Read All Email - Slashdot
An anonymous reader quotes a report from Forbes: According to cyber security firm Volexity, the threat research team has found the North Korean 'SharpTongue' group, which appears to be part of, or related to, the Kimsuky advanced persistent threat group, deploying malware called SHARPEXT that doesn'...

Why The Only Secure Password Is One You Don’t Even Know That You Know
Researchers have shown how to teach a password subconsciously, then pluck it back out.
A Thought on PDS Administration - Clinton's Other Blog
PDS_ADMIN_PASSWORD needs a lift
Passwords, Secrets, and Access Management | 1Password
Protect passwords and secrets, manage app access, and secure AI tools with 1Password. Easy to adopt from growing teams to enterprise.
mp | Github 2FA, git push, and password entry
Activating github two-factor authentication (2FA) offers an indubitable security boost, with one notable side effect--https authentication requires entering a Personal Access Token instead of password. This entry explains how I reconfigured my git push commands with 2FA to be able to enter my password once again, instead of a random 32-character token.
I've been saying for nearly a year that getting the UX right for bsky's OAuth deployment is a major inflection point for reinforcing users mental models If we phrase things right, people will learn that this password UX controls access to my identity + slices of my atmosphere data (via my PDS)

Paul Rohr
Claude is inheriting a centralized app-centric bias here (which existing OAuth profiles may share) To wind up in a decentralized world where all "my data" lives on "my PDS" -- regardless of how many atproto apps I authorize to store stuff there for me (see 🧵) -- we should invert that paradigm