


Five memory corruption bugs in nginx, called nginx2root, can let an unauthenticated attacker run code on a server. Here’s how they work.
Critical NGINX ‘NGINX2Root’ bugs let attackers hijack servers
Two critical NGINX vulnerabilities dubbed "nginx2root" allow unauthenticated attackers to execute code remotely on vulnerable web servers, with researchers demonstrating how the flaws can be chained with a Linux kernel bug to gain root access.
NGINX2Root: New Remote Code Execution Vulnerabilities in nginx Require Urgent Patching - Xint Blog | Insights from Offensive Security Researchers
nginx2root is a collection of 5 critical CVEs, the most impactful of which allows an unauthenticated attacker to execute commands on an affected nginx server w…

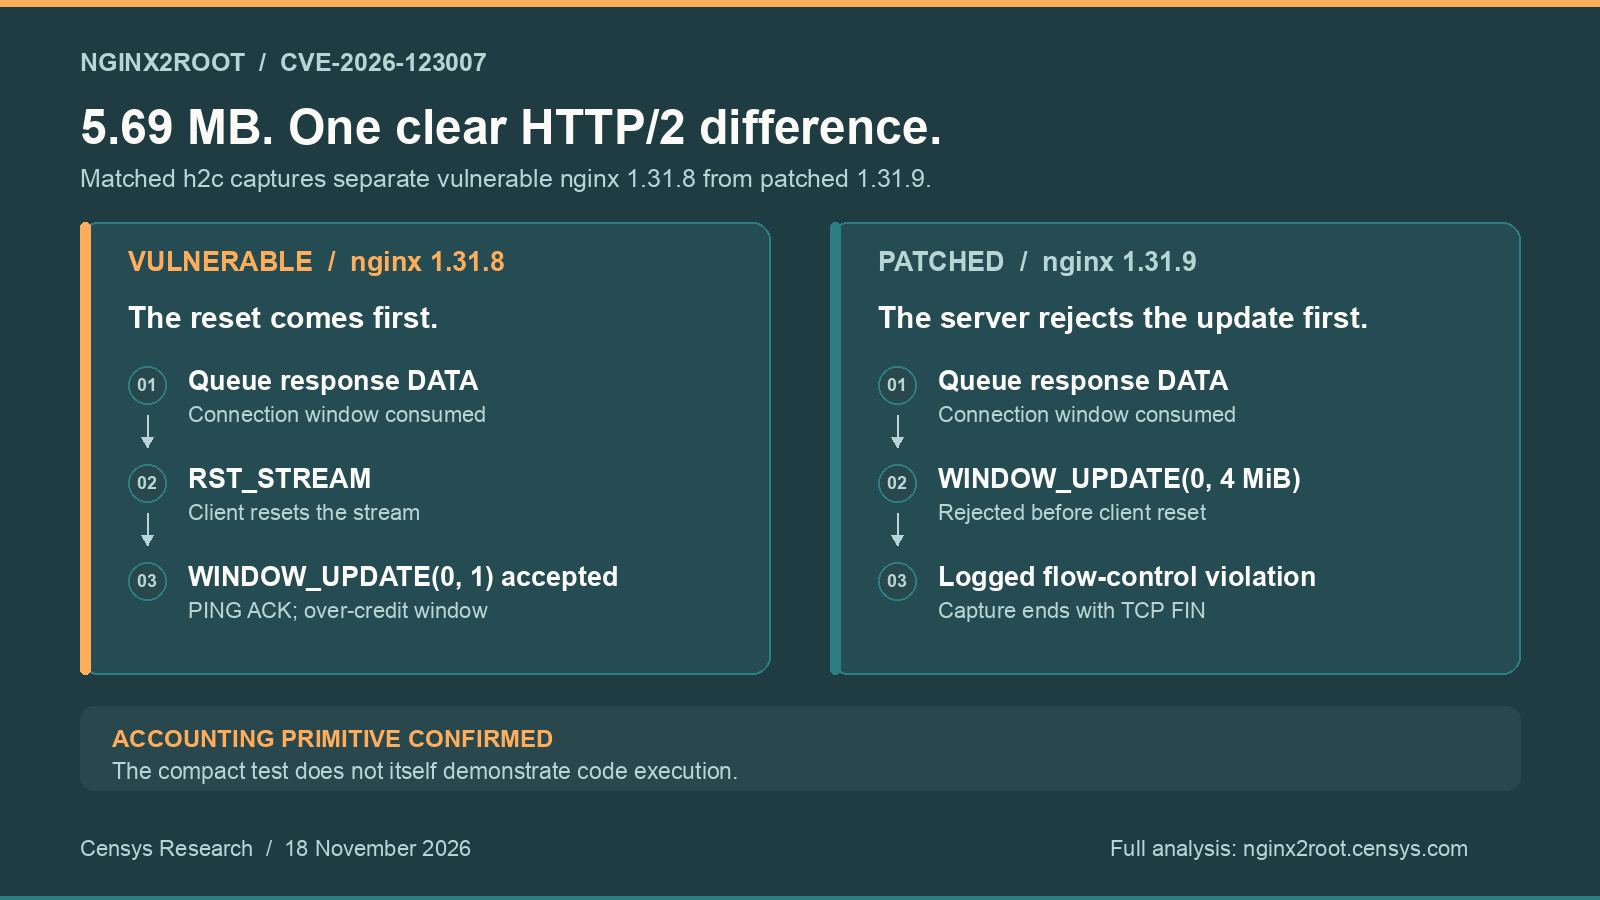
nginx2root: A simple test for the HTTP/2 flaw and three use-after-free reproductions - Censys
Executive Summary Background On 18 November 2026, Xint disclosed five nginx vulnerabilities called nginx2root. Each vulnerability affects memory in an nginx worker process and requires a specific feature: HTTP/2, reverse proxying over HTTP/2 or HTTP/3, runtime DNS resolution with subrequests, or mail proxy authentication. Xint stated that any of these allows an unauthenticated attacker to […]
NGINX2Root by Xint — From nginx visitor to root of the server host
Xint discovered five nginx vulnerabilities, including CVE-2026-123007. From unauthenticated RCE to host root, chained with a kernel exploit.
Unauthenticated Remote Code Execution in NGINX: CVE-2026-123633 and CVE-2026-123007 | Wiz Blog
Two critical HTTP/2 flaws can allow attackers to compromise NGINX servers, putting the websites, APIs, and sensitive data they handle at risk.

Cloudflare deploys protections against php2shell vulnerability
Cloudflare has deployed default web application firewall (WAF) protections for newly disclosed PHP vulnerabilities before public disclosure. The rules use request and response signals to stop exploit attempts and prevent exposed data from reaching attackers.

Cloudflare deploys protections against php2shell vulnerability
Cloudflare has deployed default web application firewall (WAF) protections for newly disclosed PHP vulnerabilities before public disclosure. The rules use request and response signals to stop exploit attempts and prevent exposed data from reaching attackers.
Cloudflare
Welcome to the Cloudflare - Powering the next generation of applications

A fully programmable secure web gateway
Cloudflare Gateway and Data Loss Prevention have inherited the flexibility and power of Cloudflare Workers through our full-stack integration with the Cloudflare Developer platform.

How Cloudflare WAF protects against ruby2shell (CVE-2026-132825)
ruby2shell lets attackers corrupt memory in default Rails and Sinatra apps without logging in. Cloudflare WAF blocks it for all customers, including Free plans.

Cloudflare for Startups | Cloudflare
Cloudflare is the leading performance and security company helping to build a better Internet. Today the company runs one of the world’s largest networks that powers more than %{GlobalWebsiteCountWords} million Internet properties.

Cloudflare R2
Cloudflare R2 is a cost-effective, scalable object storage solution for cloud-native apps, web content, and data lakes without egress fees.

Cloudflare DDoS Threat Report 2026 Q3: More swarms, fewer giants
Cloudflare mitigated over 8,200 DDoS attacks per hour in Q3 2026 as attackers shifted to shorter, high-frequency strikes. Explore the latest threat data, including the collapse of CLDAP vectors and the impact of recent botnet takedowns.

Introducing Quicksilver: Configuration Distribution at Internet Scale
At peak, Cloudflare’s network processes more than 14 million HTTP requests per second. We spend a lot of time thinking about the tools we use to make those requests faster and more secure.

Cloudflare OS Review: The Security-First AI Workspace That Wants to Be Your Company's Operating System
Cloudflare OS is not a traditional computer operating system. It is an AI productivity environment—an "operating system for the company"—that originally ran inside Cloudflare's own walls before being open-sourced under the Apache 2.0 licence in August 2026. The project emerged from a real internal need:
NGINX2Root

CVE-2026-123007, CVE-2026-123633, etc.
Censys Nginx2root Exposure Tracker
nginx security advisories
nginx2root: A simple test for the HTTP/2 flaw and three use-after-free reproductions - Censys
NGINX2Root: New Remote Code Execution Vulnerabilities in nginx Require Urgent Patching - Xint Blog | Insights from Offensive Security Researchers
Critical NGINX ‘NGINX2Root’ bugs let attackers hijack servers
Unauthenticated Remote Code Execution in NGINX: CVE-2026-123633 and CVE-2026-123007 | Wiz Blog