(Updated 22 May 2020) This post discusses web security issues that I come across – so far thankfully mostly by reading about them. It is a work in progress which I’ll keep updating. The…
Today's PHP Security Release, and How We're Strengthening PHP Security
Describing the story behind how critical security vulnerabilities were found and fixed.
Today's PHP Security Release, and How We're Strengthening PHP Security
Describing the story behind how critical security vulnerabilities were found and fixed.
Today's PHP Security Release, and How We're Strengthening PHP Security
247 votes, 49 comments. We have posted more information about today's security releases, including the sequence of events that led to the discovery…
WebAppSec/Secure Coding Guidelines - MozillaWiki
The purpose of this page is to establish a concise and consistent approach to secure application development of Mozilla web applications and web services. The information provided here will be focused towards web based applications; however, the concepts can be universally applied to applications to implement sound security controls and design.
My First 10 Minutes on a Server | Hacker News
It covers 10x what all the other guides cover in terms of server and application security. It was posted a few weeks ago on HN but didn't make the front-page.
Award-winning security research reveals a host of never-seen, currently unblockable web-tracking techniques
Who Left Open the Cookie Jar? A Comprehensive Evaluation of Third-Party Cookie Policies won the Distinguished Paper prize at this year's Usenix Security Conference; its authors, researchers at Belgium's Catholic…

The Web Authentication Arms Race – A Tale of Two Security Experts – SLaks.Blog
Web authentication systems have evolved over the past ten years to counter a growing variety of threats. This post will present a fictional arms race between a web application developer and an attacker, showing how different threats can be countered with the latest security technologies.
Cybersecurity Notes
Welcome to my blog! There's a lot here and it's a bit spread out, so here's a guide:
The reckless, infinite scope of web browsers
This blog post was published on March 18, 2020. It might be out of date, have broken images or links, or simply contain bad ideas and opinions that didn't stand the test of time. Please read generously!
Getting Started with Exploit Development
This post has been updated https://dayzerosec.com/blog/2024/07/11/getting-started-2024.html Removing the Open Security Training from my recommendations kinda messed with the flow of these recommendations. So it triggered me to rework all the recommendations with updated resources. I'm leaving this post relatively untouched for anyone who was referencing it but I'd recommend the new one for anyone just getting started. tl;dr The rest of this goes into detail about what topics matter and why fr

arkenfox/user.js
Firefox privacy, security and anti-tracking: a comprehensive user.js template for configuration and hardening
The post-quantum future of web privacy
Cryptographic protocols help keep web sites safe from abuse while keeping their users private. Here's a look at the quantum threat to these protocols.

Mylar
Response to "Breaking web applications built on top of encrypted data" (CCS 2016) by P. Grubbs, R. McPherson, M. Naveed, T. Ristenpart and V. Shmatikov.
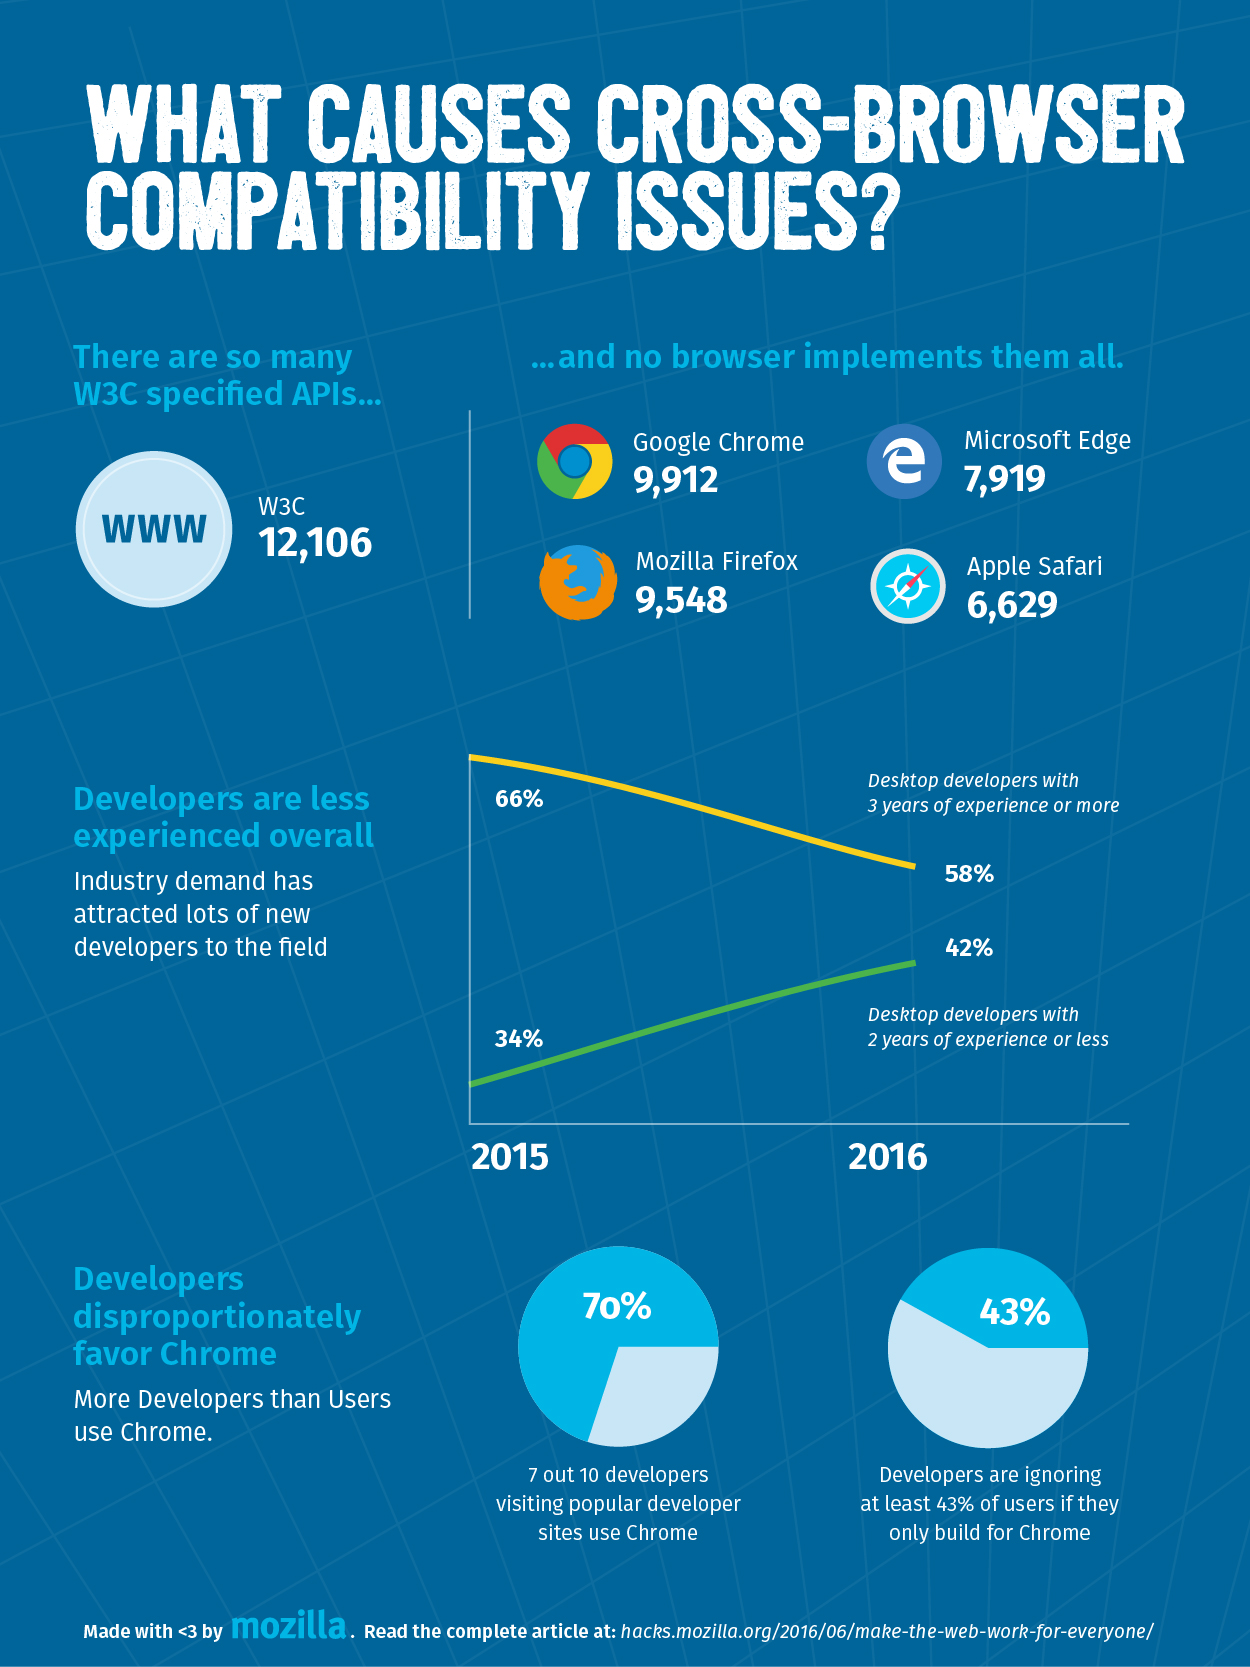
Make the Web Work For Everyone – Mozilla Hacks - the Web developer blog
Updated 2016/07/22: Commenters found a few data errors (thanks!) which have now been corrected. Millions of websites have compatibility problems on one or more of the major browsers, leading to ...
Blog | 1Password
Expert articles, security news, product updates, guides, and research from 1Password on password management, privacy, and digital security.