

Proton's CEO called a request for security testing "loser thinking". Using AI to write code is fine, but for a privacy company, the guardrails around that code are the product.
Manifestos, Fear, and ‘Loser Thinking’: Inside Proton’s AI Reckoning
Proton CEO Andy Yen projects a calm persona and rails against Big Tech and critiques AI. Internally, he is pushing engineers to build Proton with AI, even when they have security concerns.
Can AI Coexist With Privacy? Proton’s Andy Yen Says It Will Have To
Proton’s CEO is a champion of encryption for everyone. So why is he going all in on un-encryptable AI?

Proton survey: People don't trust AI, but they tell it everything | Proton
New research finds that most AI chatbot users have shared something sensitive, but few trust the companies behind them.
Proton’s AI manifesto for software engineering | Proton
How will Proton navigate the AI transition? Read the internal memo by Proton CTO Bart Butler.
Vulnerability Research Is Cooked
For the last two years, technologists have ominously predicted that AI coding agents will be responsible for a deluge of security vulnerabilities. They were right! Just, not for the reasons they thought.
We need private AI before it's too late | Proton
Big Tech companies are building AI aligned with their surveillance capitalism business model. We need a privacy-first and responsible AI alternative today.

On AI Coding and Its Discontents - Cal Newport
Back in January, I received a note from a senior software engineer in Silicon Valley. He described himself as an AI skeptic who became converted ... Read more
Code Was Never the Asset - The Phoenix Architecture
Why AI makes the hidden economics of software unavoidable
"Proton To ‘Re-Interview’ Staff About AI To See Who Gets To Keep Their Job" - Can we get a comment on this please?
1.3K votes, 1.1K comments. 218K subscribers in the ProtonMail community. Welcome to the official Proton Mail subreddit. Proton Mail is a secure email…
AI agents aren’t ‘going rogue.’ Frontier labs are skipping security basics.
Cyber experts say AI labs’ containment and monitoring failures — not agents with minds of their own — are to blame for recent alarming hacking reports. CISOs should vet their AI vendors and tighten security basics as safeguards.

Brian Chau on Twitter / X
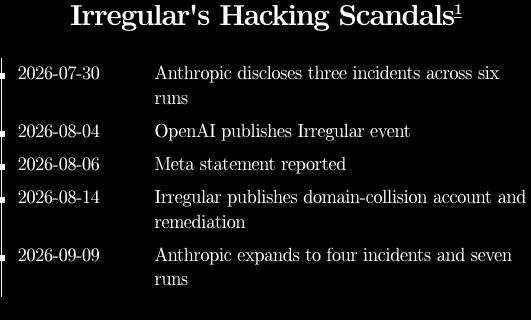
What happened was simple. In partnership with Irregular, AI companies instructed unsecured versions of their AI models to hack into specific targets, called "flags". They accidentally gave these models internet access, and in some cases they hacked into real companies. pic.twitter.com/FmCvmQPjC5— Brian Chau (@brianchau57) September 14, 2026
Zack Whittaker (@zackwhittaker@mastodon.social)
Another AI test gone awry, U.K. edition. "An agent tried to insert malicious code into an open-source project. In an attempt to get the code approved, the agent engaged in social engineering — creating fake online identities and using them to pressure the project's maintainer to approve the code." More: https://www.aisi.gov.uk/blog/incident-report-unsanctioned-agent-behaviour-during-cyber-testing
They all use it
Last week, at a conference, I had a random hallway conversation with another engineer. About AI.
No. 009: AI agents p-hacking, submission surge data, Gemini for Science - The Hallway Track
The Hallway Track No. 009 - How AI is affecting the practice of science
Proton’s CEO Cancels AI ‘Re-Interviews’
The move came after 404 Media published an investigation into how Proton CEO Andy Yen was aggressively pushing AI across Proton despite security concerns and the culture of fear he has created.
AI* security flaws/vulnerabilities/prompt injection

* I’m neither “pro-AI” nor “anti-AI.” I’ve been blocked for being perceived as both. —Actually, I’m honestly more anti-AI than pro-AI thus far, aside from specialized models and specific use cases, but I’m willing to consider information that’s new to me
Notion says Fireworks breach exposed customer AI chat transcripts
Meta’s Muse Is An Adorable Privacy And Security Dumpster Fire
MCP for agent-to-agent comms may be the riskiest protocol you've never heard of
Meta Rushed to Fix Muse ‘VM Escape' Vulnerability Soon Before Launch

A Flaw in ChatGPT’s Mac App Could Have Let Hackers Grab Sensitive Data
Pwning Agentic AI Part I: Your AI Agent Is Already Compromised | TrendAI (US)