

drops the leaked eMudhra root from the fallback certificates
eMudhra Statement on distrust of select Global TLS Intermediate and one Root CA
eMudhra Limited (NSE: EMUDHRA | BSE: 543533) today issued a statement on recent reports about the distrust of some of its intermediate Certificate Authorities (CAs) used in its global TLS business.
647959 - Add Honest Achmed's root certificate
RESOLVED (kathleen.a.wilson) in CA Program - CA Certificate Root Program. Last updated 2026-04-24.
Eight Bits of Trust; eMudhra's CA keys cracked in milliseconds
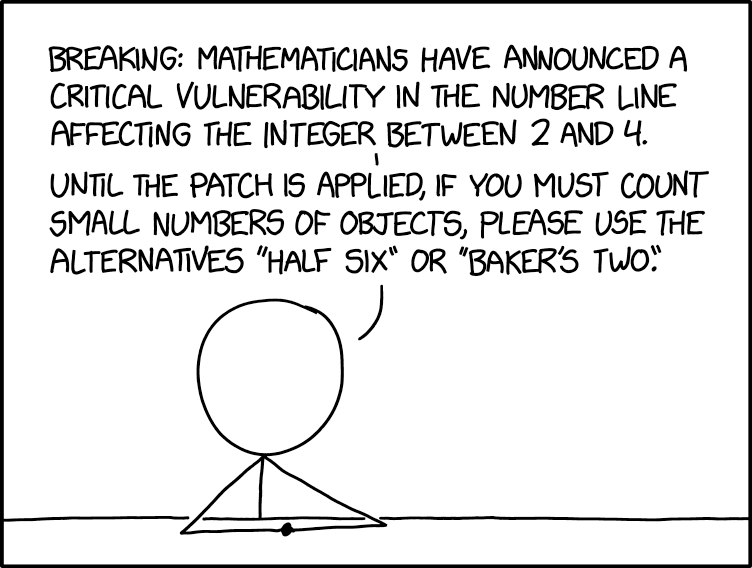
One of eMudhra's certificate authority private keys is the number 4. Not a number that starts with 4, or the number 4 followed by a few hundred random digits, just, 4... Another one is 56, and another is 115. I know, because I recovered all of them from their

wisp.place - Static Hosting on AT Protocol
Deploy static sites on AT Protocol. Your site lives in your PDS. Global CDN included. Push updates instantly. Forever free.
The GENIUS Behind Wisps Production (How to Make a Wisp Type Beat)
Wimster9030 🇪🇺 🇧🇪 (@wimster9030.wsocial.eu)
I know, Daniel, but that's not the way WSocial "sold" it to us. We could only access trough ID-verification so we know for 100% they are EU and a "real person". That was the whole point. So we went trough that process, but now it seems that the backdoor are the other ATProt platforms to get in too.

Robin Berjon (@robin.berjon.com)
*Breaking* just as I'm writing this I hear that someone made a tool for W users to check if they're in the leak: wdonthavetime.tngl.io/wsocial-wned/.

Vulnerability
Other numbers are largely unaffected, but anyone using '4' for their certificate key is urged to upgrade to '5'.
Big Tech’s Anti-Labor Playbook Has Come for Wikipedia
TLDR: In ten days last month, the Wikimedia Foundation fired the longtime lead developer of MediaWiki and disbanded the team whose entire…
I think I found an issue with the existing Bluesky OAuth permission sets @matthieu.bsky.team @bnewbold.net: github.com/bluesky-social/atproto/issues…. The XRPC endpoints specified in `authViewAll` are inconsistent about aud. Minimal repro here. tangled.org/tylerjfisher.com/repro-bluesk… Might be doing something wrong, lmk!

Bluesky permission sets require inconsistent aud parameter · Issue #4850 · bluesky-social/atproto
github.comveritiles v0.3 is out 🚀 The proof format is now DASL + AT Protocol compatible from the ground up, using raw/dag-CBOR CIDs, DRISL descriptors and MASL bundles. github.com/guillaumemichel/veritiles @dasl.ing @atproto.com
GitHub - guillaumemichel/veritiles: Verified map tiles: fetch PMTiles byte ranges from any untrusted HTTP host and cryptographically verify every byte against a content identifier before your map renders it. Zero dependencies; drop-in pmtiles Source for MapLibre GL, Leaflet, and OpenLayers.
github.comThis is an absolutely astounding press release from eMudhra. No apology, a suggestion that the researcher who found their private keys must have used AI, and an attempt to shift blame to auditors... wow. emudhra.com/en/press-release/emudhra-stat…

eMudhra Statement on distrust of select Global TLS Intermediate and one Root CA
emudhra.com


