

every version of PHP for the past 17 years has two critical bugs and now 74.5% of the internet is broken lol. there's a patch coming out tomorrow but until then most of the internet has open backdoors that allow unauthorized remote code execution. is this good
Oct 21, 2026 at 2:31 AM
Today's PHP Security Release, and How We're Strengthening PHP Security
Describing the story behind how critical security vulnerabilities were found and fixed.

Today's PHP Security Release, and How We're Strengthening PHP Security
Describing the story behind how critical security vulnerabilities were found and fixed.
PHP warns admins of two critical flaws, emergency patches coming tomorrow
The PHP security team is warning administrators to prepare for emergency security updates tomorrow to address two critical vulnerabilities, as information about the flaws has reportedly leaked ahead of their scheduled disclosure.

Today's PHP Security Release, and How We're Strengthening PHP Security
247 votes, 49 comments. We have posted more information about today's security releases, including the sequence of events that led to the discovery…
Chris Silverman 🌻 (@csilverman@mastodon.social)
Nothing puts the lie to "PHP is irrelevant" like "good morning, 70% of the internet needs to be fixed ASAP".
Opinion | Internet Hacking Is About to Get Much Worse (Published 2018)
We can no longer leave online security to the market.

Why everything was broken yesterday
Unsolicited tech advice about the two issues (PHP, compromised certificates) that, separately, each pose some security risks and are worth attending to.
Cloud Rats and Software Roaches (Idle Words)
We are entering an epoch where it may become easy for small pieces of self-replicating code to permanently infest Internet-connected devices in a way that is hard to undo. Such a world would be annoying to live in and we should take steps to forestall it.
Cloudflare deploys protections against php2shell vulnerability
Cloudflare has deployed default web application firewall (WAF) protections for newly disclosed PHP vulnerabilities before public disclosure. The rules use request and response signals to stop exploit attempts and prevent exposed data from reaching attackers.

Robin Berjon (@robin.berjon.com)
Again, we can try to be generous. But this fits a pattern. When people found issues in their open source code, instead of fixing them they went closed source. When they had an XSS vulnerability right at launch it took over a day for them to acknowledge and close it.

PHP CVE-2026-109618 and CVE-2026-109619: how to apply the patches
Install the fixed PHP for CVE-2026-109618 and CVE-2026-109619 on Ubuntu, Debian and RHEL, restart the right processes, and roll back the early mitigations.
Using Claude to reduce the attack surface of code
Automated attack surface analysis and reduction can meaningfully improve the security of deployed software in the near term. In this post, we preview data we’ve collected from applying attack surface reduction techniques to large open-source codebases using Claude.

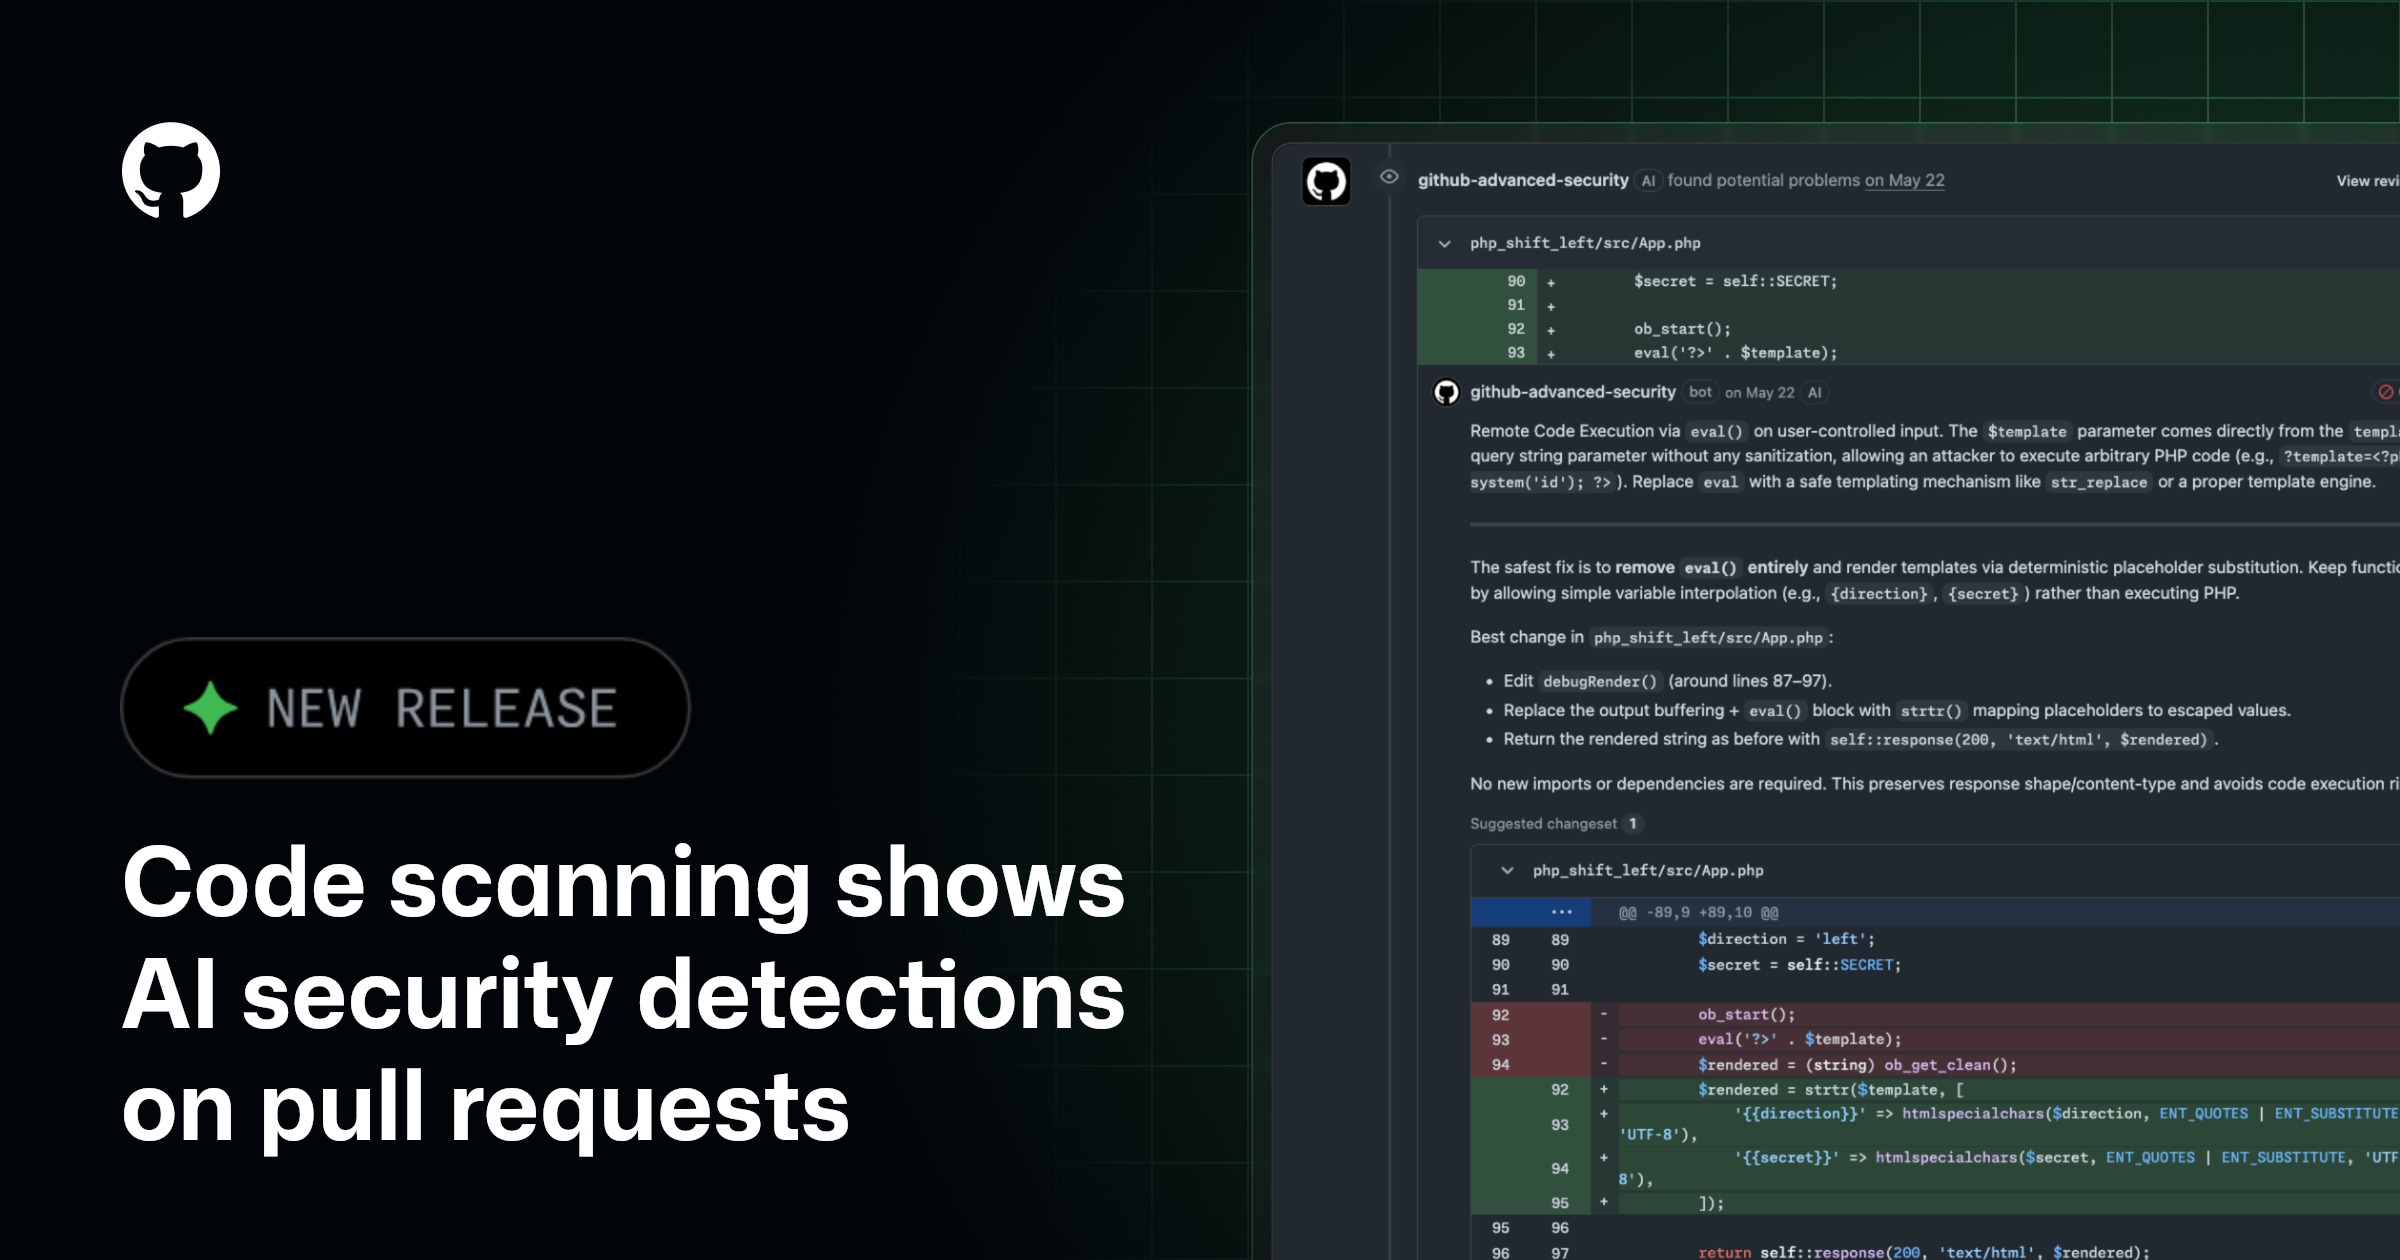
Code scanning shows AI security detections on pull requests - GitHub Changelog
GitHub code scanning now surfaces AI-powered security detections directly on pull requests, expanding vulnerability coverage to languages and frameworks not currently supported by CodeQL. These detections help teams identify and…
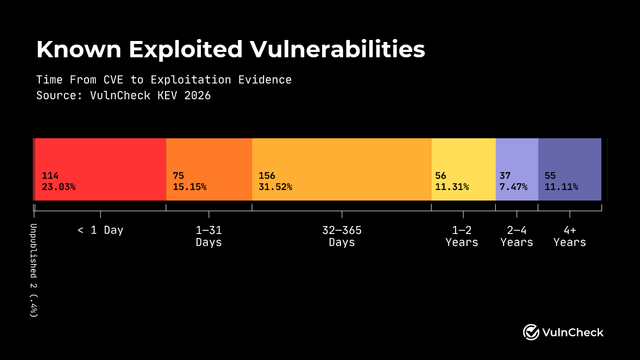
Just a rumour of a bug is enough to find a security exploit these days
Thinking through how the conventional OSS security embargoes no longer buy us time, and what open source maintainers might do instead to respond
shitposts aside, this one is serious, my loves: if you’re just waking up and you have any service online running PHP 5.4 to latest, you need to take it down RIGHT NOW and don’t put it back online until after it’s patched absolutely catastrophic vulnerability dropped in the middle of the night

