

@dholms.at thinking about permissiones data. What if: Permissioned data URI was at://<PDS did>/<record type>/<rkey> exactly the same as public data. The PDS would handle the space assignment opaquely and do a 4xx response with some space aturis. Client goes and grabs a space cred and retries
Jul 20, 2026 at 9:13 PM
Permissioned Spaces - WG.1
@Permissioned Spaces Expressive Authorization at the PDS @verdverm.com | @blebbit.app

Permissioned Spaces - WG.1
@Permissioned Spaces Expressive Authorization at the PDS @verdverm.com | @blebbit.app
Spaces · vlpds docs
Permissioned data on vlpds: every member keeps a private, signed space repo on their own PDS. It never reaches the firehose, and reading it takes a short-lived credential chain.
Spaces as Layers - Nick's Blog
Public anchor records paired with sidecar records in permissioned spaces give ATProtocol apps a composable pattern for blending open discoverability with controlled access.
Permissioned data by dholms · Pull Request #94 · bluesky-social/proposals
This is an initial proposal for permissioned data. Details, terminology, and behaviors are all likely to change. For a friendly introduction to the protocol, check my my Leaflets. For discussion, f...
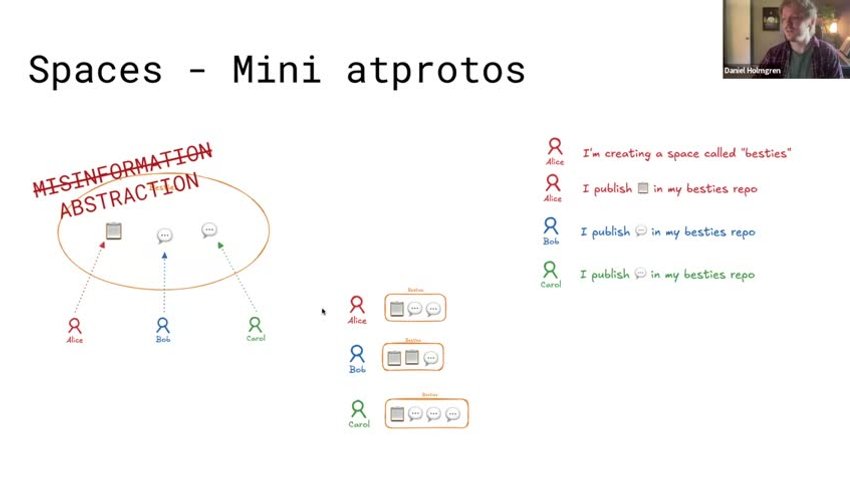
FediForum Talk: Introduction to Atproto Spaces
By Daniel Holmgren, head of protocol at Bluesky PBC. A technical overview of the recent extension of AT Protocol beyond public data to cover permissioned data and private group spaces.
Permissioned Data Diary 2: Buckets - Daniel's Leaflets
The second in a series of posts building up a solution to permissioned data on atproto. We introduce buckets: a new protocol primitive for creating a shared social context.
I've been exploring permissioned data spaces technology and components, thinking about what the end-result is going to look like. @dholms.at's last dev diary has some good nuggets and I decided to jump into an ECMH implementation.

ngerakines.me/ecmh-rs
tangled.orgSharing this! Wish I'm not late for #IETF126 Tangled found PDS doesn't fit well for contributions even with upcoming permissioned space spec. So, we are planning to store record-like data outside of PDS, in Knot. This is a post explaining the reasons & upstream spec change we need. #atproto #atdev
tangled-cob.md · by boltless.me
tangled.orgnew data diary! this is the most in the weeds yet, all revolving around our proposed URI structure for permissioned data. turns out you can figure out a lot about a protocol from the uri! as always, let me know what you think :)

Permissioned Data Diary 5: What’s in a Name?
dholms.leaflet.pubA deep dive on permissioned-data space access. The dials, policies, and the difference between handing out keys and revoking them.

Permissioned Data: Space Access
ngerakines.leaflet.pub#atproto space question: Is it fine to create space for each records to support per-record access control? Say all Tangled repository issues are spaces. My biggest concern is sync, because every issues are now standalone permissioned repos. But maybe that doesn't matter much?
Spaces explainers

Search terms: AT Protocol Spaces, ATProto Spaces, permissioned data, buckets
Permissioned Data Shapes: Self-Only Bookmarks - Nick's Blog
The Atproto Spaces Alpha is Live - AT Protocol
Reintroducing Spaces - Daniel's Leaflets
Permissioned Data Diary 1: To Encrypt or Not to Encrypt - Daniel's Leaflets


