

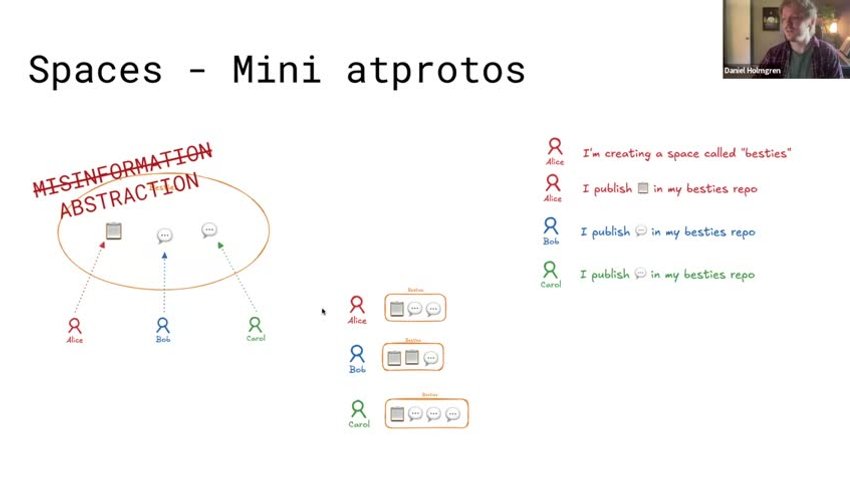
FediForum Talk: Introduction to Atproto Spaces
By Daniel Holmgren, head of protocol at Bluesky PBC. A technical overview of the recent extension of AT Protocol beyond public data to cover permissioned data and private group spaces.
atproto made simple: granular permissions - underreacted
Evaluating permissioned spaces for community contexts - meri's missives
A look at Bluesky's proposed approach to private data on ATProto
The Atproto Spaces Alpha is Live - AT Protocol
Atproto Spaces, formerly known as “the permissioned data protocol,” is a new extension to atproto that enables non-public data. The alpha is now officially open. Here’s how to develop with it and what to expect as we work towards the full release.
The Atproto Spaces Alpha is Live - AT Protocol
Atproto Spaces, formerly known as “the permissioned data protocol,” is a new extension to atproto that enables non-public data. The alpha is now officially open. Here’s how to develop with it and what to expect as we work towards the full release.
The Atproto Spaces Alpha is Live - AT Protocol
Atproto Spaces, formerly known as “the permissioned data protocol,” is a new extension to atproto that enables non-public data. The alpha is now officially open. Here’s how to develop with it and what to expect as we work towards the full release.
Atproto spaces · aturi.to
Browse your permissioned atproto data: records kept outside your public repo.
Reading Proposal 0016: What atproto’s “Permissioned Data” Actually Does - Nick's Blog
AT Protocol is public by default. Everything you write goes into a signed, archived, and rebroadcastable repository that anyone can read from and moves throu…

Understanding ATProtoFans: A Technical Deep Dive into Verifiable Creator Support - ATProtoFans Blog
ATProtoFans - Support Your Favorite Creators
Decentralized supporter attestation service for the ATProtocol ecosystem. Support creators with cryptographically verifiable relationships.
ATProtoFans - Support Your Favorite Creators
Decentralized supporter attestation service for the ATProtocol ecosystem. Support creators with cryptographically verifiable relationships.
#atproto space question: Is it fine to create space for each records to support per-record access control? Say all Tangled repository issues are spaces. My biggest concern is sync, because every issues are now standalone permissioned repos. But maybe that doesn't matter much?
continuing to build up our permissioned data protocol! this one asks what a bucket actually is and where the data that constitutes a bucket is stored. it argues for maintaining the atproto ethos in the permissioned data protocol as always, looking forward to hearing your thoughts!

Permissioned Data Diary 3: Your Bucket, My Data
dholms.leaflet.pub

