

Notes On Epstein's Emails
_ With the seemingly momentous dumping of what appears to be millions of emails from the infamous Epstein saga by the Department of Justice, we are witnes...

How an Élite University Research Center Concealed Its Relationship with Jeffrey Epstein
New documents show that the M.I.T. Media Lab was aware of Epstein’s status as a convicted sex offender, and that Epstein directed contributions to the lab far exceeding the amounts M.I.T. has publicly admitted.
Jeffrey Epstein, Blackmail and a Lucrative ‘Hot List’ (Published 2019)
A shadowy hacker claimed to have the financier’s sex tapes. Two top lawyers wondered: What would the men in those videos pay to keep them secret?

W Social – Public Beta Launch
W Social, public institutions and the theater of European digital sovereignty | Hacker News
And weirdly, there was never a peep about this in the press - while the W Social launch was on national news and a bunch of high-profile EU politicians immediately joined. What's going on here?
The hacker crackdown: law and disorder on the electronic frontier
A journalist investigates the past, present, and future…
One Nation Under Blackmail: The Sordid Union Between Intelligence and Crime that Gave Rise to Jeffrey Epstein$dVol. 1
Cover Page -- Title Page -- Copyright -- Publisher's Foreword -- Contents -- Introduction -- 1) The Underworld -- 2) Booze and Blackmail -- 3) Organized Crime and the State of Israel -- 4) Roy Cohn's "Favor Bank" -- 5) Shades of Gray -- 6) A Private CIA -- 7) A Killer Enterprise -- 8) Clinton Contra -- 9) High Tech Treason -- 10) Government by Blackmail: The Dark Secrets of the Reagan Era -- Documents -- Index -- List of Abbreviations -- Acknowledgments -- Back Cover

Donald Trump indictment: what are the classified documents?
A running update on information in the indictment as I go through it
Massive AfD data breach exposes illegally copied files
The “Alternative for Germany” party apparently suffered a data breach. Some 421,000 emails were published, offering a glimpse inside the party.

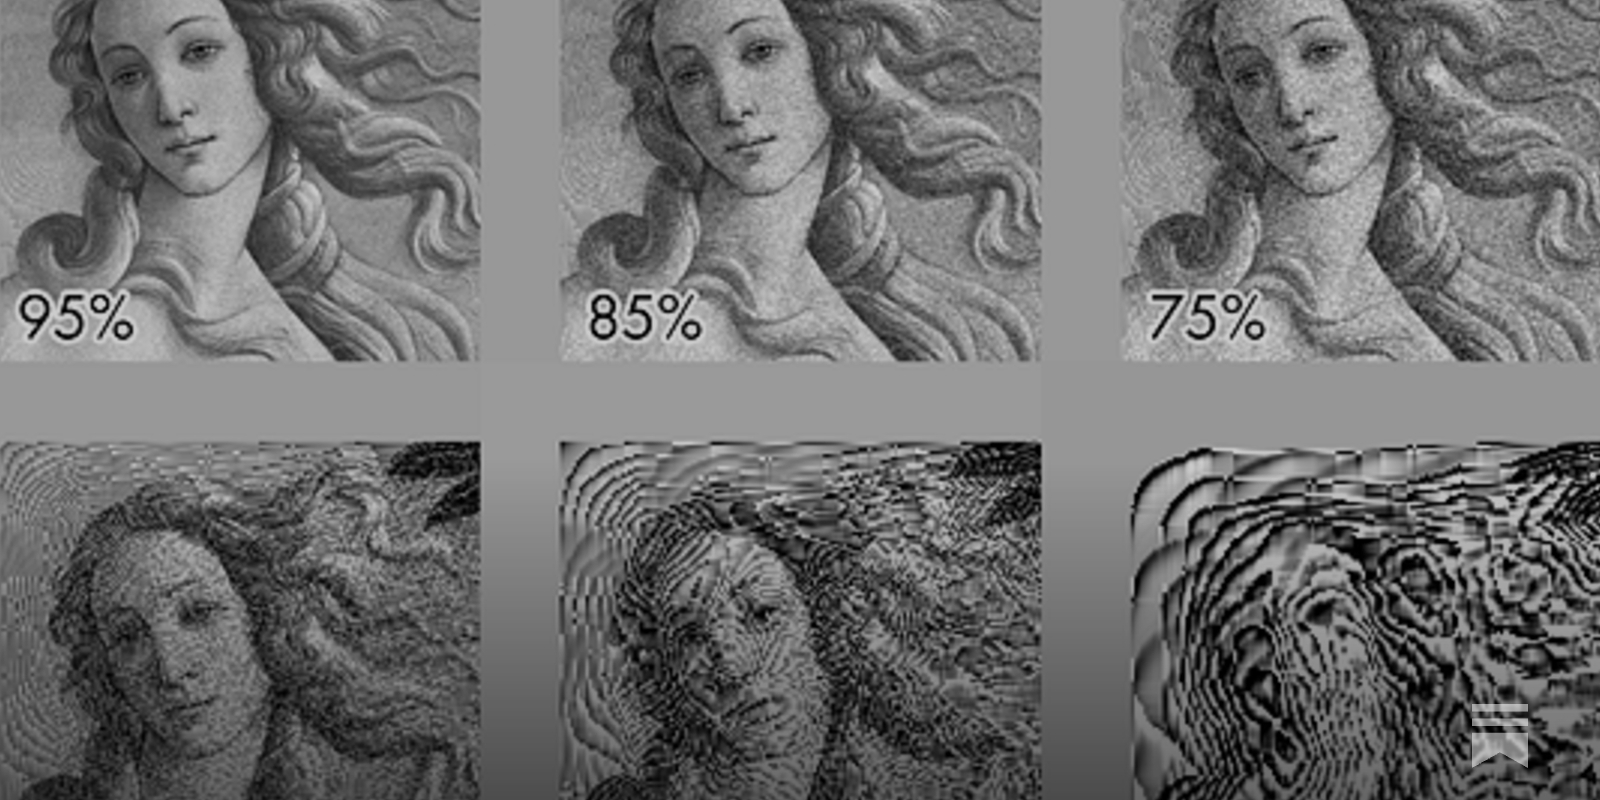
It's all a blur
If you follow information security discussions on the internet, you might have heard that blurring an image is not a good way of redacting its contents.
@palle.eurosky.social just published a powerful exposé about the #WSocial "it's not a leak if we intentionally publish it" ID data controversy. I highly recommend you read it (it's in German, but you could use your browser's translation tool): metacheles.de/w-social-datenskandal/ #WIdentity #GDPR

W Social: Verifiziert heisst veroeffentlicht
www.metacheles.deW Social published a "constitution" W supports freedom of expression then in the same breath says no pornography wsocial.news/constitution

W - The European social network for verified humans
wsocial.newsBut anyway, papers since you asked: - DOI:10.1371 Digital Social Norm Enforcement: Online Firestorms in Social Media - Deliberation and Identity Rules: The Effect of Anonymity, Pseudonyms and Real-Name Requirements on the Cognitive Complexity of Online News Comments doi.org/10.1177/0032321719891385
It looks like W Identity, the part of @wsocial.eu that checks your papers before you go in, has a very basic XSS on its admin backend, found hours after launch. This seems almost too predictable... Cyberfriends, any thoughts on how bad? 23.social/@kantorkel/116767220594438841
kantorkel (@kantorkel@23.social)
23.socialIs this a thing? Something about private data on AT Proto, where a person could purchase content and have a copy of said content injected into their Private Data, so it could not be removed without their consent? I’m thinking “I’ve bought a copy of a book, and now the book blob lives in my PDS”


