

This is an absolutely astounding press release from eMudhra. No apology, a suggestion that the researcher who found their private keys must have used AI, and an attempt to shift blame to auditors... wow. emudhra.com/en/press-release/emudhra-stat…

eMudhra Statement on distrust of select Global TLS Intermediate and one Root CA
emudhra.comOct 21, 2026 at 11:35 AM
eMudhra Statement on distrust of select Global TLS Intermediate and one Root CA
eMudhra Limited (NSE: EMUDHRA | BSE: 543533) today issued a statement on recent reports about the distrust of some of its intermediate Certificate Authorities (CAs) used in its global TLS business.
Eight Bits of Trust; eMudhra's CA keys cracked in milliseconds
One of eMudhra's certificate authority private keys is the number 4. Not a number that starts with 4, or the number 4 followed by a few hundred random digits, just, 4... Another one is 56, and another is 115. I know, because I recovered all of them from their

Updated: Data Breaches Caused by Leaks in 2024
We’re tracking data breaches that are most likely caused by leaked secrets and keeping this page up-to-date.
The Internet goes on high alert after discovery of 8 compromised TLS certs
Intermediate certs allow anyone to mint web credentials for any Internet server.

Gautam Kamath on Twitter / X
Nihar Shah did a heroic experiment for TMLR: he spent 20-25 hours over two weeks interviewing authors of seemingly low-quality submissions about their own papers. He confirmed what we all suspected: people submitting these papers have *no idea* what is going on in them. https://t.co/6CJF152u7I— Gautam Kamath (@thegautamkamath) September 16, 2026
Why everything was broken yesterday
Unsolicited tech advice about the two issues (PHP, compromised certificates) that, separately, each pose some security risks and are worth attending to.
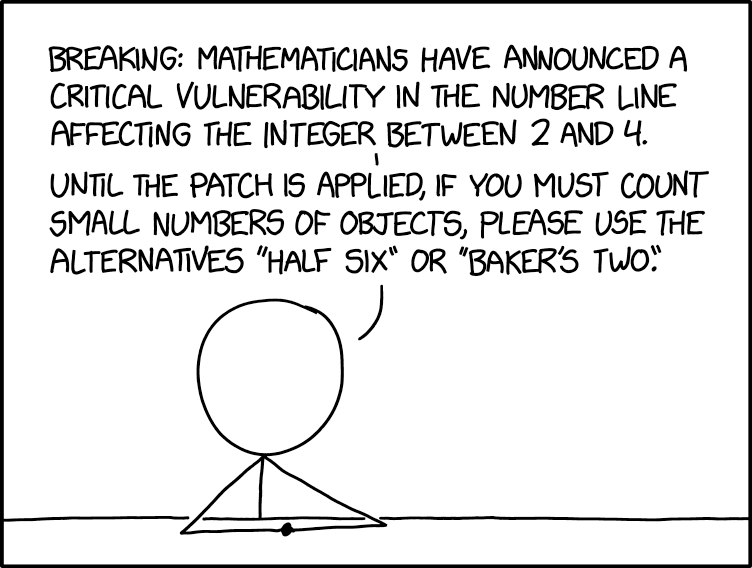
Vulnerability
Other numbers are largely unaffected, but anyone using '4' for their certificate key is urged to upgrade to '5'.
Encryption + Trust & Safety reading list (updated 2026-05-20)

Announcing the Centre for Cryptographic Trust Infrastructure
You’re getting this email because you subscribed to my blog posts at martin.kleppmann.com.
Eric Topol on Twitter / X
This is a FRAUDULENT paper, AI-generated. My name was used as an author and I had nothing to do with it, never saw it until today https://t.co/Ky60zJrMEZThe "Editors" Angelo Rossi Mori, David Mensah, and Zarnie Khadjesari should be reported. pic.twitter.com/2Z5CE8w4bn— Eric Topol (@EricTopol) April 22, 2026

Why “Trusted Publishing” Can’t Save Us from Social Engineering
Unmasking the risky illusion of npm's "trusted publishing" amidst recent cyber attacks.
Itai Yanai on Twitter / X
Is the scientific paper a fraud? Peter Medawar (Nobel Prize winner) suggested that publications are overly structured and formal, giving only a sanitized version of the discovery without revealing the thought process that actually led to it. pic.twitter.com/E3ttRPzcfL— Itai Yanai (@ItaiYanai) October 27, 2024

Really important to notice the sleight of hand here. Nobody reported that @wsocial.eu *leaked* the data (except for W Social saying in their denials that others reported this). We all agree this over-publication was done on purpose, by design, in a way that is not totally clear to everyday users.

heiseonline
Das soziale Netz W Social will sich mit einer Verifizierung aller Konten von der Konkurrenz abheben. Dass einige gesammelte Daten publik sind, sei kein Fehler. #Social Media
This is a FRAUDULENT paper, AI-generated. My name was used as an author and I had nothing to do with it, never saw it until today e-pubmed.co.uk/journals/digital-health-imple… The "Editors" Angelo Rossi Mori, David Mensah, and Zarnie Khadjesari and this "Journal" should be reported.
This is a FRAUDULENT paper, AI-generated. My name was used as an author and I had nothing to do with it, never saw it until today e-pubmed.co.uk/journals/digital-health-imple… The "Editors" Angelo Rossi Mori, David Mensah, and Zarnie Khadjesari and this "Journal" should be reported.


