

New: Revocation notices for the UCAN layer

Capability Trees: A Protocol-Level Extension of Object Capabilities, Draft 5
leaflet.pubApr 12, 2026 at 9:00 PM
UCAN - User Controlled Authorization Network
A trustless, secure, local-first, user-originated, distributed authorization scheme.
badge.blue — CID-First Attestation Specification
Specification for CID-first attestations on AT Protocol records. Inline and remote cryptographic signatures with replay-attack prevention.
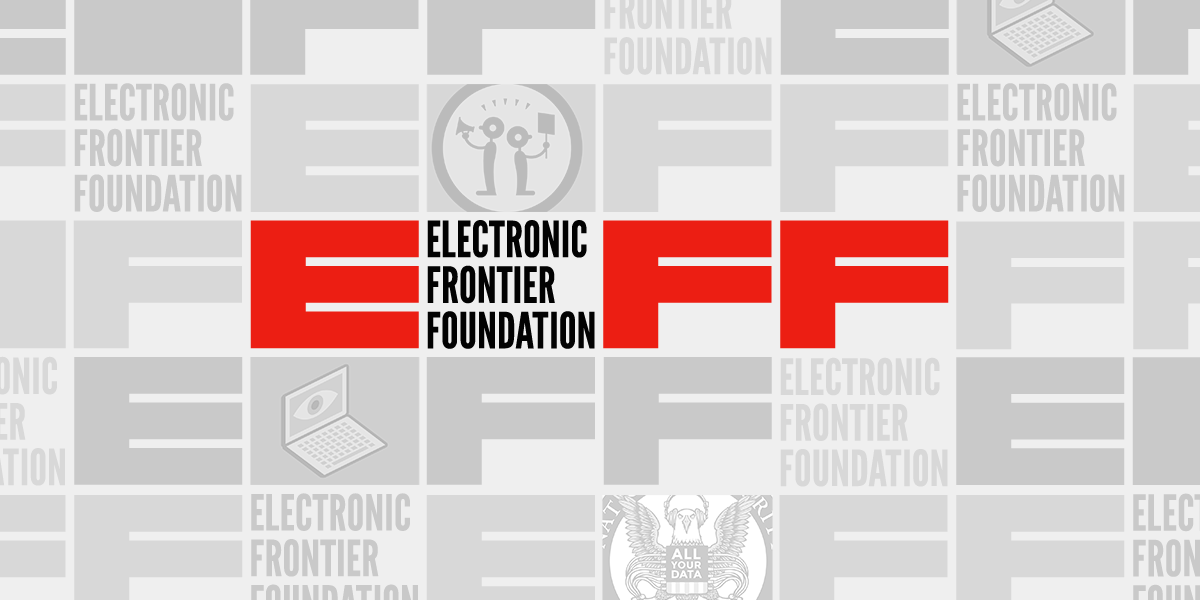
Comment and Control: Prompt Injection to Credential Theft in Claude Code, Gemini CLI, and GitHub Copilot Agent
Anthropic Claude Code Security Review, Google Gemini CLI Action, and GitHub Copilot Agent are vulnerable to prompt injection via GitHub comments — turning PR titles, issue bodies, and issue comments into attack vectors for API key and token theft.
UCAN Working Group
Decentralized Auth — User Controlled Authorization Networks - UCAN Working Group

Investigation into Message Layer Security (MLS)
This article investigates Message Layer Security (MLS), the IETF standard protocol (RFC 9420) for Signal-style end-to-end encryption. Through a practical analysis of OpenMLS (the Rust reference implementation) and a demonstration CLI chat application (mls-chat), the post reveals the substantial gap between protocol specification and production deployment. Introduction MLS (Message Layer …
The Evolving Language of PERA (Patent Eligibility Restoration Act)
A History of the Language of the Patent Eligibility Restoration Act (PERA); Section 101 of Title 35 of the United States Code

Head of copyright committee wants to deny EU creators the right to share - Creative Commons
Over the last few years the European Union has been working on revising its rules on copyright. But the latest proposal from the head of the copyright committee would deny creators the right to refuse remuneration — the right to share a work without getting paid — which could undermine the use of CC licenses…
New: Revocation notices for the UCAN layer
Capability Trees: A Protocol-Level Extension of Object Capabilities, Draft 5
leaflet.pubI hope @dholms.at or someone else at @bsky.app considers this before it's too late and ACLs are baked into the protocol.

Authority as Possession: Permissioned Spaces Deserve Better Than ACLs
leaflet.pub@leafplaza.eu just presented an official complain. Also, setup a whole chain of official follow ups on this complain. We know our rights, no other European ATP project has been giving the advantage W Social received and that goes against Commission Decision (EU) 2024/3083 - Art. 4.

Ursula von der Leyen
Warm Welcome to all followers on W 👌 User friendly 🔓 Open source AT Protocol 🔒 Privacy preserving 🧑🤝🧑 Humans only / No bots And 🇪🇺 European!
Yesterday we launched a new feature and now our existing web users can bring their own DID or we can be a temporary custodian of a new identity. Either way, now every user's PDS is the source of truth for public events and rsvps. openmeet.net/your-identity-your-events #ATprotocol

Your Identity, Your Events: How OpenMeet Gives Every User an AT Protocol Account
openmeet.netThe FOSDEM 2027 AT Protocol devroom proposal is taking shape. @edouard.paris and @viivi.rocks are leading the submission, due October 4. The draft covers protocol infrastructure, applications, governance, and critical perspectives. Share project ideas and use cases in the Discourse thread.
FOSDEM 2027 ATProto devroom proposal
discourse.atmosphere.community


