

I'm seeing a lot of different people, coming from different angles, recognize that the Same-Origin Policy is insufficient for the kind of apps that we want to make now, and that we need something more fine-grained and more secure. Very interesting times!
Sep 1, 2025 at 5:11 PM
Native Apps Should Be Avoided Whenever Possible — No One's Happy
Why native apps have become privacy liabilities, and why the browser is almost always the better choice.
Why Internet Infrastructure Decisions Rarely Stay Localized - Internet Society
Even narrow policy choices can have ripple effects that shape what people can access, how information moves, and who can participate online.

Why Native Apps Really are Doomed: Native Apps are Doomed pt 2
I recently wrote an article called “Native Apps are Doomed.” I was surprised at how many people were defending native apps. In all honesty…
Evolving AltStore PAL
In April of last year, we launched AltStore PAL in the European Union as one of the first official alternative app marketplaces on iOS thanks to the Digital Markets Act. We launched with just 2 apps — my Nintendo emulator Delta and clipboard manager Clip — yet Apple immediately changed their App Store rules to allow emulators worldwide for the first time ever.
Alex Moore on Open Web Advocacy and Why "Innovation Doesn't Come from the Gatekeepers"
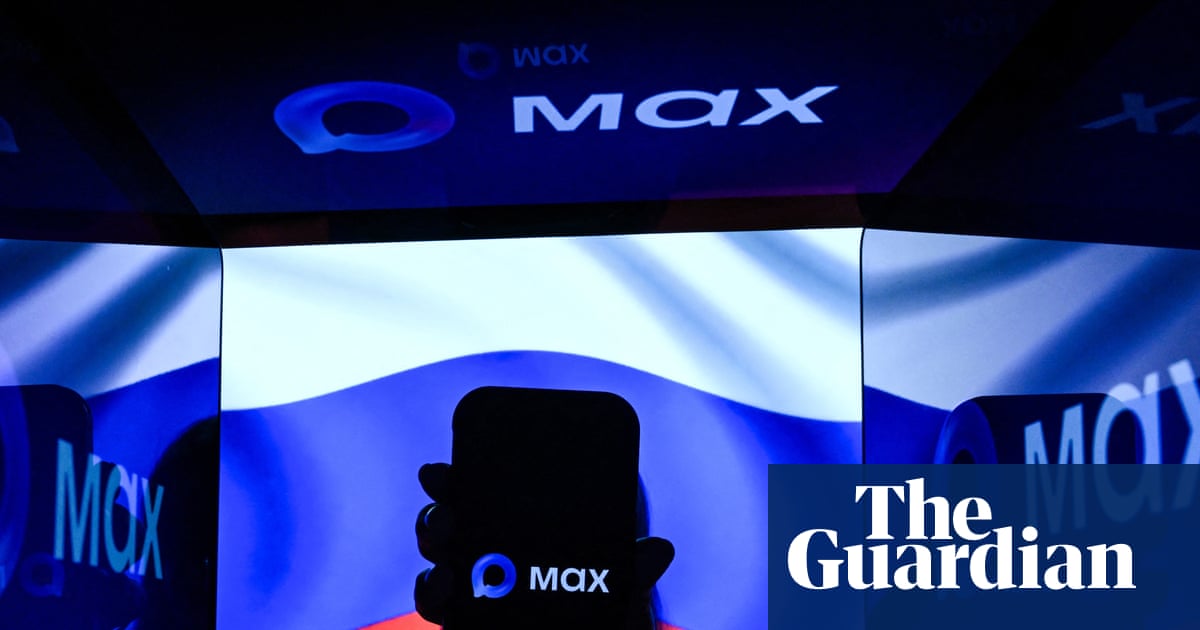
Revealed: how Russia uses mobile ‘super-app’ Max to spy on its citizens
Research shows tens of millions of people are being forced to use platform that amounts to ‘backdoor’ on their device
A new layer of security for certified Android devices
Starting in 2026 and in select countries first, Android apps must be registered to a verified developer in order to be installed.

Cross-Border Collaboration For Ip Protection.
Cross-Border Collaboration for IP ProtectionCross-border collaboration in IP protection occurs when multiple countries, corporations, or ins...
Origin Trials
Chrome origin trials allow developers to safely experiment with web platform features
Are we human?
Distributed app platform's proposed agreement 'isn't freedom respecting,' he says
The same-origin paradigm has unfortunately become a local maxima of the web. I'd argue the capture of the internet's search, social spaces, and data lock-in, as well as the lack of open protocols counter this capture can be directly attributed to building on top of the same-origin paradigm.

𝕮
Thinking about atproto as an identity and data *substrate* of the web. RSS couldn't go all the way because it built within the boundaries of the same-origin paradigm, just like the closed platforms that ended up enclosing most of the web.
Not even low-key, Access-Control-Allow-Origin: '*' everywhere is one of the best things that atproto has done. (I'm reasonably excited about this, in part because I've been waiting since shortly after it was proposed and first implemented. Here's a moan from 2010: x.com/blaine/status/13206867161?s=2…)
3) it still doesn't fully cover all use cases well or at all 4) bsky.app still didn't manage to implement OAuth at all Yes, we should all be moving to OAuth w/ scopes, that's the goal, but give people some slack, it's all still rather fresh, we'll get there… (yes, it's me, I'm those people)
Claude is inheriting a centralized app-centric bias here (which existing OAuth profiles may share) To wind up in a decentralized world where all "my data" lives on "my PDS" -- regardless of how many atproto apps I authorize to store stuff there for me (see 🧵) -- we should invert that paradigm

Paul Rohr
TL/DR = yes, it's a subtle conceptual shift: - from app-centric (apps control identity/data, delegating access to you at signin) - to identity-centric (you control identity/data, delegating access to apps at signin) Really looking forward to how the team evolves the OAuth UX to address this! /END


