

An interesting thing is happening to me at the moment. I have a standing bug bounty policy for my first authored scientific work. That means, I've committed to pay people who report bugs in my code, up to 750€ for severe errors. Since GPT-6 Astra came out, I'm now getting several bug reports daily.
Sep 11, 2026 at 7:27 AM
There Are No Bugs, Just TODOs | Almad's Changelog
One of my life’s traumas is the bug trackers, the issue trackers, the project management tools. The toolset that completes the version control log to form the development equivalent of double-entry bookkeeping.
What Happened to HackerOne?
The rise and fall of the largest bug bounty platform in the world
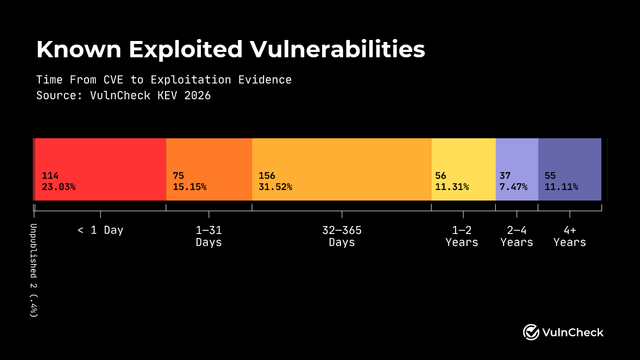
Just a rumour of a bug is enough to find a security exploit these days
Thinking through how the conventional OSS security embargoes no longer buy us time, and what open source maintainers might do instead to respond
Five US tech giants' hidden debts soar to $1.65tn on opaque AI funding
Data center leases, GPU supply contracts raise liabilities at Meta, Oracle, Nikkei study shows

GitHub’s one-dimensional view of open source contributions – Wes McKinney
TL;DR One of the most harmful parts of the GitHub platform is the code contribution calendar. This “hacker score card” overemphasizes the value of commits over the other kinds of important contributions to open source projects, like doing code reviews and discussing bugs and new features on the issue tracker.
Red Squares — the GitHub outage graph
A satirical contribution graph: red squares track GitHub.com platform outages instead of green squares tracking commits.
New AI Flaw Reporting System Fills Crucial Security Gap | CMU Software Engineering Institute
Flaw Reporting for AI (FLARE-AI) allows developers and security researchers to submit artificial intelligence flaws for formal, coordinated disclosure.
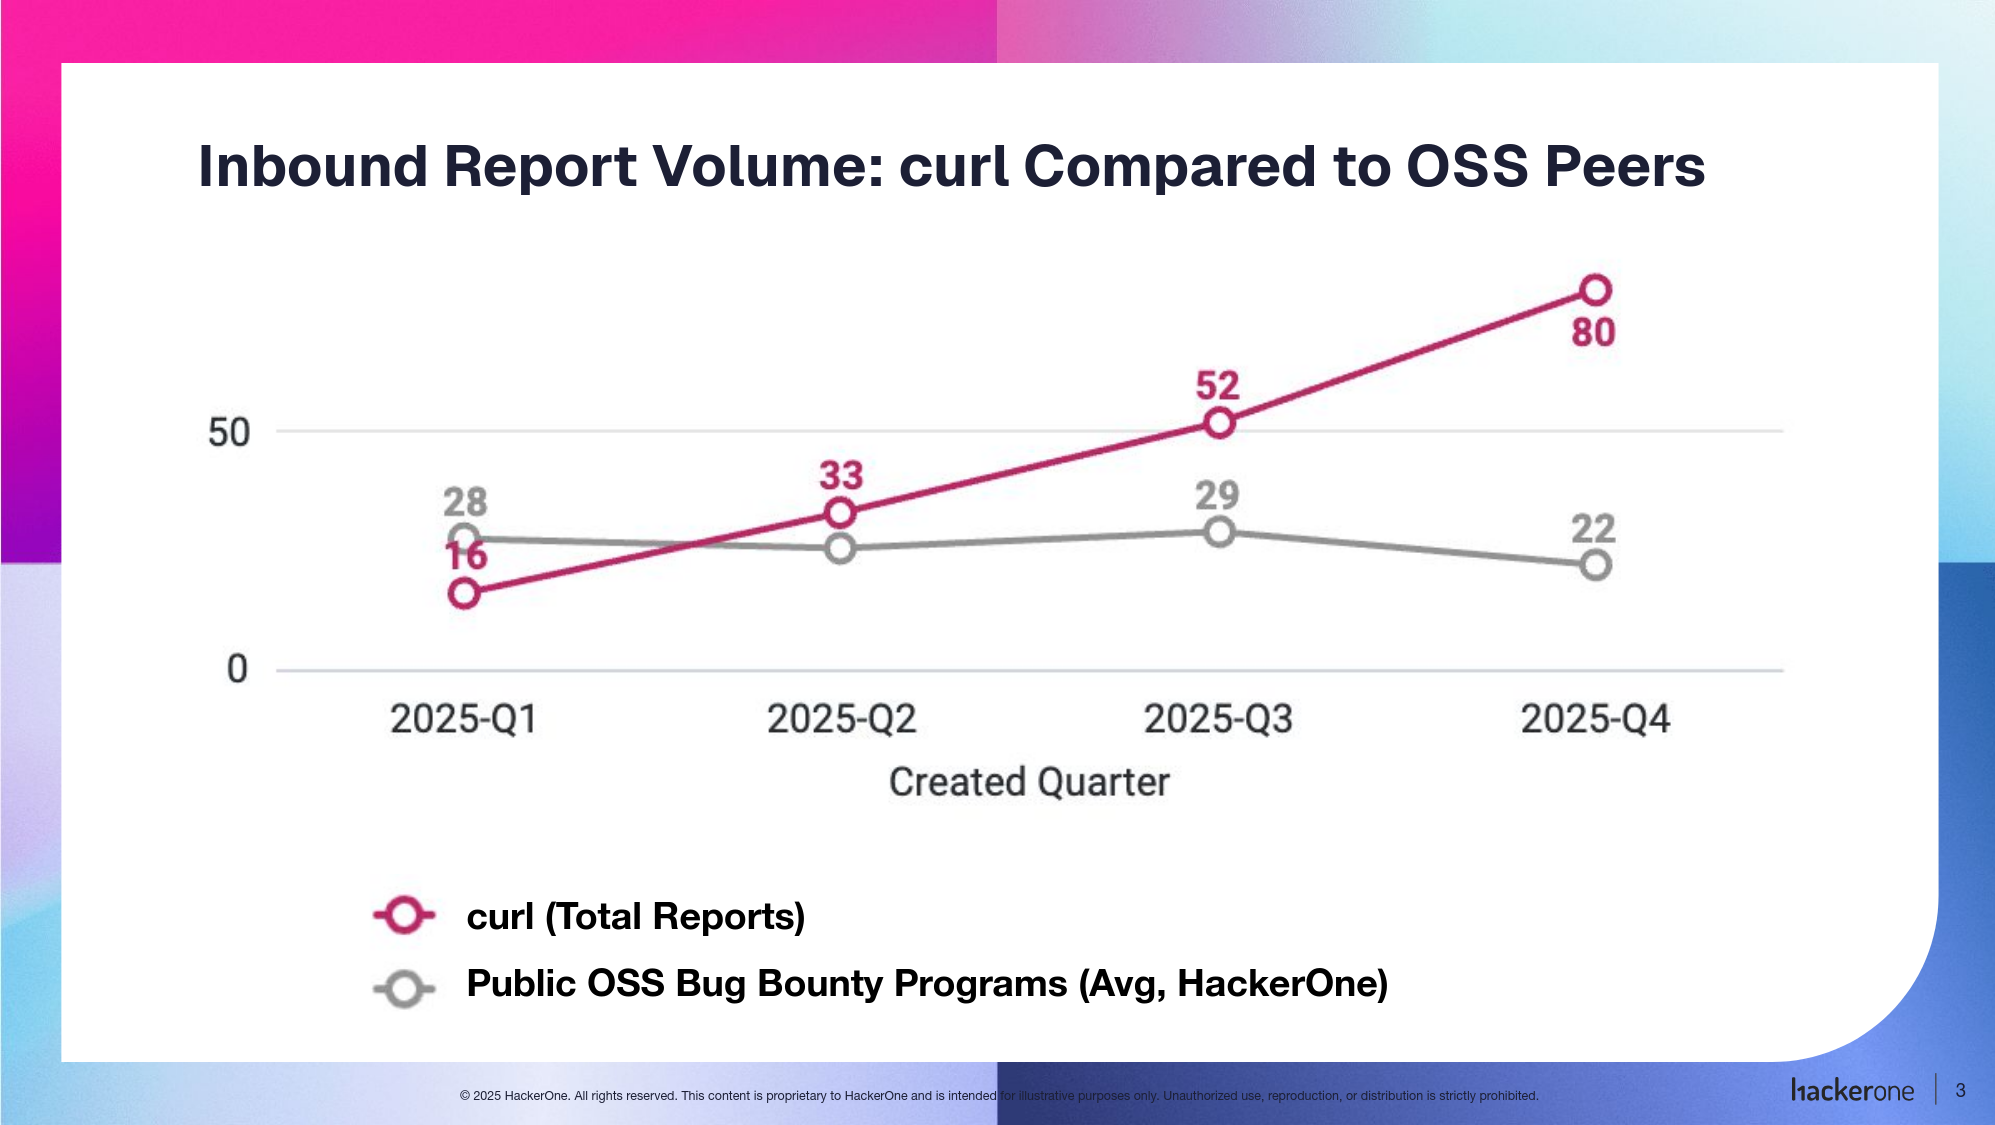
The end of the curl bug-bounty
tldr: an attempt to reduce the terror reporting. There is no longer a curl bug-bounty program. It officially stops on January 31, 2026. After having had a few half-baked previous takes, in April 2019 we kicked off the first real curl bug-bounty with the help of Hackerone, and while it stumbled a bit at first … Continue reading The end of the curl bug-bounty →
OpenAI Developers on Twitter / X
We’re releasing new Codex features to make it a more effective coding collaborator:- A new IDE extension- Easily move tasks between the cloud and your local environment- Code reviews in GitHub- Revamped Codex CLIPowered by GPT-5 and available through your ChatGPT plan.— OpenAI Developers (@OpenAIDevs) August 27, 2025
GPT-6 Astra System Card - OpenAI Deployment Safety Hub
Today, we are releasing GPT-6 Astra, the most capable model we have ever broadly deployed. Astra is our first model to reach the Critical level of cybersecurity capability under our Preparedness Framework.
Report on Burnout in Open Source Software
I am currently working on a report on the causes of burnout in open source software, and am inviting the OSS community to share their thoughts!
Astra 6.1 Pulled As Insufficiently Aligned
We once again got a new set of warnings yesterday, and new movement towards living in a sane world.
Microsoft Struggling With Hundreds of AI-Discovered Security Bugs — ProPublica
Anthropic’s Mythos has flagged bugs faster than Microsoft can fix them. Documents reviewed by ProPublica reveal the tech giant's “mad dash” behind the scenes to patch holes before hackers can find and exploit them.

GPT-6 Astra System Card - OpenAI Deployment Safety Hub
Public, mostly-static site to explore OpenAI safety evaluations, system cards, and posts.

