

A simple idea that turned out to be very useful.
VerifiedIDA | Making LLM-Driven Reverse Engineering Inspectable, Continuable and Reusable
LLM reverse engineering scales only if analysis stays inspectable. A new standard and its open-source IDA Pro implementation tie annotations to evidence.
Building Software for a Zero Trust World
How we are helping to build Zero Trust architectures that safeguard the most protected data in the world
Tock OS A Rust Based Open Platform for Transparent and Secure Root of Trust Devices
Claude reverse engineered my 32-year-old Jeep. Then it started controlling it.
Ante: A New Way to Blend Borrow Checking and Reference Counting
Ante has taken the first step towards something we all thought was impossible: blending reference counting and borrow checking without run-time crashes. 0
Enabling the next iteration of the borrow checker on nightly | Rust Blog
Empowering everyone to build reliable and efficient software.
Self-reinforcing quality / adopting verification pattern
After implementing the small-change pattern, Imprint Engineering’s next focus in improving our development loop has been implementing a verification loop for our software development. This is an increasingly common pattern, particularly popularized by poteto’s pstack, but you’ll find similar ideas emerging in other places as well, e.g. Niko Matsakis’ post on the correctness ratchet, among others. This captures some of the confusion I’ve seen in our initial rollout, and the particulars of how we are implementing the approach.
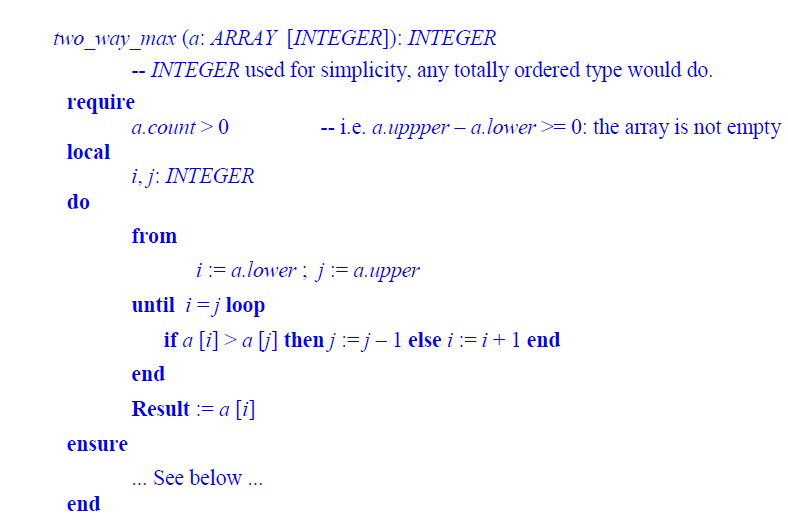
Domain Theory: the forgotten step in program verification - Bertrand Meyer's technology+ blog
Program verification is making considerable progress but is hampered by a lack of abstraction in specifications. A crucial step is, almost always, absent from the process; this omission is the principal obstacle to making verification a standard component of everyday software development. 1. Steps in software verification In the first few minutes of any ... Read more
REA — Reverse Engineer Anything
Inspect apps, binaries and runtime behavior with your coding agent or terminal. REA connects local analysis tools through CLI and MCP.
FR#150 – On ICE, Verification, and Presence As Harm
Bluesky built a verification system designed to distribute trust, and then didn't use it when it mattered.
An Update on OpenTitan
GitHub - msanft/CVE-2025-55182: Explanation and full RCE PoC for CVE-2025-55182
Explanation and full RCE PoC for CVE-2025-55182. Contribute to msanft/CVE-2025-55182 development by creating an account on GitHub.
I agentically developed a Ghost-to- @offprint.app importer script and fell down the rabbit hole that is the future of networked code sharing @v-it.org

Building GhostOff and our networked, personalized software futures
blog.bmannconsulting.com