

How co/core's two orthogonal provider guarantees work: Secure Mode (hardware attestation) and the Confidential tier (operator-blind inference).
Enhanced Security Mode | Microsoft Edge
Browse with confidence using Microsoft Edge’s Enhanced Security Mode. Learn how extra protection helps reduce risks from untrusted sites and keeps your browsing experience safer—without slowing you down.
The Secure Enclave
Secure Enclave is a dedicated secure subsystem in the latest versions of iPad, iPhone, Mac, Apple TV, Apple Vision Pro, Apple Watch, and HomePod.
Spectrum, a step towards usable secure computing
Spectrum is a project to create a computer operating system, based on the principle of security by compartmentalization. It aims to have a lower barrier to entry and to be easier to use and maintain than other such systems.

Improve device security with Advanced Protection for Android - Android Help
When you turn on Advanced Protection, you get the strongest security and privacy features to protect you and your device against online attacks, harmful apps, and data risks. This feature offers seve
Titan in depth: Security in plaintext | Google Cloud Blog
While there are no absolutes in computer security, we design, build and operate Google Cloud Platform (GCP) with the goal to protect customers' code and data. We harden our architecture at multiple layers, with components that include Google-designed hardware, a Google-controlled firmware stack, Google-curated OS images, a Google-hardened hypervisor, as well as data center physical security and services.
The seL4 Microkernel | seL4
seL4 is both the world's most highly assured and the world's fastest operating system kernel. Its uniqueness lies in the formal mathematical proof that it behaves exactly as specified, enforcing strong security boundaries for applications running on top of it while maintaining the high performance that deployed systems need.
Sharing a safety tool: announcing policyserv
Matrix, the open protocol for secure decentralised communications
Platform
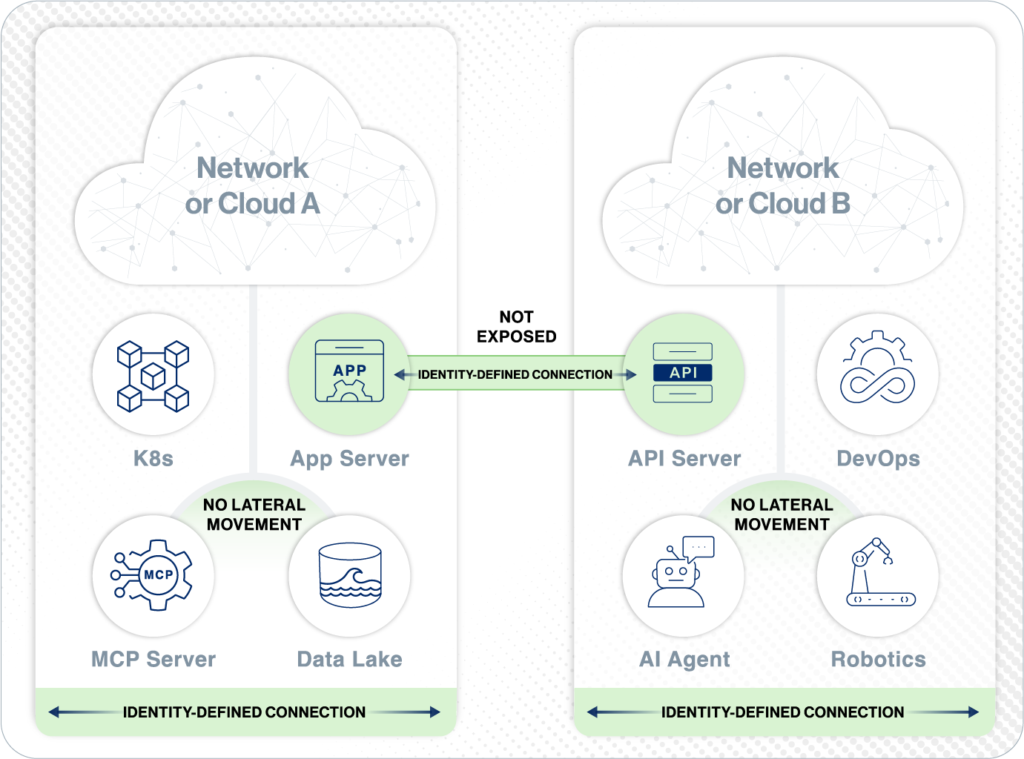
Secure workloads with Identity-First Reachability. NetFoundry closes inbound ports and replaces VPNs for simpler, zero-trust networking.
Confidential Inference via Trusted Virtual Machines
Announcing a new collaborative research paper on Confidential Inference, a set of tools to improve the security of our model weights and of our users' data
the net routes around damage. so do we.
Tieroute: an open, federated, end-to-end encrypted chat protocol. No phone number, no email, no platform in the middle.
netbirdio/netbird
Connect your devices into a secure WireGuard®-based overlay network with SSO, MFA and granular access controls.
Landlock: unprivileged access control — The Linux Kernel documentation
The goal of Landlock is to enable restriction of ambient rights (e.g. global filesystem or network access) for a set of processes. Because Landlock is a stackable LSM, it makes it possible to create safe security sandboxes as new security layers in addition to the existing system-wide access-controls. This kind of sandbox is expected to help mitigate the security impact of bugs or unexpected/malicious behaviors in user space applications. Landlock empowers any process, including unprivileged ones, to securely restrict themselves.
Confidential AI Cloud · Private Inference on GPU TEE | Phala
Phala Cloud delivers confidential AI on TEE-protected GPUs — private LLM inference, sealed agents, and verifiable compute on Intel TDX + NVIDIA H100/H200.
