Anthropic got compromised. Their Claude Code extension on Visual Studio Code and Cursor has malware in it, which creates a remote access Trojan to desktops. https://phorion.io/blog/offical-claude-code-vsx-compromise/
Security notice — malicious version of Anthropic.claude-code (2.1.313) identified in the Cursor Extension Marketplace · Cursor
Today we identified a security incident involving a specific extension package in the Cursor VS Code extension Marketplace: Anthropic.claude-code version 2.1.313.
Official Claude Code Extension Compromise: Security Advisory | Phorion
Phorion has detected a backdoor in the official Claude Code for VS Code extension bundle on the Cursor Marketplace that drops a persistent SSH backdoor across macOS, Linux, and Windows. This write-up …

Bastian Greshake Tzovaras (@gedankenstuecke@scholar.social)
It's great that a class of tool that by its very design is an unfixable security issue is forced into everything: «This works often enough that Måløy reported this to Microsoft as a security hole in March. He gave them a 90-day reporting window, Microsoft extended that twice to a total of 144 days, and they still didn’t have a solid fix. So Måløy posted about the hole on July 28th.» Copilot prompt injection goes viral in your documents https://pivot-to-ai.com/2026/08/03/copilot-prompt-injection-goes-viral-in-your-documents/
Anthropic hacked to deliver remote access trojan to Claude developer laptops worldwide
Yesterday, Anthropic were compromised and used to stage a global supply chain attack.

Malicious VS Code AI Extensions with 1.5 Million Installs Steal Developer Source Code
Security researchers found two AI-branded VS Code extensions with 1.5M installs that covertly send source code and files to China-based servers.

Everything Is Broken
Once upon a time, a friend of mine accidentally took over thousands of computers. He had found a vulnerability in a piece of software and…

When Cursor Wiped a User's PC: A Cautionary Tale of AI Overreach
We recently received a sobering story from a subscriber, a stark reminder of the potential pitfalls when granting AI agents unfettered access to your system.

Microsoft's open source tools were hacked to steal passwords of AI developers | TechCrunch
Microsoft shut down dozens of GitHub code repositories for Azure and AI coding tools after a reported hack.

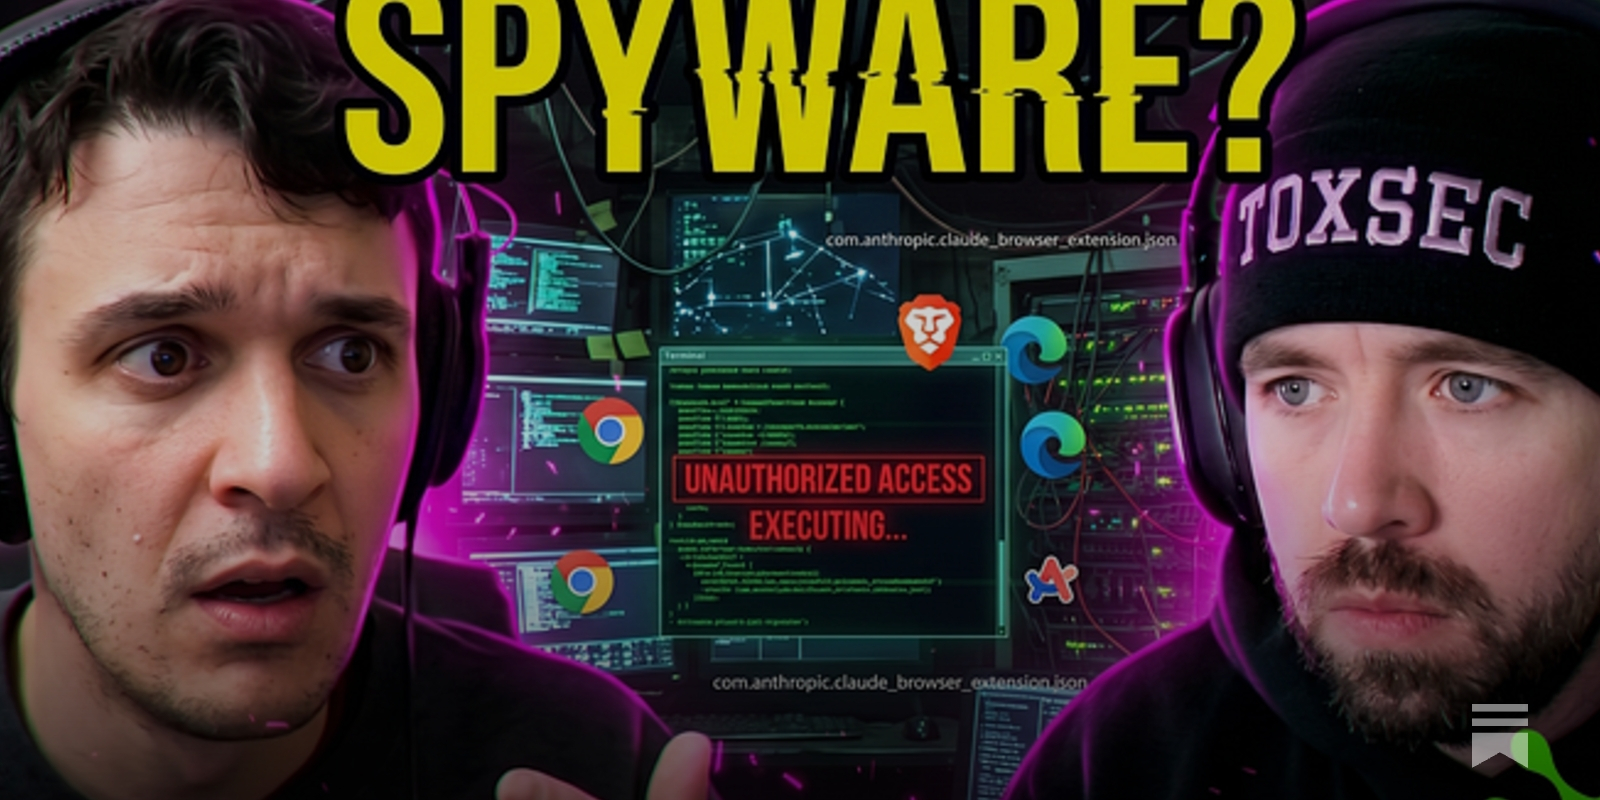
Comment and Control: Prompt Injection to Credential Theft in Claude Code, Gemini CLI, and GitHub Copilot Agent
Anthropic Claude Code Security Review, Google Gemini CLI Action, and GitHub Copilot Agent are vulnerable to prompt injection via GitHub comments — turning PR titles, issue bodies, and issue comments into attack vectors for API key and token theft.
Is Claude Code Secretly Installing Spyware?
A researcher caught Claude Desktop installing browser bridges silently. Plus the MCP RCE Anthropic won’t patch.
Charly Wargnier on Twitter / X
an AI agent literally destroyed all of this guy's production data 🤯Total AI disaster, yet totally predictable.here's the story:> Cursor agent (Opus 4.6) tries to fix a staging bug> Finds an unscoped Railway CLI token> Guesses an API call> Wipes Prod DB & 3 mos of backups… https://t.co/24KfDhMtVz— Charly Wargnier (@DataChaz) April 27, 2026
zak.eth on Twitter / X
🚨 UPDATE: Full Post-Mortem On Cursor Security IncidentIn yesterday’s thread I explained how I got drained after installing a malicious extension in @cursor_ai.This is the deeper dive into what I found, what I did, and how you can avoid it.🧵 👇— zak.eth (@0xzak) August 13, 2025
A GitHub Issue Title Compromised 4,000 Developer Machines
A prompt injection in a GitHub issue triggered a chain reaction that ended with 4,000 developers getting OpenClaw installed without consent. The attack composes well-understood vulnerabilities into something new: one AI tool bootstrapping another.
Using Claude to reduce the attack surface of code
Automated attack surface analysis and reduction can meaningfully improve the security of deployed software in the near term. In this post, we preview data we’ve collected from applying attack surface reduction techniques to large open-source codebases using Claude.

Securing CI/CD in an agentic world: Claude Code Github action case | Microsoft Security Blog
Microsoft Threat Intelligence identified a prompt injection pathway in Claude Code GitHub Action that allowed access to workflow secrets under specific conditions. This research examines the attack chain, responsible disclosure process, Anthropic's mitigation, and guidance for securing AI-powered CI/CD workflows.