

Learn more about Security incident detection in the GitLab documentation.
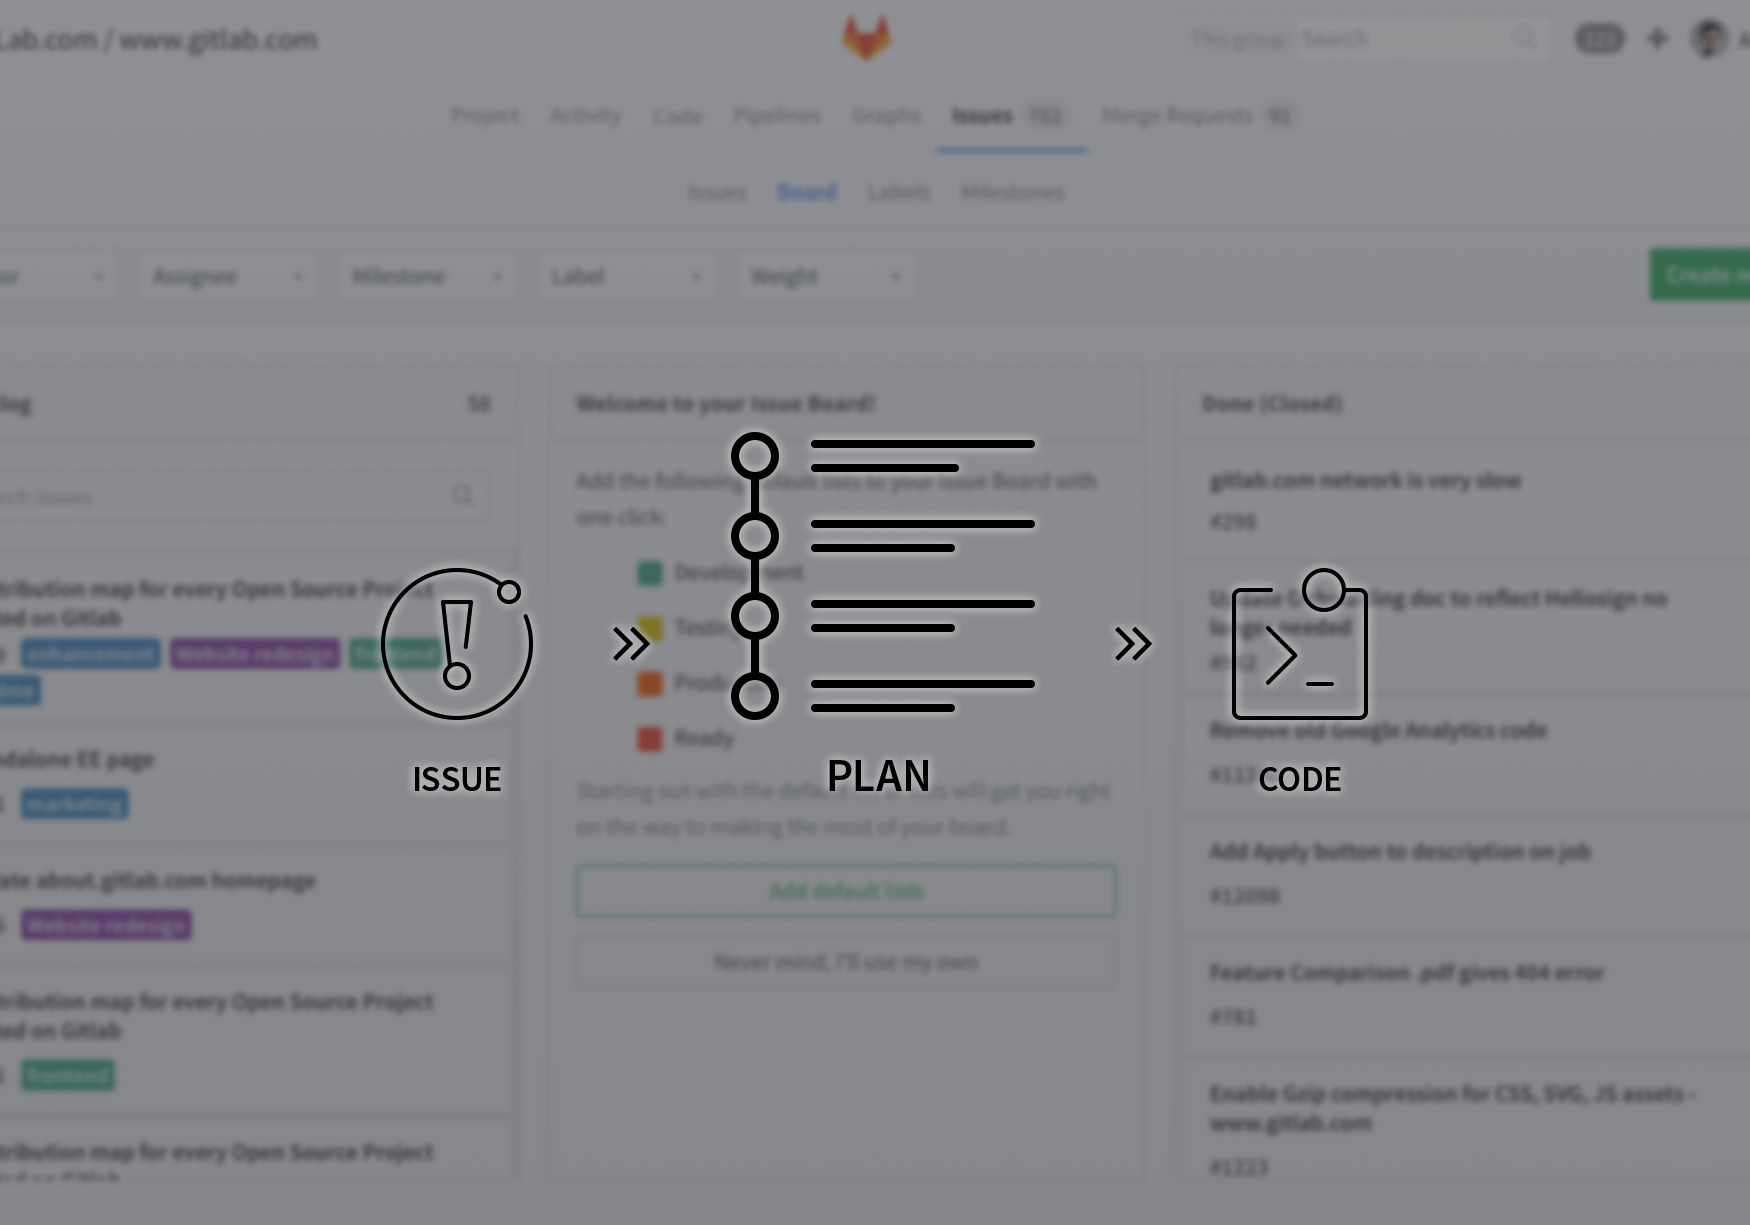
Announcing The GitLab Issue Board
Strengthen your Release Management Process: announcing the GitLab Issue Board!
GitLab Critical Patch Release: 19.5.1, 19.4.3, 19.3.6, 19.2.9, 19.1.9, 19.0.10, 18.11.13 | GitLab Docs
Learn more about GitLab Critical Patch Release: 19.5.1, 19.4.3, 19.3.6, 19.2.9, 19.1.9, 19.0.10, 18.11.13 for GitLab Community Edition (CE) and Enterprise Edition (EE).
GitLab Critical Patch Release: 19.4.1, 19.3.3, 19.2.7 | GitLab Docs
Learn more about GitLab Critical Patch Release: 19.4.1, 19.3.3, 19.2.7 for GitLab Community Edition (CE) and Enterprise Edition (EE).
GitLab Patches CVSS 10.0 Flaw That Could Let Unauthenticated Users Run Server Code
GitLab fixed CVE-2026-97229 (CVSS 10.0), a CI/CD flaw that could allow unauthenticated code execution under certain conditions.

Open Source is a privilege. Not a right. | devroom.io
Edit: this is not a Gitlab specific issue. I’ve seen it before and I’m seeing it again at the Gitlab project. The past few months I’ve been contributing to the Gitlab project. This has been a great experience, mostly because Gitlab has become a very popular project with over 2.3k watchers right now.
jdalrymple/gitbeaker
🦊🧪 A comprehensive and typed Gitlab SDK for Node.js, Browsers, Deno and CLI
Investigating unauthorized access to GitHub-owned repositories
If any impact is discovered, customers will be notified via established incident response and notification channels.
Support ActivityPub for GitLab (#11247) · Epics · GitLab.org · GitLab
Gitlab/ActivityPub Design Documents by @oelmekki
Critical GitLab Flaw (CVSS 10.0) Could Allow Unauthenticated RCE Across 12 Years of Releases
GitLab fixes CVE-2026-110264, a critical flaw that could allow unauthenticated code execution on self-managed versions dating back to 7.0.

atforge
atforge is GitLab with the AT Protocol built in: a bundled Personal Data Server, sign-in with a handle or a DID, and a did:web identity for the instance.

Is GitHub Cooked?
Track GitHub service incidents and outages. Real-time stats, incident history, and downtime analytics.
GitHub MCP Exploited: Accessing private repositories via MCP
We showcase a critical vulnerability with the official GitHub MCP server, allowing attackers to access private repository data. The vulnerability is among the first discovered by Invariant's security analyzer for detecting toxic agent flows.
Wijiti / blackhole / messenger · GitLab
A peer-to-peer, decentralized, general-purpose messaging application. Runs in the web browser. All messages are encrypted on the peer and the application can be run entirely client-side.

Our big Frontend plan revealed
Our long term plan to make GitLab as fast and performant as possible with Vue and webpack.
software-metadata-tool-pipeline / software-metadata-sync-tool · GitLab
Helmholtz Codebase - GitLab
