

The goal of Landlock is to enable restriction of ambient rights (e.g. global filesystem or network access) for a set of processes. Because Landlock is a stackable LSM, it makes it possible to create safe security sandboxes as new security layers in addition to the existing system-wide access-controls. This kind of sandbox is expected to help mitigate the security impact of bugs or unexpected/malicious behaviors in user space applications. Landlock empowers any process, including unprivileged ones, to securely restrict themselves.
anthropic-experimental/sandbox-runtime
A lightweight sandboxing tool for enforcing filesystem and network restrictions on arbitrary processes at the OS level, without requiring a container.
fencesandbox/fence
Lightweight, container-free sandbox for running commands with network and filesystem restrictions
Tock OS A Rust Based Open Platform for Transparent and Secure Root of Trust Devices
Sooraj on Twitter / X
IronClaw (@near_ai, Rust) is the most architecturally serious alternative. Built by @ilblackdragon as a direct response to OpenClaw's security failures. Tools and channels run in isolated WASM containers with capability-based permissions. Credentials live in an encrypted vault… https://t.co/3VkLn4f0Ai— Sooraj (@iAnonymous3000) February 16, 2026
linuxkit/linuxkit
A toolkit for building secure, portable and lean operating systems for containers
DropLock
The link below is like an open lock box that belongs to you. Anyone you share it with can put a secret inside and create a locked link that only you can open.
Genode - Genode Operating System Framework
We understand the complexity of code and policy as the most fundamental security problem shared by modern general-purpose operating systems. Because of high functional demands and dynamic workloads, however, this complexity cannot be avoided. But it can be organized. Genode is a novel OS architecture that is able to master complexity by applying a strict organizational structure to all software components including device drivers, system services, and applications. The Genode OS framework is an open-source tool kit for building highly secure component-based operating systems. It scales from embedded devices to dynamic general-purpose computing.
Sprites - Stateful sandboxes
Persistent, hardware-isolated execution environments for arbitrary code. Run AI agents, untrusted code, and more in secure sandbox environments with checkpoint & restore.
libkrun/libkrun
A dynamic library providing Virtualization-based process isolation capabilities
oss-security - Dirty Frag: Universal Linux LPE
Please check out the Open Source Software Security Wiki, which is counterpart to this mailing list.
Introducing Deno Sandbox | Deno
Instant Linux microVMs with defense-in-depth security for running untrusted code.
Lockdown Systems
A worker-owned collective building freedom and privacy tech, empowering people to take control of their own data and protect themselves from unwanted surveillance
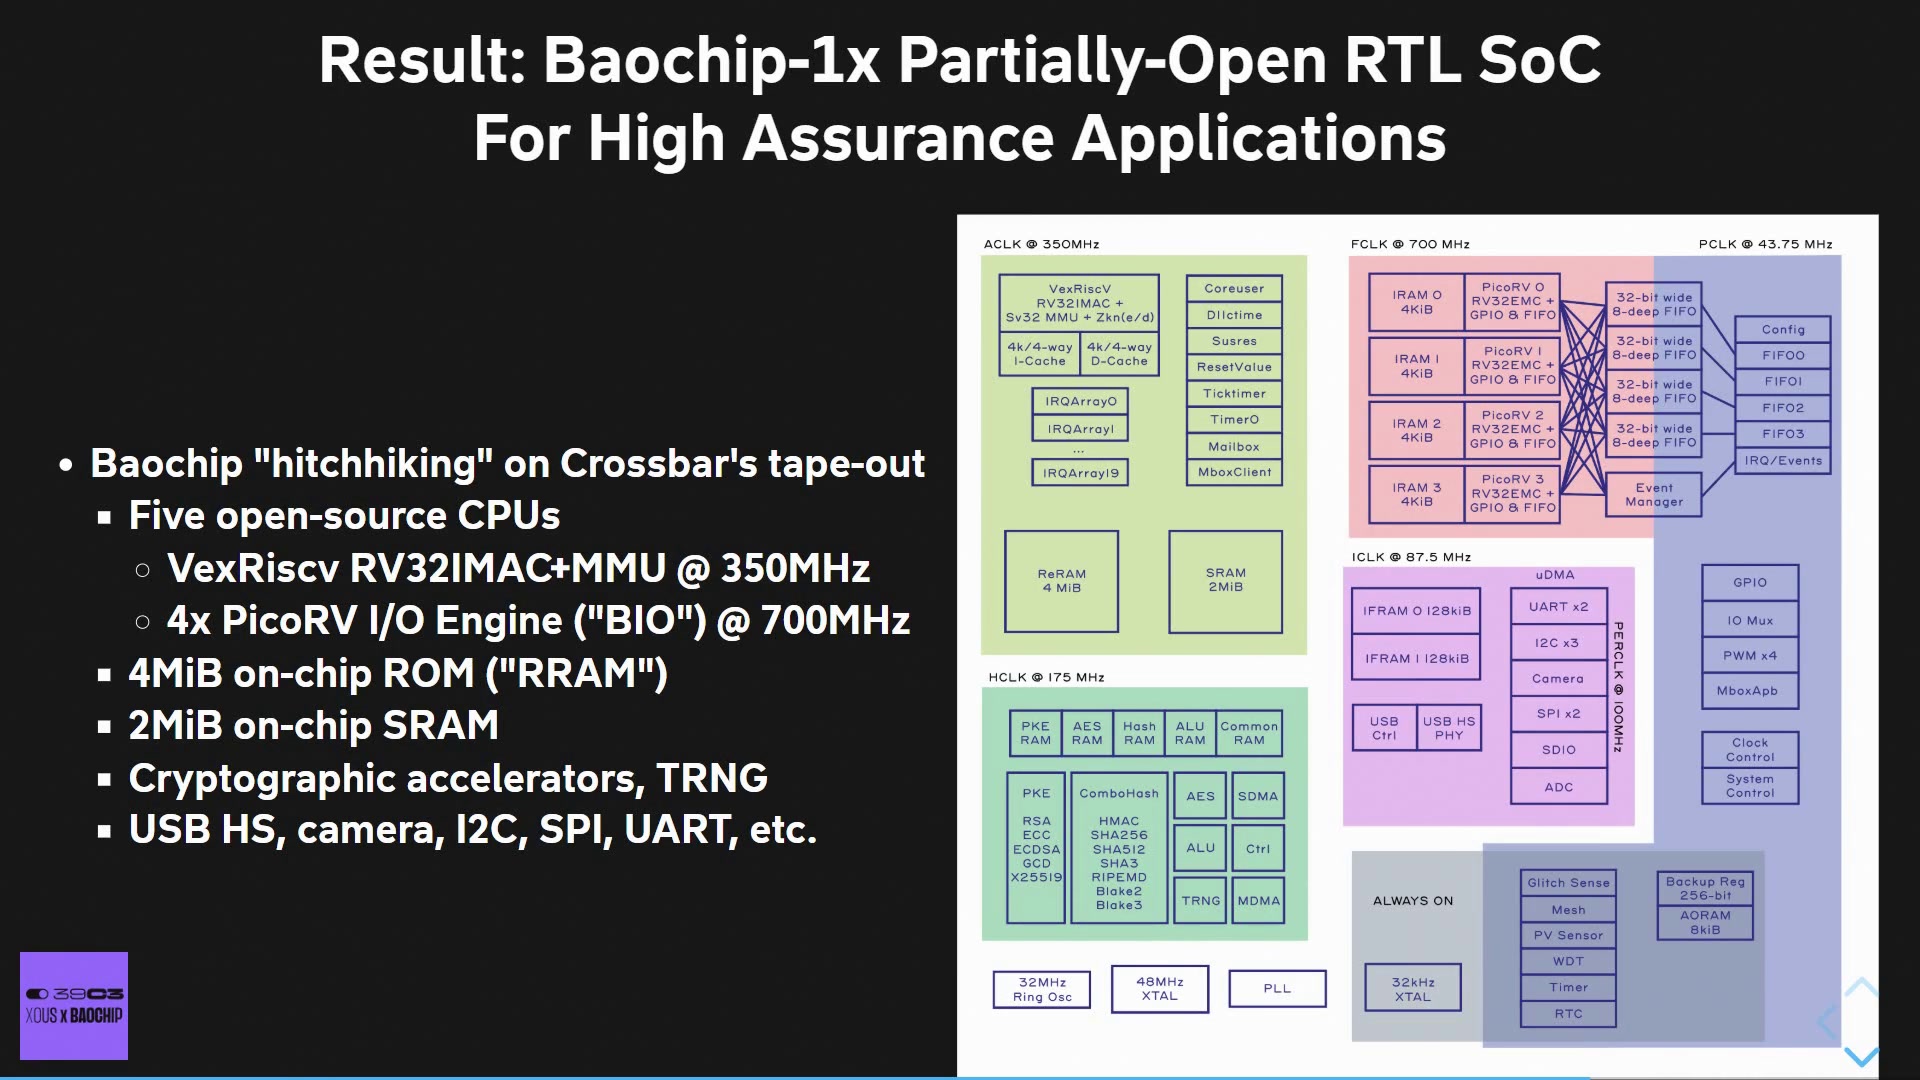
Xous: A Pure-Rust Rethink of the Embedded Operating System
Xous is a message-passing microkernel implemented in pure Rust, targeting secure embedded applications. This talk covers three novel aspe...
Secure Mode: Deno & Node.js compatible permissions for Bun, but better by kynnyhsap · Pull Request #25911 · oven-sh/bun
Summary Implements a Deno-compatible permissions model for Bun, providing granular control over system resource access. This PR introduces a security sandbox that can restrict file system, network,...
Linux Firewalls: How to Actually Secure a Cloud Server (iptables, nftables, firewalld, ufw)
A practical guide to the four major Linux firewall technologies - iptables, nftables, firewalld, and ufw. Covers real-world cloud server hardening with concrete examples, from locking down SSH to b...
A deep dive on permissioned-data space access. The dials, policies, and the difference between handing out keys and revoking them.

Permissioned Data: Space Access
ngerakines.leaflet.pub