

Our helper dll for the installer was erroneously flagged by several antivirus programs, so we re-released the Windows version as 1.12.1-1 to address this issue. No need to worry, these were false positives that for some reason didn't like the version of gcc used to compile the helper dll. To prevent this happening again, we have now used MSVC to compile the helper dll.
“As a Windows user, it’s a very surreal way to install a program.” – Unsung
A blog about software craft and quality
Bastian Greshake Tzovaras (@gedankenstuecke@scholar.social)
It's great that a class of tool that by its very design is an unfixable security issue is forced into everything: «This works often enough that Måløy reported this to Microsoft as a security hole in March. He gave them a 90-day reporting window, Microsoft extended that twice to a total of 144 days, and they still didn’t have a solid fix. So Måløy posted about the hole on July 28th.» Copilot prompt injection goes viral in your documents https://pivot-to-ai.com/2026/08/03/copilot-prompt-injection-goes-viral-in-your-documents/
EricLBuehler/safetensors_explorer
CLI utility to inspect and explore .safetensors and .gguf files
Fix your tools
Last week I had to diagnose a bug in an open source library I maintain. The issue was gnarly enough that I couldn’t find it right away, but then I thought: if I set a breakpoint here and fire up the debugger, I will likely find the root cause very soon… and then proceed to mercilessly destroy it! So I rolled up my sleeves, set the breakpoint, fired up the debugger, and… saw the program run to completion without interruptions whatsoever.
Microsoft joins group working to ‘cure’ open-source licensing issues
Microsoft is one of 10 companies now committed to work through open-source software licensing problems involving the GPL with customers before resorting to legal action.
Scan always fails at seal step: `scan-manifest.json: expected a regular file inside the scan directory` — reproducible on Windows AND Linux · Issue #73 · openai/codex-security
Summary codex-security scan fails deterministically at the seal step. The scan runs to completion (models are invoked, tokens billed), preflight reports zero issues, then the tool errors trying to ...
[bug] tauri build errors out at bundling step · Issue #5175 · tauri-apps/tauri
Describe the bug When running tauri build the binary builds fine but then immediately errors out with thread '<unnamed>' panicked at 'Can't detect any appindicator library'...
StartAllBack to fix all Windows 11 deal-breaking UI issues
StartAllBack restores taskbar, start menu, context menus, explorer, sanity, style and order!
Microsoft Struggling With Hundreds of AI-Discovered Security Bugs — ProPublica
Anthropic’s Mythos has flagged bugs faster than Microsoft can fix them. Documents reviewed by ProPublica reveal the tech giant's “mad dash” behind the scenes to patch holes before hackers can find and exploit them.

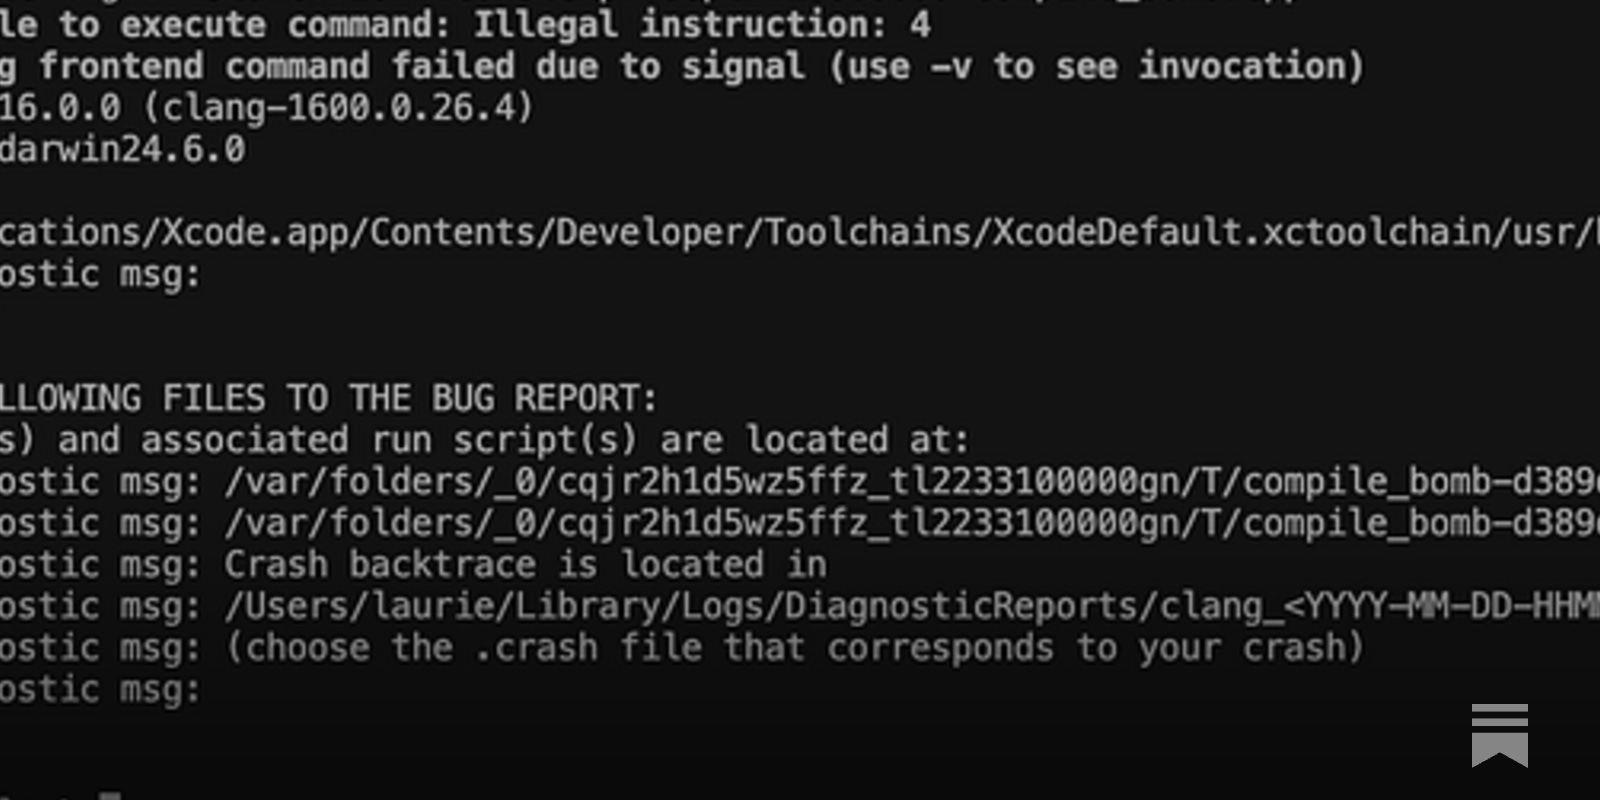
using C++ to exploit the C++ that is building the C++
today you’re going to segfault your compiler.
SHARP APL Source Code
SHARP APL source code (circa 1989). This is posted for educational and historical purposes and may not represent a fully working system. Tools associated with a full system (e.g., assembler, link-editor, IBM 370-code simulator, graphics driver, workspaces) may also not be included. Likely this was a version used to generate the PC version of SHARP APL. NOTE: The original files are ANSI encoded but look to have originally contained APL characters (which are no longer displayed as such). As a result, the comments and some other lines are sometimes hard to read. A secondary zip file has been added which attempts to convert the files to UTF8 and to change some characters back to APL. A zip file of SHARP APL/PC workspace listings has been added for example code. A version of SHARP APL/PC has been added which also has additional implementation code examples (requires a DOS emulator in order to run).

Beginner's Guide to Linkers
A typical example of what triggers this explanation is when I help someone who has a link error like:
Killed by Microsoft
Killed by Microsoft is the Microsoft Graveyard. A full list of dead products killed by Microsoft in the Microsoft Cemetery.
C ABI Changes for `wasm32-unknown-unknown` | Rust Blog
Empowering everyone to build reliable and efficient software.
WinFS, Integrated/Unified Storage, and Microsoft – Part 1
People have been bugging me to write about Integrated Storage for some time, and with Bill Gates having just disclosed that failure to ship WinFS was his biggest product regret now seemed like a g…
