


Capability based security and more
Authorization Series — Pt 1: What is Authorization?
Editor’s Note: This is the first, introductory post in a 3-part series on focusing on Authorization. Stay tuned for future parts in this…

WAVE: A Decentralized Authorization Framework with Transitive Delegation | USENIX
Michael P Andersen, Sam Kumar, Moustafa AbdelBaky, Gabe Fierro, John Kolb, Hyung-Sin Kim, David E. Culler, and Raluca Ada Popa, University of California, Berkeley
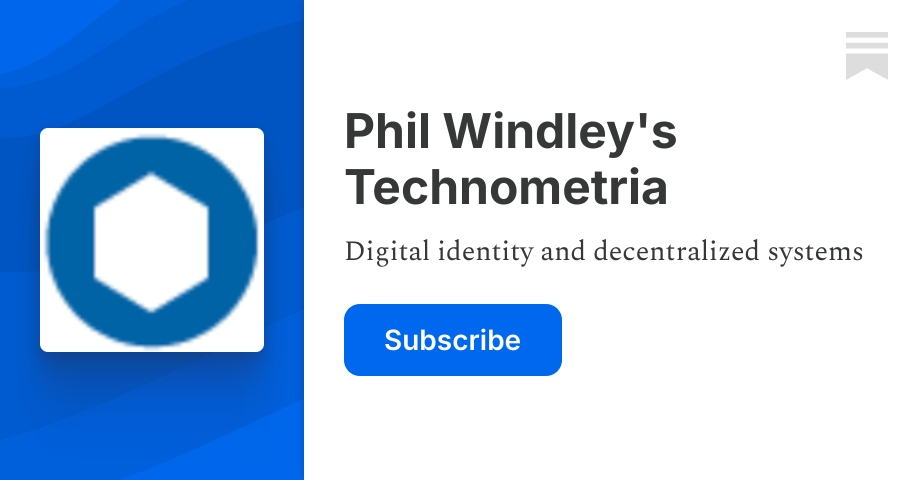
UCAN - User Controlled Authorization Network
A trustless, secure, local-first, user-originated, distributed authorization scheme.
How to handle granular permissions | Authorization Resources | Google for Developers
Granular permissions give users more control over the specific data they share with apps, improving transparency, security, and trust.
Musings of a Trust Architect: Least & Necessary Design Patterns
ABSTRACT: The principles of least privilege and least authority are core computer security principles that can minimize attacks. Not only can they be ex...
Authorization Series — Pt 3: Dynamic Authorization with GraphQL and Rules
Editor’s Note: This is the third and final technical post in a 3-part series on focusing on Authorization. If you’d like to read the…
Object-capability model
The object-capability model is a computer security model. A capability describes a transferable right to perform one (or more) operations on a given object. It can be obtained by the following combination:
AIP: Agent Identity Protocol for Verifiable Delegation Across MCP and A2A
AI agents increasingly call tools via the Model Context Protocol (MCP) and delegate to other agents via Agent-to-Agent (A2A), yet neither protocol verifies agent identity. A scan of approximately 2,000 MCP servers found all lacked authentication. In our survey, we did not identify a prior implemented protocol that jointly combines public-key verifiable delegation, holder-side attenuation, expressive chained policy, transport bindings across MCP/A2A/HTTP, and provenance-oriented completion records. We introduce Invocation-Bound Capability Tokens (IBCTs), a primitive that fuses identity, attenuated authorization, and provenance binding into a single append-only token chain. IBCTs operate in two wire formats: compact mode (a signed JWT for single-hop cases) and chained mode (a Biscuit token with Datalog policies for multi-hop delegation). We provide reference implementations in Python and Rust with full cross-language interoperability. Compact mode verification takes 0.049ms (Rust) and 0.189ms (Python), with 0.22ms overhead over no-auth in real MCP-over-HTTP deployment. In a real multi-agent deployment with Gemini 2.5 Flash, AIP adds 2.35ms of overhead (0.086% of total end-to-end latency). Adversarial evaluation across 600 attack attempts shows 100% rejection rate, with two attack categories (delegation depth violation and audit evasion through empty context) uniquely caught by AIP's chained delegation model that neither unsigned nor plain JWT deployments detect.

Authority as Possession: Permissioned Spaces Deserve Better Than ACLs
Why Capability Trees are the right governance primitive for permissioned spaces.
Composing capability security and conflict-free replicated data types — Spritely Institute
In August, I attended the DWeb Seminar where a small group of builders gathered to discuss the state-of-the-art and open problems in the distributed web space. Some in the group are primarily concerned with distributed data and focus on sync algorithms and local-first use cases. I am mainly concerned with distributed behavior and focus on the object capability security model. Both areas of study are steeped in their own lore and research papers, which makes it difficult for the two camps to communicate effectively with each other.
Permissioned Data Diary 6: Boring Auth - Daniel's Leaflets
In which we resist the temptation to invent a clever authorization model & pick the boring one instead.