

We understand the complexity of code and policy as the most fundamental security problem shared by modern general-purpose operating systems. Because of high functional demands and dynamic workloads, however, this complexity cannot be avoided. But it can be organized. Genode is a novel OS architecture that is able to master complexity by applying a strict organizational structure to all software components including device drivers, system services, and applications. The Genode OS framework is an open-source tool kit for building highly secure component-based operating systems. It scales from embedded devices to dynamic general-purpose computing.
An Update on OpenPRoT
Tock OS A Rust Based Open Platform for Transparent and Secure Root of Trust Devices
Xous: A Pure-Rust Rethink of the Embedded Operating System
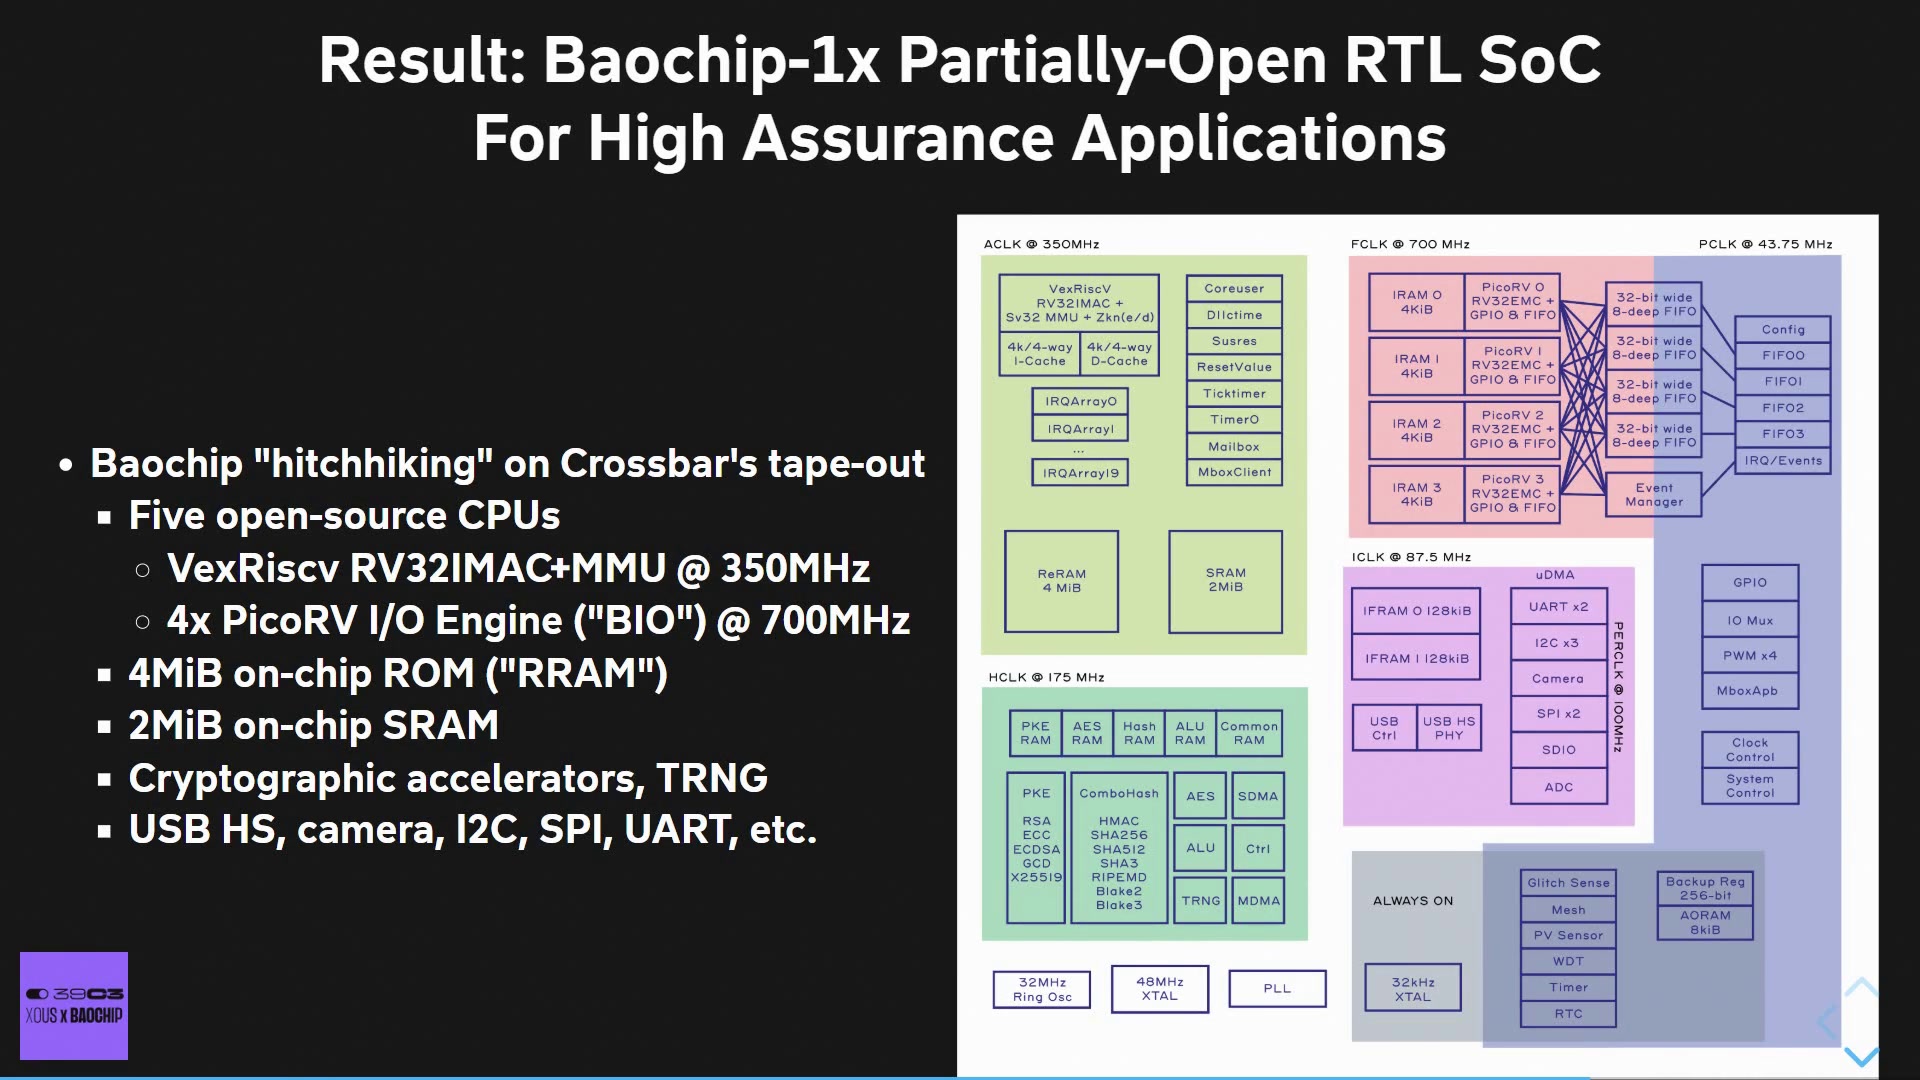
Xous is a message-passing microkernel implemented in pure Rust, targeting secure embedded applications. This talk covers three novel aspe...
The seL4 Microkernel | seL4
seL4 is both the world's most highly assured and the world's fastest operating system kernel. Its uniqueness lies in the formal mathematical proof that it behaves exactly as specified, enforcing strong security boundaries for applications running on top of it while maintaining the high performance that deployed systems need.
oss-security - Dirty Frag: Universal Linux LPE
Please check out the Open Source Software Security Wiki, which is counterpart to this mailing list.
Smarter Operating Systems Will Use Wasm - The Coming OS Revolution by Jonas Kruckenberg @ Wasm I/O
OpenFang — The Agent Operating System
Open-source Agent OS built in Rust. 7 autonomous Hands. 16 security layers. 40 channels. 27 providers. Single binary. Battle-tested.
Pop!_OS Linux Operating System | Secure, Customizable & Productive
Explore Pop!_OS, a Linux operating system built for productivity, customization, security, and software compatibility. Free to download from System76.
Finally, Our Own OS – Oh Yes!
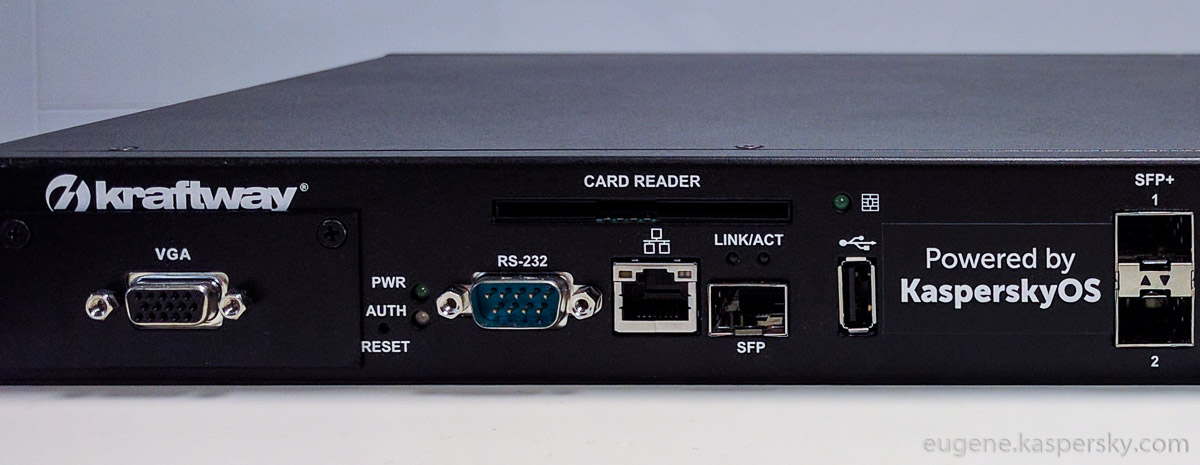
At last – we’ve done it! I’ve anticipated this day for ages – the day when the first commercially available mass market hardware device based our own secure operating system landed on my desk.
TrenchBoot Anti Evil Maid (current plan - v2) - Dasharo Universe
As Qubes OS users, promoters, and developers, we understand how essential it is to be aware of the latest developments in maintaining the security of your favorite operating system. We're excited to share our plans to integrate the TrenchBoot Project into Qubes OS's new Anti-Evil Maid (AEM) implementation. As you may know, traditional firmware security measures like UEFI Secure Boot and measured boot, even with a Static Root of Trust (SRT), may only sometimes be enough to ensure a completely secure environment for your operating system. Compromised firmware may allow for the injection of malicious software into your system, making it difficult to detect. To overcome these limitations, many silicon vendors have started implementing Dynamic Root of Trust (DRT) technologies to establish a secure environment for operating system launch and integrity measurements. We're excited to take advantage of these advancements through integration with the TrenchBoot Project.
Composio
Just-in-time tool calls, secure delegated auth, sandboxed environments, and parallel execution across 1,000+ apps.
anthropic-experimental/sandbox-runtime
A lightweight sandboxing tool for enforcing filesystem and network restrictions on arbitrary processes at the OS level, without requiring a container.
Vercel Sandbox
Vercel Sandbox allows you to run arbitrary code in isolated, ephemeral Linux VMs.
Why AVF?
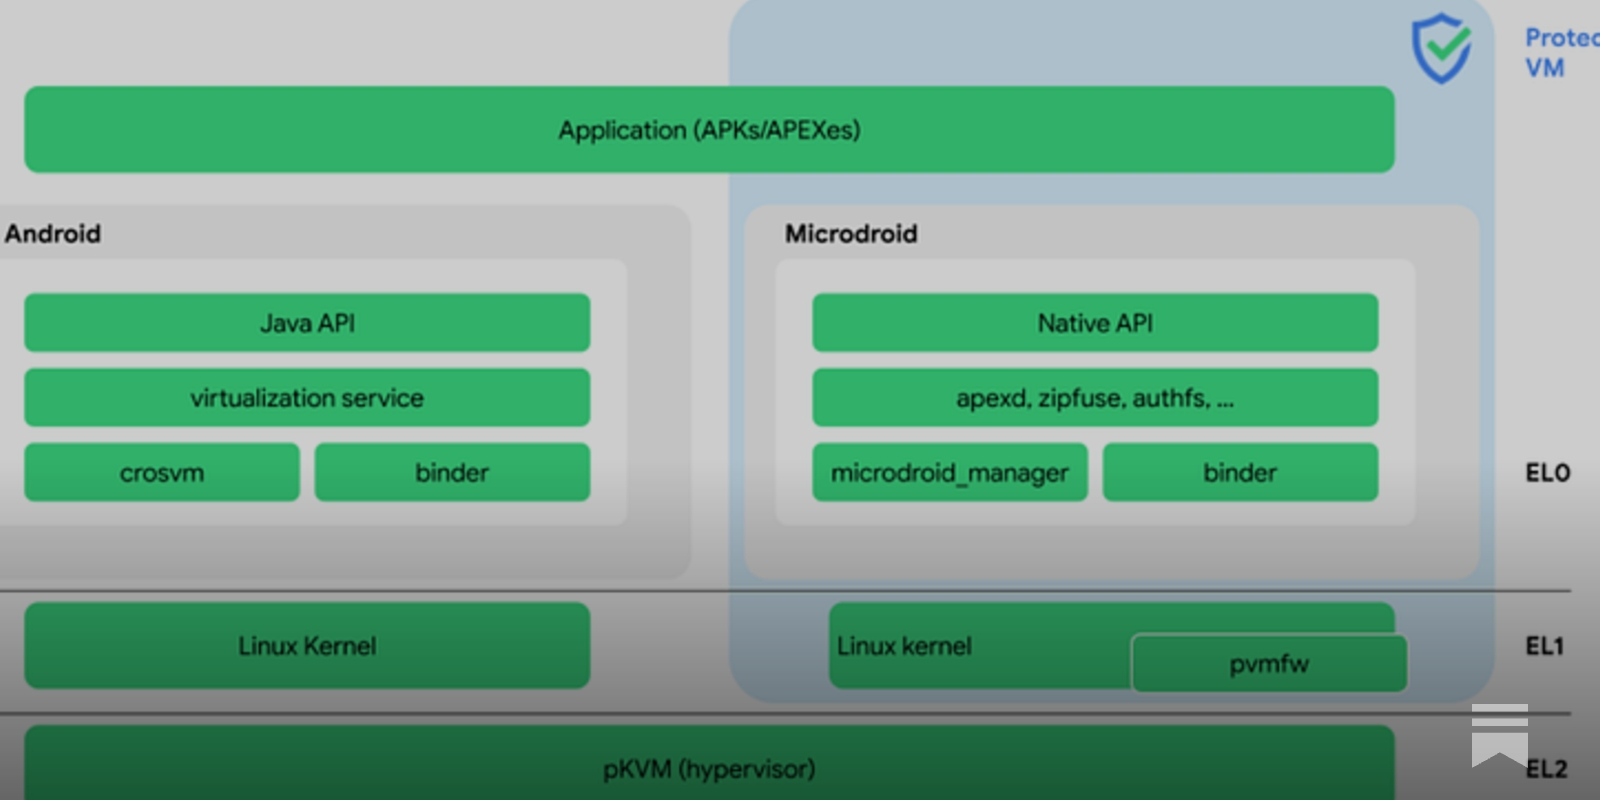
AVF and pKVM: next-generation Trustworthy Execution Environment for connected products
New OS

Building a next generation operating system Capabilities security model, RISC V, atproto service accounts (like iCloud), local first, agentic integration
unikernels were hard. key word: were.
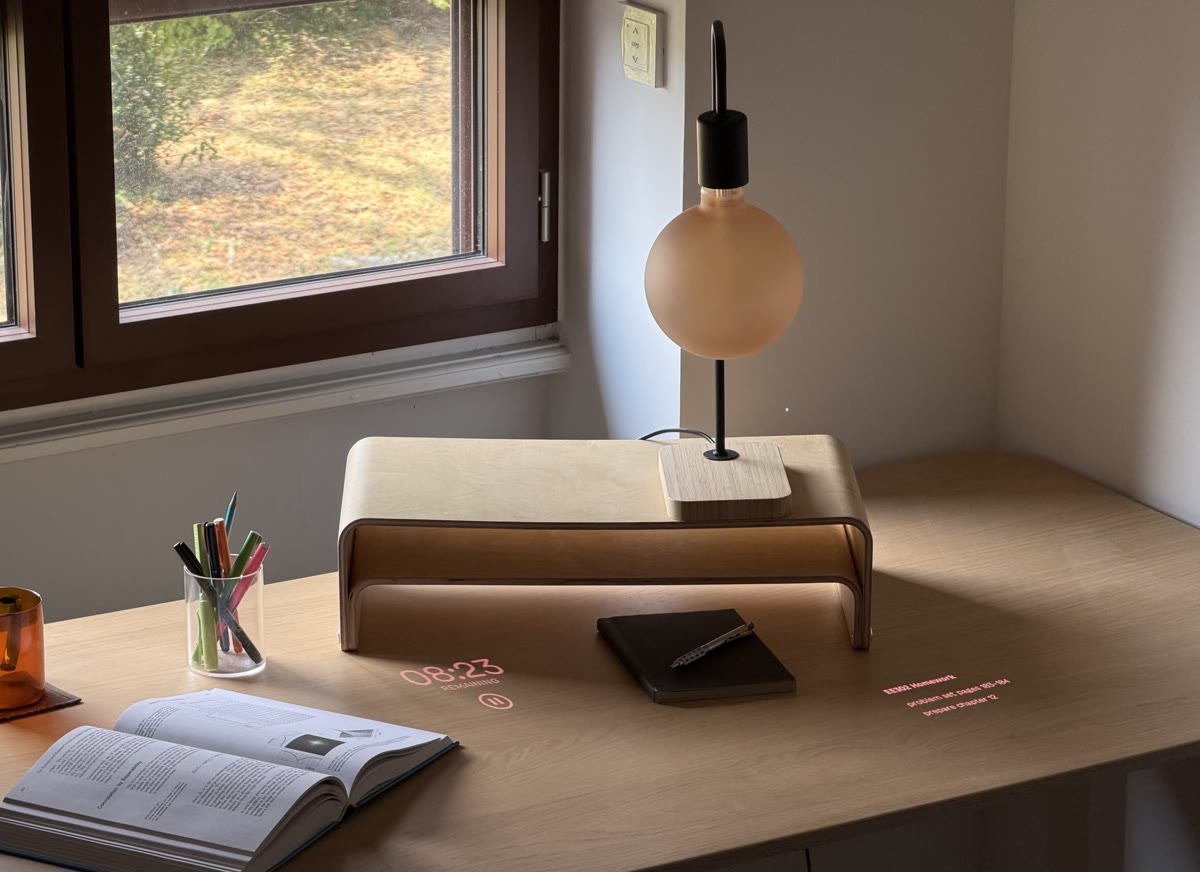
The Lightbulb Computer — Reimagining Spatial & Ambient Computing with Projectors
What Even Is An OS Now?

so that new Mac Studio and M5 Ultra have me thinking about 2030 now the wildcard on the $1200ish 2030 Mac Mini is RAM. who knows what the…
MercuryOS
inanimate-tech/resident