


Primary - the Zero Trust Control Plane, offers unparalleled security and control for web access. Protect corporate data and secure your workforce without compromising speed and usability.
Building Software for a Zero Trust World
How we are helping to build Zero Trust architectures that safeguard the most protected data in the world
Zero Trust Information
Zero Trust Networking is security with Internet assumptions; there is tremendous value if we apply the same approach to information.

NetFoundry Documentation
Cloud-managed zero-trust networking platform. Manage identities, policies, services, and routers from the console, or automate through the API.
Secure Minions: private collaboration between Ollama and frontier models· Ollama Blog
Secure Minions is a secure protocol built by Stanford's Hazy Research lab to allow encrypted local-remote communication.
ĐApps: What Web 3.0 Looks Like
As we move into the future, we find increasing need for a zero-trust interaction system. Even pre-Snowden, we had realised that entrusting our information to arbitrary entities on the internet was fraught with danger. However, post-Snowden the argument plainly falls in the hand of those who believe that large organisations and governments routinely attempt to stretch and overstep their authority. Thus we realise that entrusting our information to organisations in general is a fundamentally broken model. The chance of an organisation not meddling with our data is merely the effort required minus their expected gains. Given they tend to have an income model that requires they know as much about people as possible the realist will realise that the potential for convert misuse is difficult to overestimate.
Trust Over IP - Defining a complete architecture for Internet-scale digital trust
The Trust over IP Foundation is defining a complete architecture for Internet-scale digital trust that combines both cryptographic trust at the machine layer and human trust at the business, legal, and social layers.
Tinfoil - Private AI
AI that keeps your data private at all times. Fast, powerful, and verifiable, thanks to secure hardware enclaves.
Data Minimisation in Communication Protocols: A Formal Analysis...
With the growing amount of personal information exchanged over the Internet, privacy is becoming more and more a concern for users. One of the key principles in protecting privacy is data...

openPDS/SafeAnswers - The privacy-preserving Personal Data Store
Protecting the Privacy of Metadata through SafeAnswers
Web of trust
In cryptography, a web of trust is a concept used in PGP, GnuPG, and other OpenPGP-compatible systems to establish the authenticity of the binding between a public key and its owner. Its decentralized trust model is an alternative to the centralized trust model of a public key infrastructure (PKI), which relies exclusively on a certificate authority. As with computer networks, there are many independent webs of trust, and any user can be a part of, and a link between, multiple webs.

Exit Chat Control · Become Ungovernable
A practical field guide to escape Chat Control and reclaim your digital privacy: encrypted messaging, email, VPN, DNS, passwords, Linux, GrapheneOS, self-hosting. Free, open source, no tracking.

Keyhive: Local-first access control
Keyhive is a project exploring local-first access control. It aims to provide a firm basis for secure collaboration, similar to the guarantees of private chat but for any local-first application.
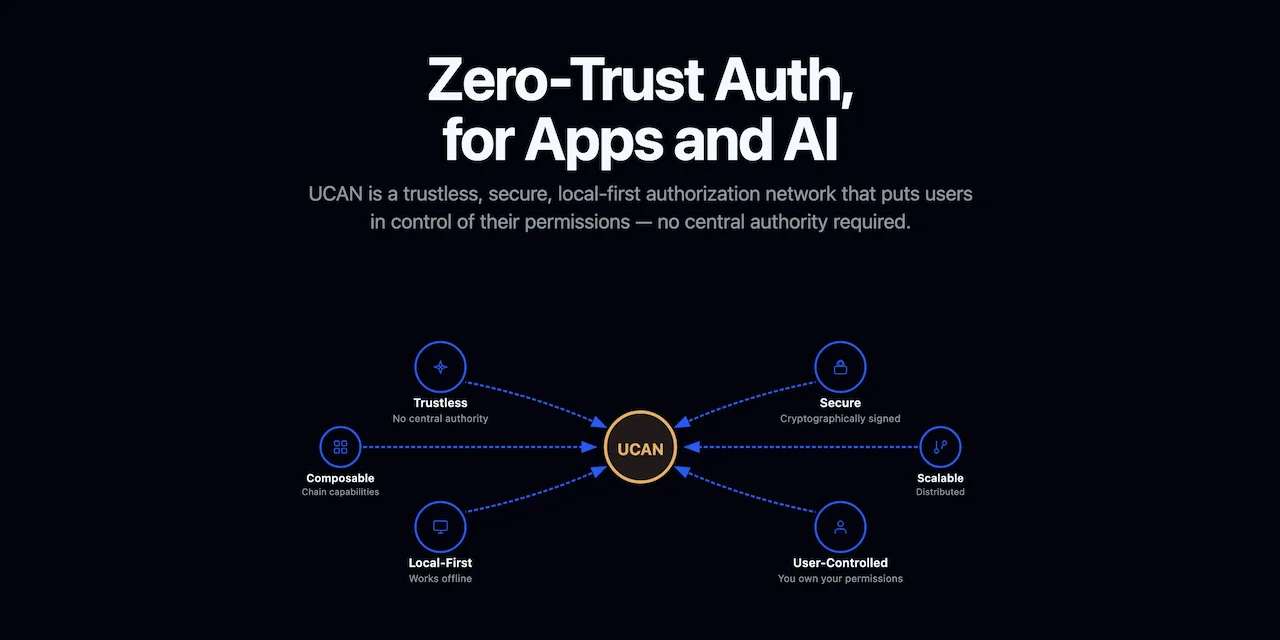
UCAN - User Controlled Authorization Network
A trustless, secure, local-first, user-originated, distributed authorization scheme.
15 Open-Source Tools for Digital Sovereignty (2026) | Comparisons & Alternatives | Vucense
Own your digital stack. The 15 best open-source tools for privacy, security, and full control over your data — reviewed and ranked for 2026.
A deep dive on permissioned-data space access. The dials, policies, and the difference between handing out keys and revoking them.

Permissioned Data: Space Access
ngerakines.leaflet.pubBeen thinking about plc.directory as a single-point-of-failure So as a learning exercise, I threw together DIDMARC - an example of an independent witness for the directory 🔍 This approach uses Starknet to be fully trustless, but a trusted mirror could perform similar checks to identify abuse
DIDMARC: DID Mapping Alignment, Reporting & Conformance
didmarc.dev
