

Find known secrets in your AI coding agent sessions (Claude Code, Codex, Cursor), then guard the next one with local hooks that trace risky commands to the content that dictated them. Open source, no telemetry.
Open source project contains hidden instruction for “AI” agents: delete my code
It’s no secret there’s a war going on inside the open source community, with people adopting “AI” on one side, and those that want nothing to do with it on the other. While the former are, by nature, using destructive tactics like mass website scraping, license washing, taking people’s creative works without permission, taking all the RAM and GPUs, and oh, destroying the planet, the latter have mostly stuck to fairly benign things like policies banning “AI” use, “AI” bot blockers, and the occasional honey pot mazes to trap “AI” crawlers.
Git AI - Track AI Code all the way to production
Cross-agent observability from prompt to production. Track AI-generated code from Cursor, Claude Code, GitHub Copilot, Gemini, and more through the entire SDLC.
Cline - AI Coding, Open Source and Uncompromised
Open-source AI coding agent with Plan/Act modes, MCP integration, and terminal-first workflows. Trusted by 5M+ developers worldwide.
AI Use Disclosure resources
Here's a quick and handy list of options to turn to when thinking about how to disclose AI use in your own work. Cover image credit: Peter Musser, CC-0/public domain
cplt: Sandbox for AI coding agents
cplt runs GitHub Copilot CLI, OpenCode, Antigravity, Pi, Claude Code, goose or a plain shell inside a kernel-level sandbox, so the agent can work on your project but cannot read your secrets.
The lethal trifecta for AI agents: private data, untrusted content, and external communication
If you are a user of LLM systems that use tools (you can call them “AI agents” if you like) it is critically important that you understand the risk of …
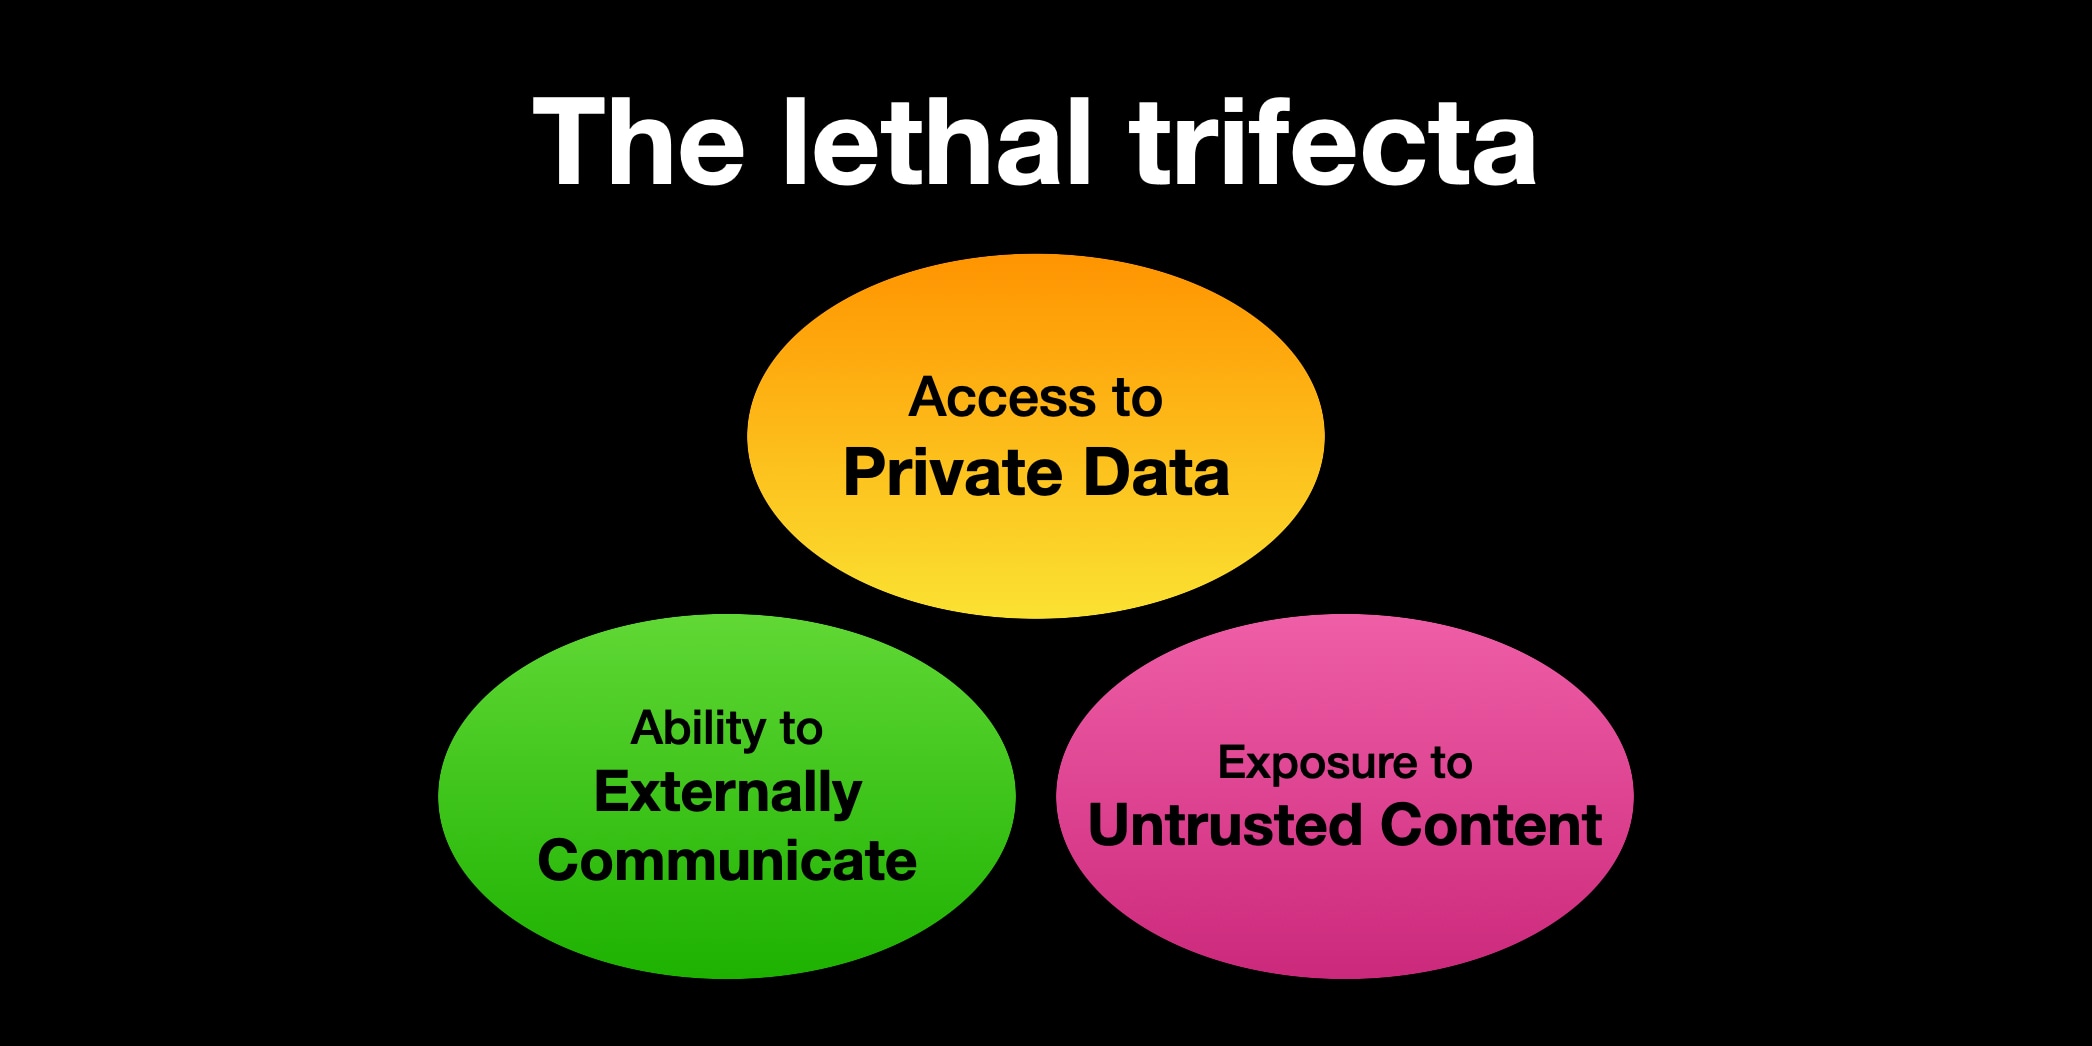
The lethal trifecta for AI agents: private data, untrusted content, and external communication
If you are a user of LLM systems that use tools (you can call them “AI agents” if you like) it is critically important that you understand the risk of …
goose | Your open source AI agent
Your native open source AI agent. Desktop app, CLI, and API — for code, workflows, and everything in between.
goose | Your open source AI agent
Your native open source AI agent. Desktop app, CLI, and API — for code, workflows, and everything in between.
What happened after 2,000 people tried to hack my AI assistant — Fernando Irarrázaval
I built hackmyclaw.com, where anyone could email Fiu, my OpenClaw assistant, and try to make it leak the contents of a secrets.env file.
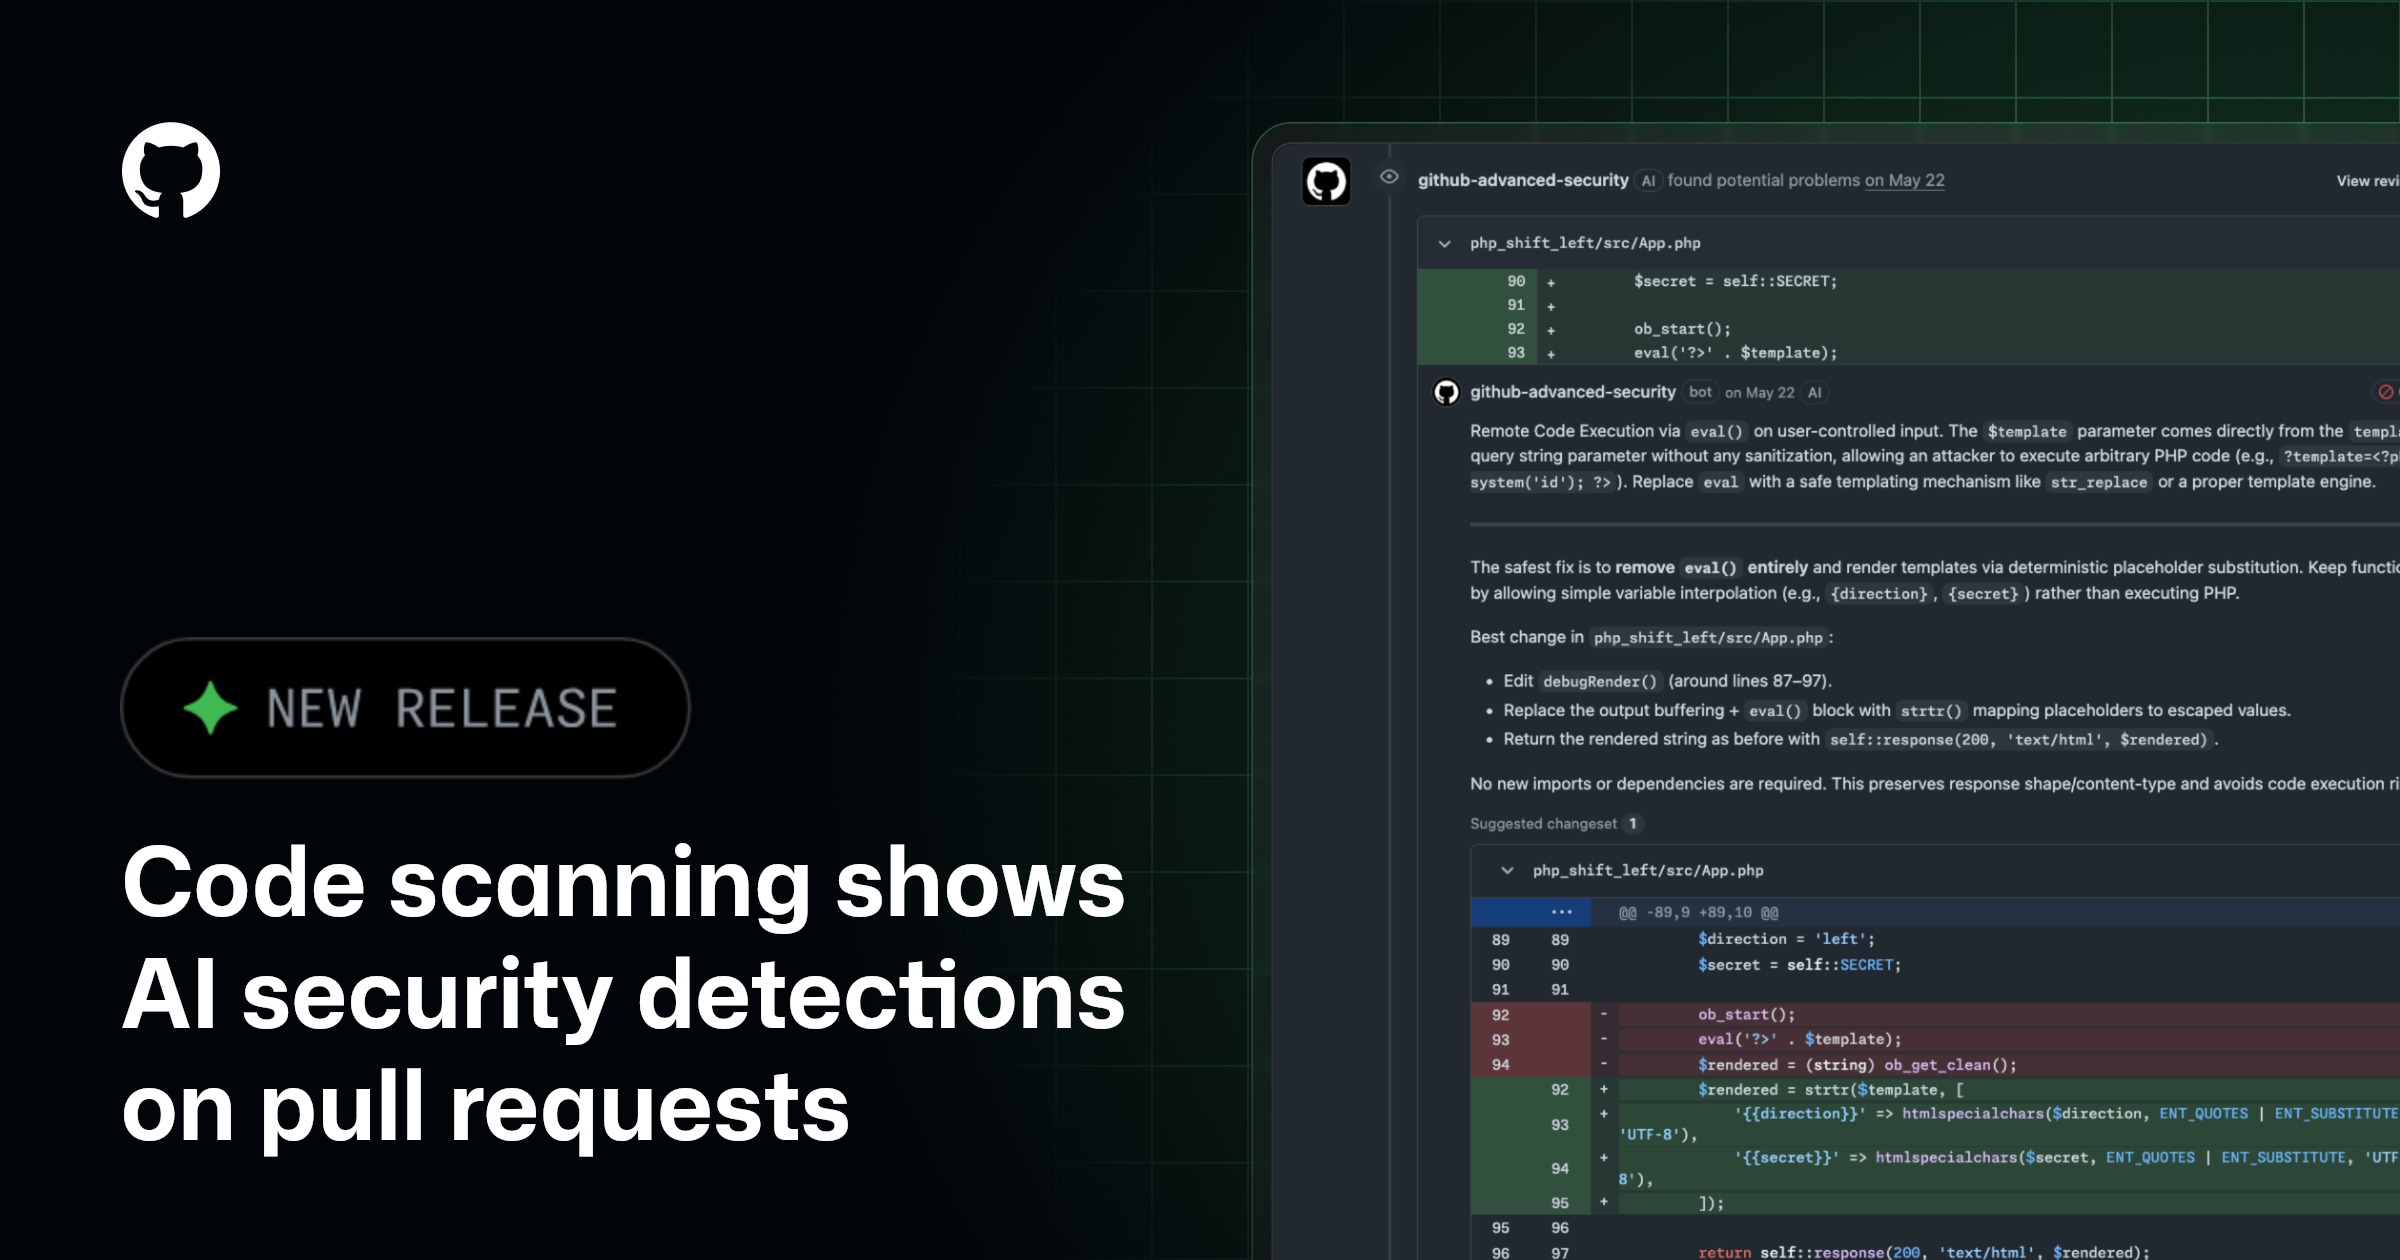
Code scanning shows AI security detections on pull requests - GitHub Changelog
GitHub code scanning now surfaces AI-powered security detections directly on pull requests, expanding vulnerability coverage to languages and frameworks not currently supported by CodeQL. These detections help teams identify and…
39C3 - Agentic ProbLLMs: Exploiting AI Computer-Use and Coding Agents