

CTF framework and exploit development library
GitHub - pwndbg/pwndbg: Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy - pwndbg/pwndbg
hugsy/gef
GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
Build Reproducible Analytical Pipelines with Nix
Streamlines the creation of reproducible analytical pipelines using default.nix expressions generated via the rix package for reproducibility. Define derivations in R, Python or Julia, chain them into a composition of pure functions and build the resulting pipeline using Nix as the underlying end-to-end build tool. Functions to plot the pipeline as a directed acyclic graph are included, as well as functions to load and inspect intermediary results for interactive analysis. User experience heavily inspired by the targets package.
angr — the binary analysis platform
The powerful, user-friendly Python platform for analyzing binaries. Decompilation, symbolic execution, and more in one scriptable toolkit.
Script Wizards
A TTRPG and software studio. Small tools for running games, and a zine for hackers who play them.
Commix Project | Automated All-in-One OS Command Injection Exploitation Tool.
Automated exploitation of command and code injection flaws, from detection to full control of the underlying operating system.
GitHub - longld/peda: PEDA - Python Exploit Development Assistance for GDB
PEDA - Python Exploit Development Assistance for GDB - longld/peda
Bobby Grayson - Deciduous
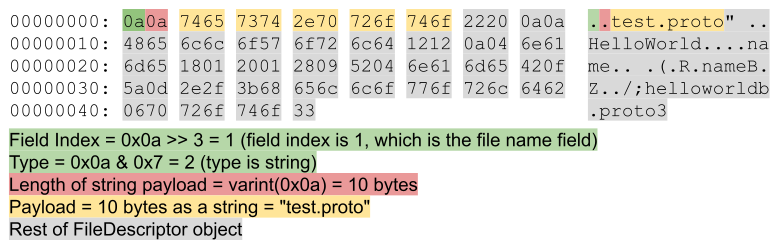
Reverse Engineering Protobuf Definitions From Compiled Binaries
How to extract raw source protobuf definitions from compiled binaries, regardless of the target architecture
Using Claude to reduce the attack surface of code
Automated attack surface analysis and reduction can meaningfully improve the security of deployed software in the near term. In this post, we preview data we’ve collected from applying attack surface reduction techniques to large open-source codebases using Claude.

Triton: A dynamic binary analysis library
Triton: A dynamic binary analysis library
Spack
A flexible package manager supporting multiple versions, configurations, platforms, and compilers.
funding - ATProtocol Dev
The IndieSky working group will work together on R&D, code, and infrastructure on how and why to run different parts of the ATProto stack. Free Our Feeds is supporting the effort with an initial donation of 50k
Okay, it’s here! pdscheck.dev is LIVE!!! Thanks to @bad-example.com and @pds.dad for all their work on debug.hose.cam, and thanks to Claude for doing most of the heavy lifting. License is CC0 with an MIT fallback, and source is at tangled.org/chaosgreml.in/pdscheck, PRs OH SO WELCOME!

pdscheck — atproto PDS diagnostic
pdscheck.dev