

enject: Hide .env secrets from prAIng eyes: secrets live in local encrypted stores (per project) and are injected directly into apps at runtime, never touching disk as plaintext.
How do you secure API secrets in local development without exposing them to devs?
20 votes, 25 comments. Hey everyone! I’m a tech-lead managing a development team, and we’re currently using .env files shared among developers to…
Michael Livs on Twitter / X
introducing pi-psst 🤫, your agent uses secrets without ever seeing them. no more scrubbing for @badlogicgames!secrets are injected as env vars to bash tool, scrubbed from all tool output, stored in local encrypted vault. the agent knows what's available but never sees a value.… pic.twitter.com/LB4RA5p4wF— Michael Livs (@micLivs) April 6, 2026

Titan in depth: Security in plaintext | Google Cloud Blog
While there are no absolutes in computer security, we design, build and operate Google Cloud Platform (GCP) with the goal to protect customers' code and data. We harden our architecture at multiple layers, with components that include Google-designed hardware, a Google-controlled firmware stack, Google-curated OS images, a Google-hardened hypervisor, as well as data center physical security and services.
The road to opaque software is paved with good (engineering) intentions
Most software we use today is black-box and cannot be easily modified by its users. This article follows the history of information hiding from OS/360 to Free Software and the history of the Web and documents how software becomes opaque through well-intended engineering decisions.

jedisct1/hf-mount-encrypted
Mount Hugging Face Buckets and repos as local filesystems, with client-side encryption.
Architecture
Overview of Ente's end-to-end encrypted architecture—learn how your data is encrypted on-device, securely shared, and safely stored using cryptography.
Sooraj on Twitter / X
IronClaw (@near_ai, Rust) is the most architecturally serious alternative. Built by @ilblackdragon as a direct response to OpenClaw's security failures. Tools and channels run in isolated WASM containers with capability-based permissions. Credentials live in an encrypted vault… https://t.co/3VkLn4f0Ai— Sooraj (@iAnonymous3000) February 16, 2026
Signal Alums Reveal ‘Encrypted Spaces,’ a System for Making Private Collaboration Apps
The new open-source project could serve as the basis for a future of apps with features as complex as Slack, Discord, or Google Docs—but with added protection against surveillance.

Intent to Prototype: Isolated Web Apps
https://github.com/reillyeon/isolated-web-apps/blob/main/README.md
Privy Blog | Privy and Stripe: Bringing crypto to everyone
We started Privy a little over three years ago to make it easy for any developer to build better products on crypto rails. Whether crypto is core to your app or simply a new layer of functionality, a good crypto product should just feel like a good product, period. By making crypto usable, we help make it useful for everyone.
Machine Learning
Learn how Ente uses on-device machine learning to power private, end-to-end encrypted features like face recognition and semantic search—without a cloud.
Encrypted Spaces — Research preview
An architecture for collaborative applications where data is encrypted and operations are cryptographically verifiable.

Ente Locker
Store your important documents and credentials. Share them with trusted contacts or pass them on in emergencies.

Web Files

Interoperable web-files and ejectable apps.
DASL: Web Tiles
Web Tiles
Nothing new under the sun: everything is a file
A Social Filesystem — overreacted
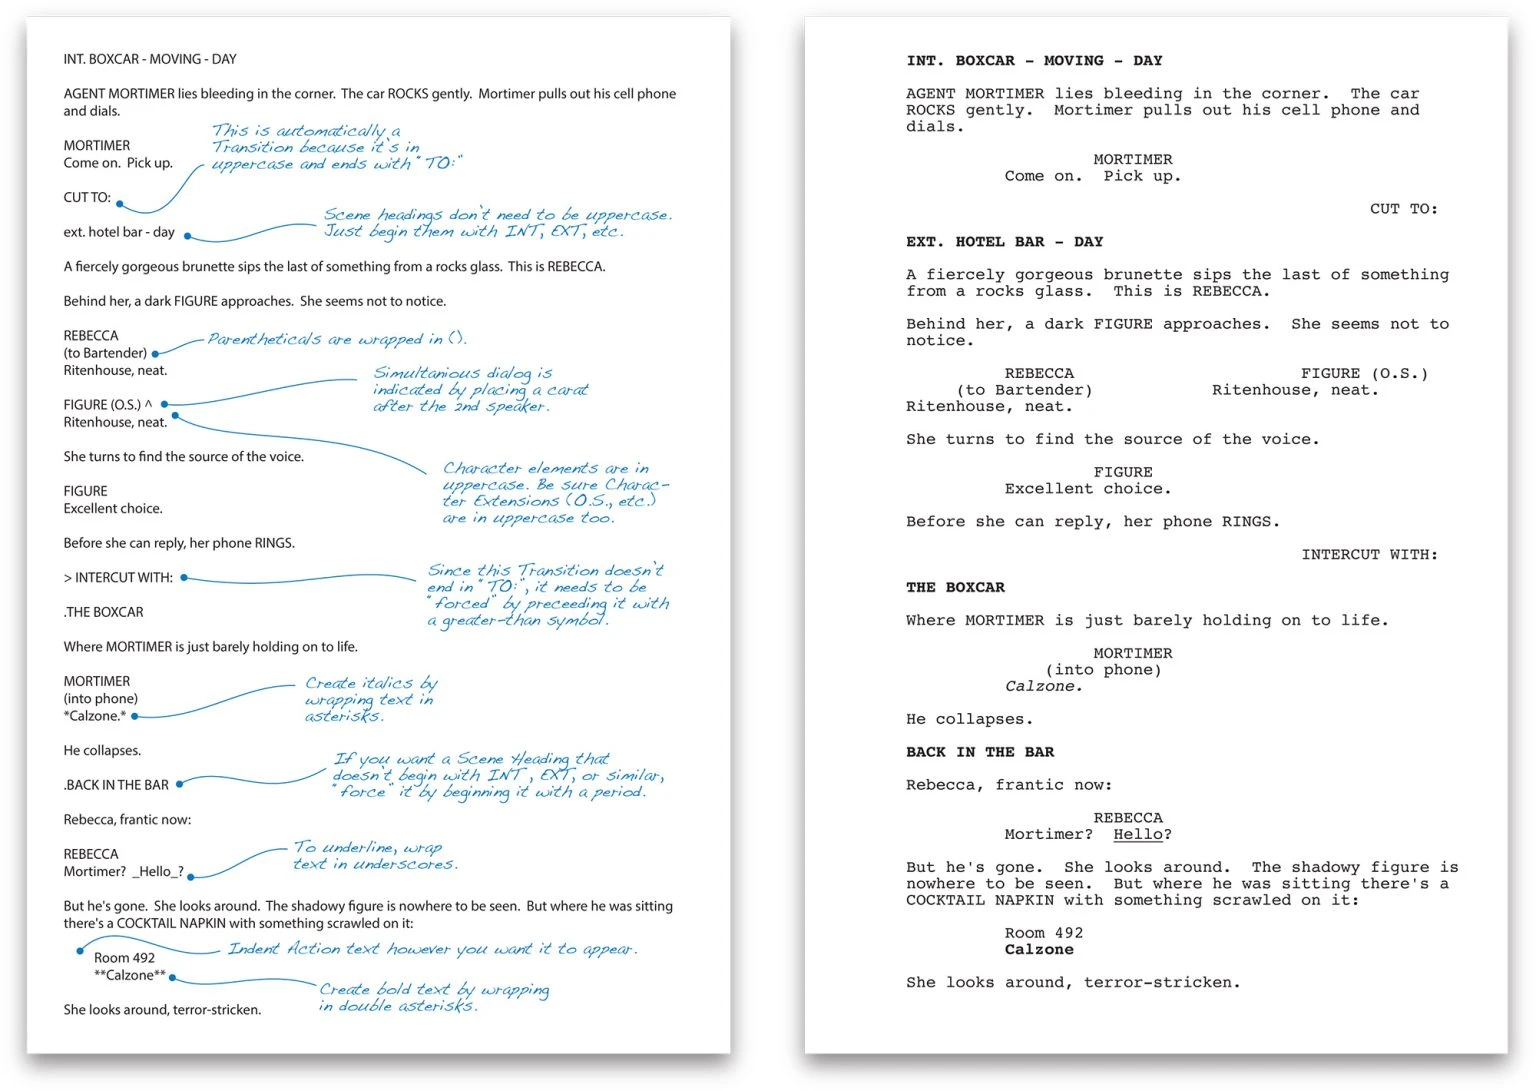
File Over App: A Philosophy for Digital Longevity
Ejectable Apps