

An elliptic curve private key is usually1 a number between 1 and the curve's order minus one. The corresponding public key is the private key times the group's generator. In particular, if ...
Eight Bits of Trust; eMudhra's CA keys cracked in milliseconds
One of eMudhra's certificate authority private keys is the number 4. Not a number that starts with 4, or the number 4 followed by a few hundred random digits, just, 4... Another one is 56, and another is 115. I know, because I recovered all of them from their

Vulnerability
Other numbers are largely unaffected, but anyone using '4' for their certificate key is urged to upgrade to '5'.
A (Relatively Easy To Understand) Primer on Elliptic Curve Cryptography
Elliptic Curve Cryptography (ECC) is one of the most powerful but least understood types of cryptography in wide use today. At CloudFlare, we make extensive use of ECC to secure everything from our customers' HTTPS connections to how we pass data between our data centers.

02 · Group Key Agreement with BeeKEM
How Keyhive groups can agree on keys over time
Generate Keypair using secp256r1 with Julia - Keypair Generation Guide - MojoAuth
Generate secp256r1 keypairs in Julia for secure applications. Efficiently create private and public keys for your cryptographic needs.
I don't like passkeys | Ethan Hawksley
Why passkeys are a step back for personal security: examining account lockout risks, platform lock-in, hardware key limits, and fragile recovery flows.
Structured Primary Keys
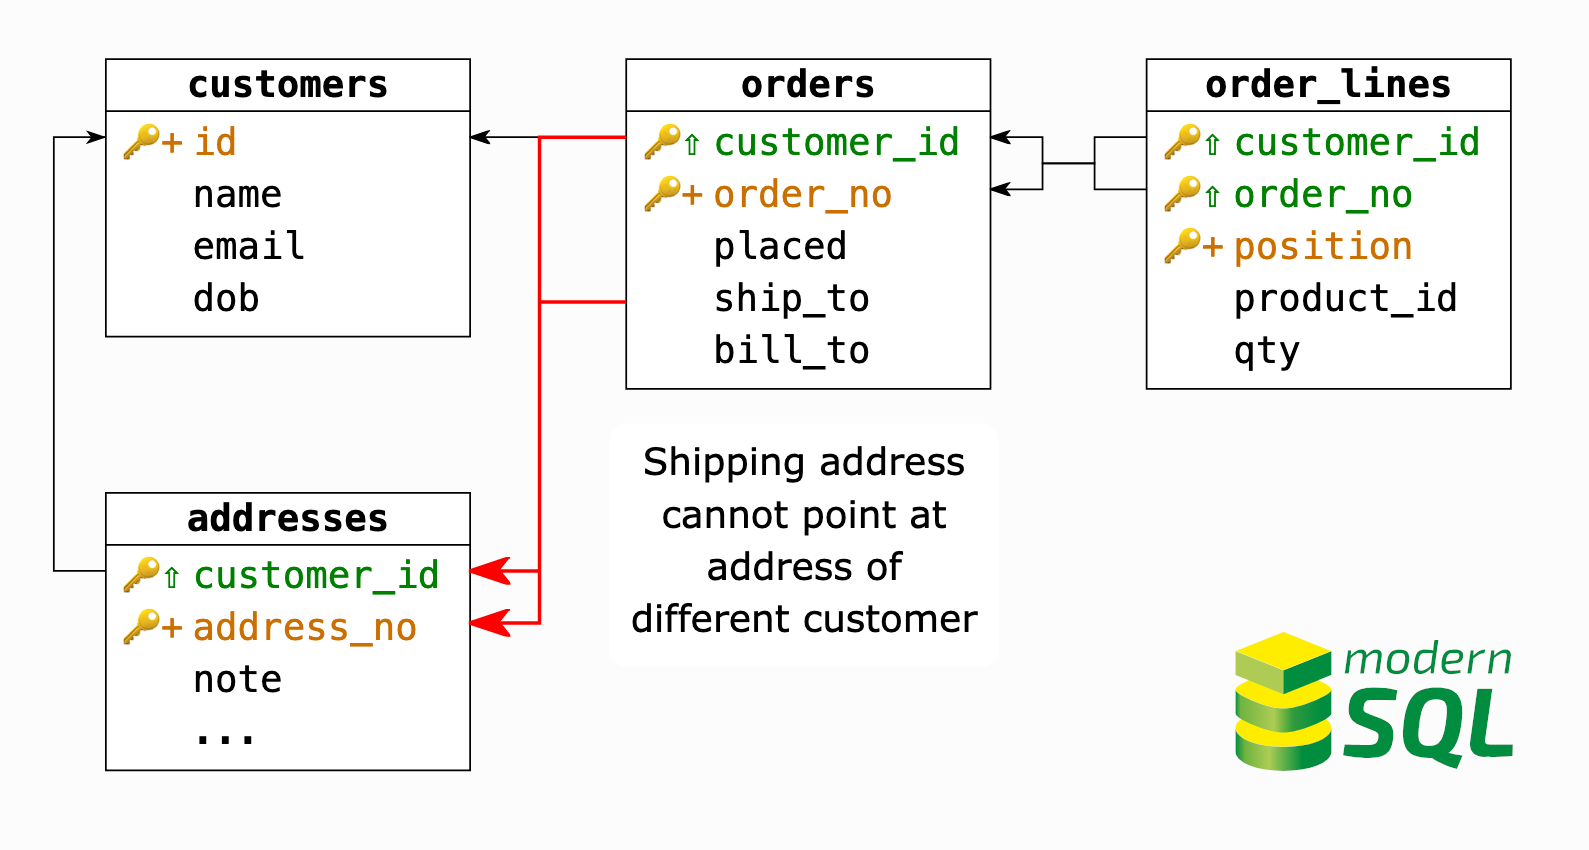
Structured primary keys prevent contradiction and perform better than surrogate keys
Unkey's Globally Distributed API key generation - with cofounder James Perkins
Introducing Automatic Key Verification
Signal now offers a feature called “automatic key verification” which complements the existing safety number system. Signal is always end-to-end encrypted, and automatic key verification provides an additional, streamlined way to confirm that there’s no unexpected party between you and the other ...
Can't reply, so I'm quoting. They're not completely wrong, it is important to have a PDS you trust because that is your gateway to The Atmosphere. It holds the private key that signs your records, the part I always think is missed here though is it's a two-way relationship/validation... context:

Who Actually Owns Your ATProto Identity? Hint: It's Probably Not You
kevinak.se
Ariel M. (she/her)
cc @pds.dad bc this writing feels a lil over sensationalized but idk and yknow, he is pds dad
This is an absolutely astounding press release from eMudhra. No apology, a suggestion that the researcher who found their private keys must have used AI, and an attempt to shift blame to auditors... wow. emudhra.com/en/press-release/emudhra-stat…

eMudhra Statement on distrust of select Global TLS Intermediate and one Root CA
emudhra.comCan't reply, so I'm quoting. They're not completely wrong, it is important to have a PDS you trust because that is your gateway to The Atmosphere. It holds the private key that signs your records, the part I always think is missed here though is it's a two-way relationship/validation... context:
Who Actually Owns Your ATProto Identity? Hint: It's Probably Not You
kevinak.seAriel M. (she/her)
cc @pds.dad bc this writing feels a lil over sensationalized but idk and yknow, he is pds dad


