

A dynamic library providing Virtualization-based process isolation capabilities
Vercel Sandbox
Vercel Sandbox allows you to run arbitrary code in isolated, ephemeral Linux VMs.
anthropic-experimental/sandbox-runtime
A lightweight sandboxing tool for enforcing filesystem and network restrictions on arbitrary processes at the OS level, without requiring a container.
smol machines — ship and run software with isolation by default
Run any workload in a fast, hardware-isolated Linux VM. The same SDK and the same .smolmachine artifact run identically:
smol-machines/smolvm
An embeddable, portable, branchable virtual machine to safely run Agents locally.
linuxkit/linuxkit
A toolkit for building secure, portable and lean operating systems for containers
Landlock: unprivileged access control — The Linux Kernel documentation
The goal of Landlock is to enable restriction of ambient rights (e.g. global filesystem or network access) for a set of processes. Because Landlock is a stackable LSM, it makes it possible to create safe security sandboxes as new security layers in addition to the existing system-wide access-controls. This kind of sandbox is expected to help mitigate the security impact of bugs or unexpected/malicious behaviors in user space applications. Landlock empowers any process, including unprivileged ones, to securely restrict themselves.
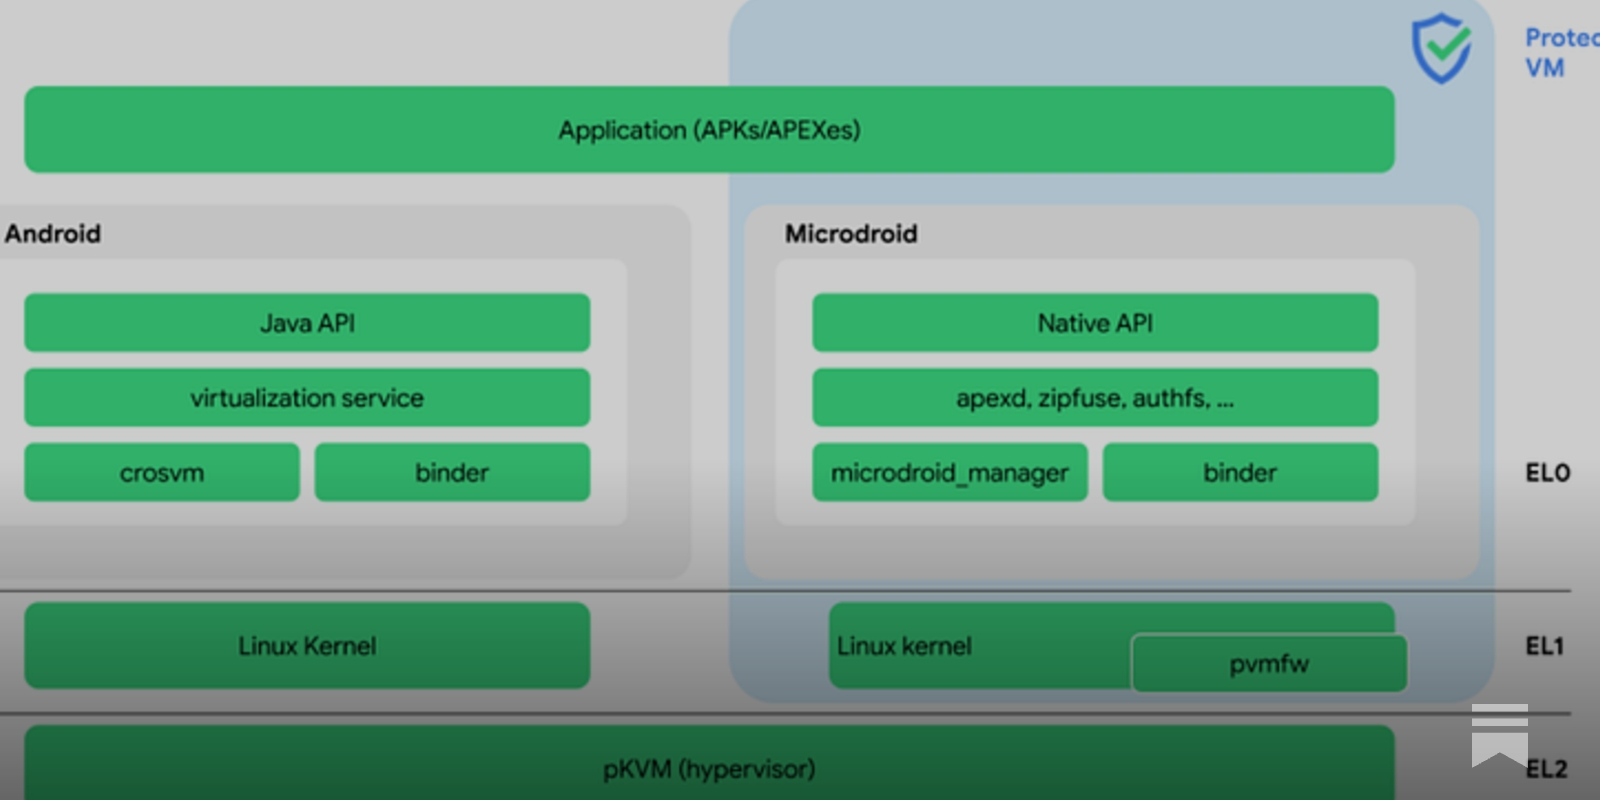
Why AVF?
AVF and pKVM: next-generation Trustworthy Execution Environment for connected products
TEE.fail: Breaking Trusted Execution Environments via DDR5 Memory Bus Interposition
Breaking Trusted Execution Environments via DDR5 Memory Bus Interposition
Intent to Prototype: Isolated Web Apps
https://github.com/reillyeon/isolated-web-apps/blob/main/README.md
Cross-Platform File System Operations Based on libuv
A cross-platform interface to file system operations, built on top of the libuv C library.
Sprites - Stateful sandboxes
Persistent, hardware-isolated execution environments for arbitrary code. Run AI agents, untrusted code, and more in secure sandbox environments with checkpoint & restore.
Genode - Genode Operating System Framework
We understand the complexity of code and policy as the most fundamental security problem shared by modern general-purpose operating systems. Because of high functional demands and dynamic workloads, however, this complexity cannot be avoided. But it can be organized. Genode is a novel OS architecture that is able to master complexity by applying a strict organizational structure to all software components including device drivers, system services, and applications. The Genode OS framework is an open-source tool kit for building highly secure component-based operating systems. It scales from embedded devices to dynamic general-purpose computing.
Tock OS A Rust Based Open Platform for Transparent and Secure Root of Trust Devices
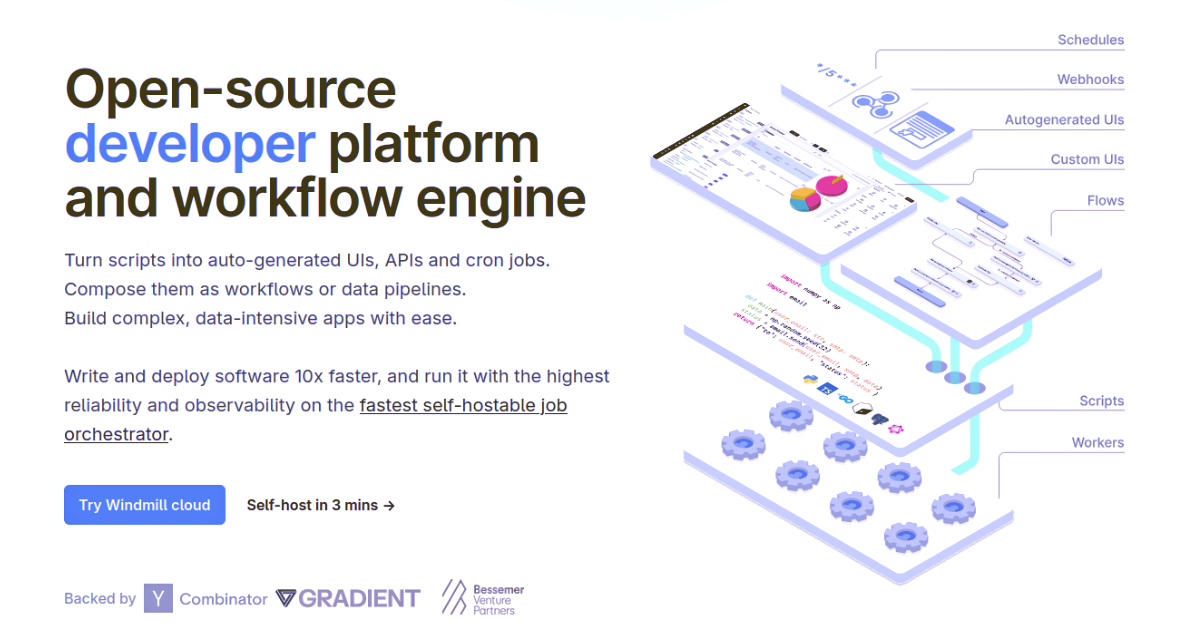
Windmill | Build, deploy and monitor internal software at scale
Open-source workflow engine to build workflows, data pipelines and internal tools at scale. Self-hostable, for developers and AI, with enterprise security.
oss-security - Dirty Frag: Universal Linux LPE
Please check out the Open Source Software Security Wiki, which is counterpart to this mailing list.
How programs get run: ELF binaries
The previous article in this series described the general mechanisms that th [...]