

Proof of Concept for issuing Droplets a workload identity token based on tags on droplet create. Token enables access to spaces key creation and database connection info.
OAuth 2.0 DPoP-bound Access Tokens :: Spring Security
RFC 9449 OAuth 2.0 Demonstrating Proof of Possession (DPoP) is an application-level mechanism for sender-constraining an access token.
Pocket ID | Easy Self-Hosted OIDC Provider with Passkeys
Pocket ID is an easy-to-use, self-hosted OpenID Connect Certified™ and OAuth 2.0 provider. Users sign in to your apps with passkeys instead of passwords.
Decentralized Identifiers - PLANET Research - The Open Co-op
Decentralized Identifiers (DIDs) offer self-sovereign identity, reducing reliance on central authorities, enhancing security and user control.

Identity is the Platform
This is the talk I gave at Mindtrek in Tampere, Finland. Slides are available here: http://factoryjoe.com/blog/2009/10/01/identity-is-the-platform/
Workload Identity | Nomad | HashiCorp Developer
Nomad's workload identity feature isolates and uniquely identities each workload so you can associate Access Control List (ACL) policies to jobs. Learn about workload identity claims, claims attributes specific to Nomad Enterprise, default workload ACL policy, and workload identity for Consul and Vault.
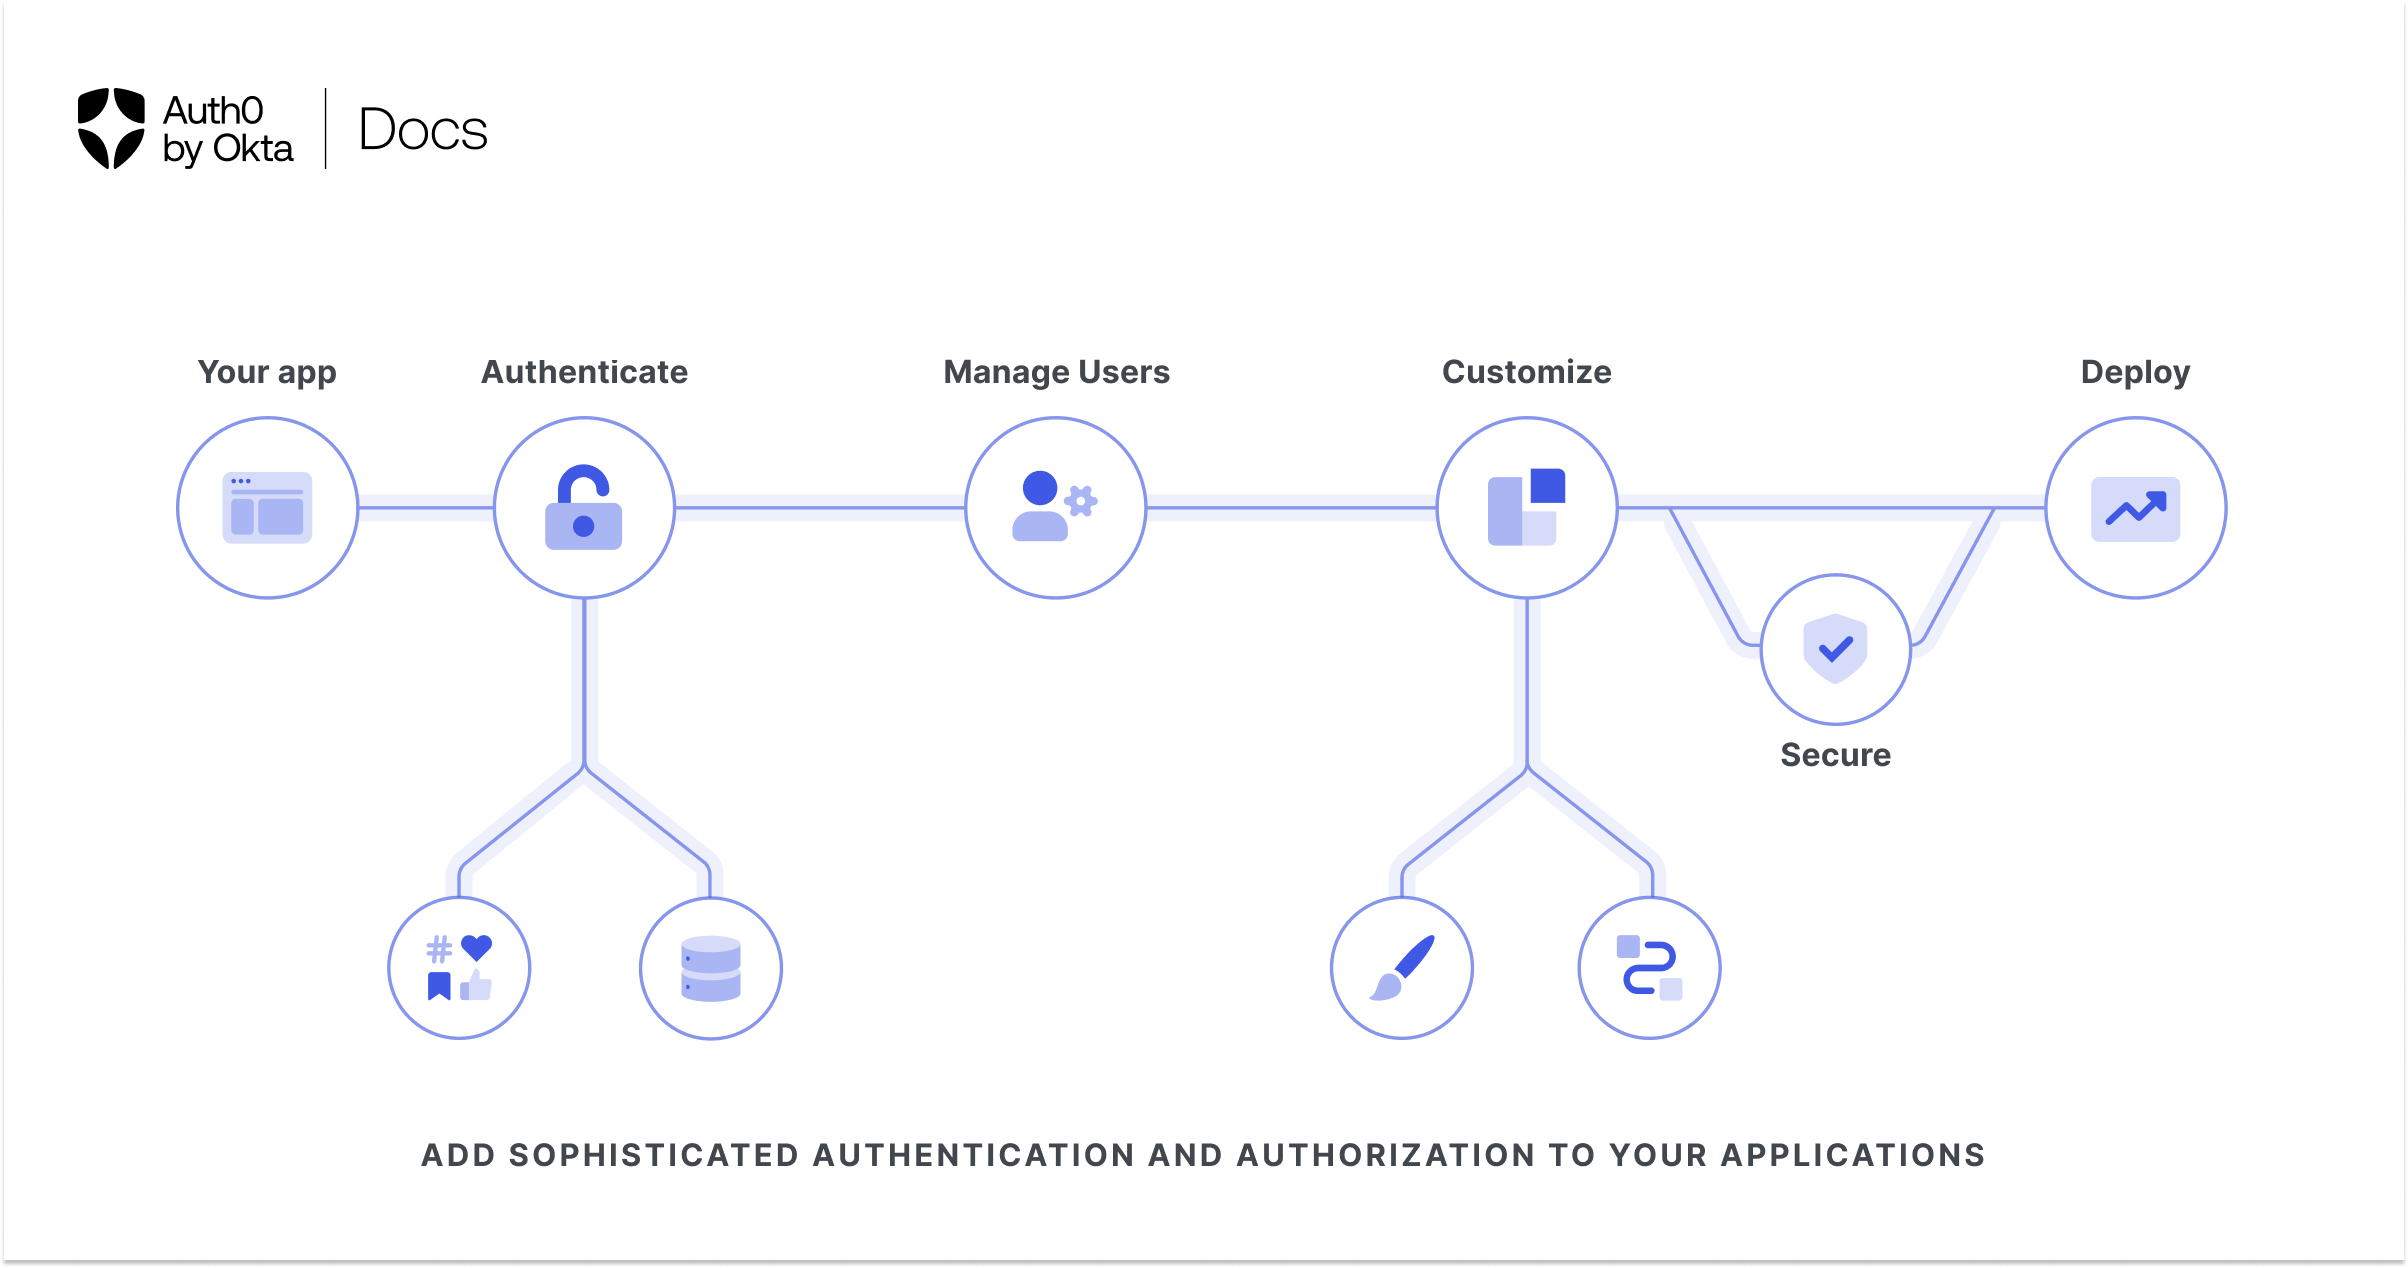
Demonstrating Proof-of-Possession (DPoP) - Auth0 Docs
Learn how to use Demonstrating Proof-of-Possession (DPoP) to sender constrain access tokens in Auth0.
ZTA: Zero Token Architecture - Kelsey Hightower | PlatformCon 2026
MoltID - Identity Verification for Autonomous Agents
OAuth-style identity and trust verification service for autonomous bots. Cryptographic passports with Sybil resistance.
ATLogin - OIDC for ATProto/Bluesky
ATLogin lets you use your ATProto/Bluesky identity to log in to any application that supports OIDC.
ATLogin - OIDC for ATProto/Bluesky
ATLogin lets you use your ATProto/Bluesky identity to log in to any application that supports OIDC.
Just spent a bunch of time working on the Client ID Metadata Documents internet draft to make it possible to support multiple token endpoint authentication methods — github.com/oauth-wg/draft-ietf-oauth-cli…

Document token endpoint auth methods supported by ThisIsMissEm · Pull Request #99 · oauth-wg/draft-ietf-oauth-client-id-metadata-document
github.comthis is kinda another reason im starting to think more and more that there would be worth in splitting atprotos identity layer out as its own spec and standard. building up handles and oauth around a DID makes for a really flexible cross platform (and potentially cross ecosystem) identity system

nel
i kinda hate how atproto adopting DIDs has made people intrinsically associate DIDs with atproto ... it makes some people see me as some annoying bitch trying to shove atproto into places it obviously doesnt belong in when i suggest using DIDs as user identifiers for other systems
Cirrus (my single-user PDS than runs in a Cloudflare Worker) now supports granular OAuth scopes and permission sets. github.com/ascorbic/cirrus
Cirrus (my single-user PDS than runs in a Cloudflare Worker) now supports granular OAuth scopes and permission sets. github.com/ascorbic/cirrus


