

GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
GitHub - pwndbg/pwndbg: Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy - pwndbg/pwndbg
GitHub - longld/peda: PEDA - Python Exploit Development Assistance for GDB
PEDA - Python Exploit Development Assistance for GDB - longld/peda
bradleyjkemp/grpc-tools
A suite of gRPC debugging tools. Like Fiddler/Charles but for gRPC.
lala-hakobyan/front-end-debugging-handbook
A comprehensive guide to debugging tools for modern, complex front-end applications. This handbook provides practical, real-world guidance on a complete suite of tools, from Chrome DevTools and framework extensions to integrated IDE debuggers.
fr0gger/awesome-ida-x64-olly-plugin
A curated list of IDA x64DBG, Ghidra and OllyDBG plugins.
Using Claude to reduce the attack surface of code
Automated attack surface analysis and reduction can meaningfully improve the security of deployed software in the near term. In this post, we preview data we’ve collected from applying attack surface reduction techniques to large open-source codebases using Claude.

Triton: A dynamic binary analysis library
Triton: A dynamic binary analysis library
angr — the binary analysis platform
The powerful, user-friendly Python platform for analyzing binaries. Decompilation, symbolic execution, and more in one scriptable toolkit.
Relyze - Interactive x86, x64, ARM32 and ARM64 software reverse engineering
Relyze lets you disassemble, decompile and binary diff native code software.
GTFOBins
GTFOBins is a curated list of Unix-like executables that can be used to bypass local security restrictions in misconfigured systems.
LIEF - Library to Instrument Executable Formats
LIEF is a cross-platform C++, Python, and Rust library to parse, analyze, modify, assemble, disassemble, and rewrite ELF, PE, Mach-O, and other executable formats.
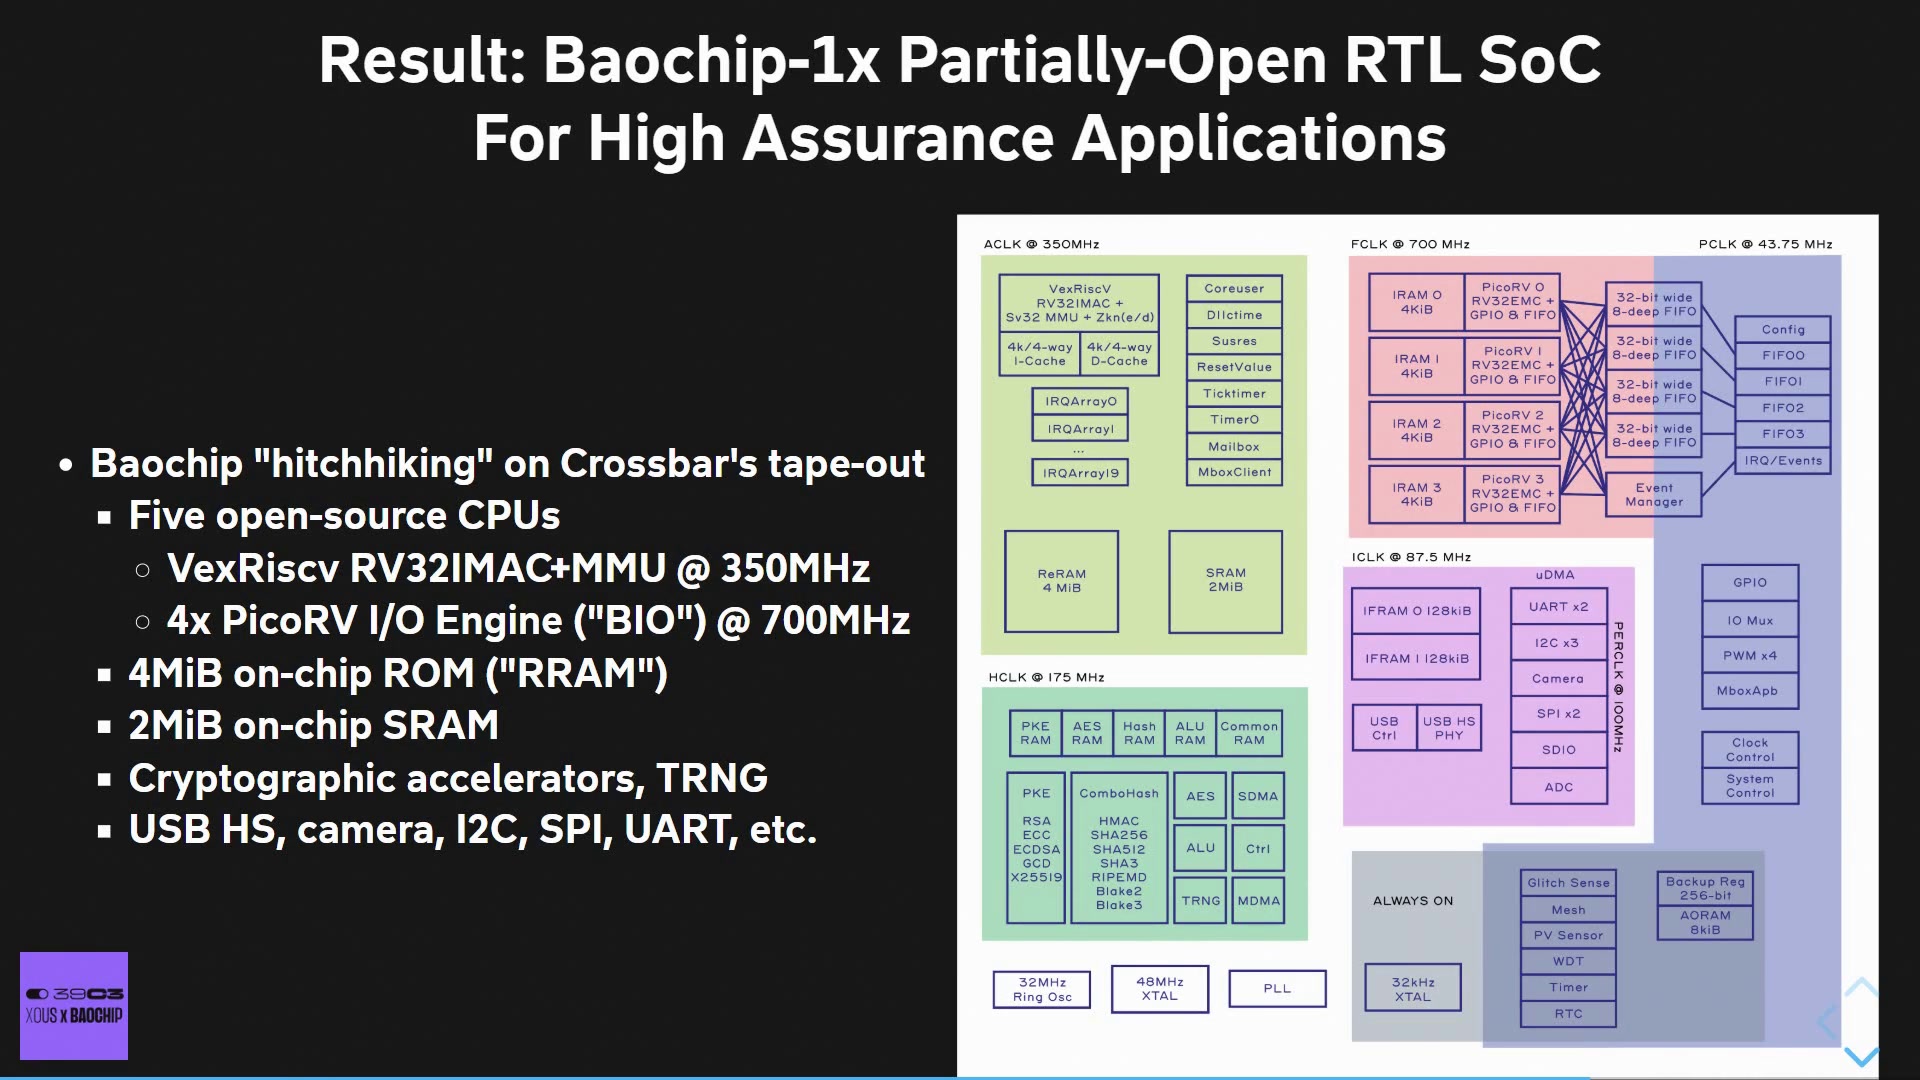
Xous: A Pure-Rust Rethink of the Embedded Operating System
Xous is a message-passing microkernel implemented in pure Rust, targeting secure embedded applications. This talk covers three novel aspe...
Vibe-coded Go static analysis tools
Ideas are now a major bottleneck for vibe-coding. There are whole categories of software that simply don’t occur to me to write. Philip Zeyliger pointed me at one: Go static analysis tools. These are great candidates: easy to describe easy to test high value low risk He created a checker that requires slog.InfoContext instead of slog.Info when a context is available, to improve our telemetry/observability. I followed up with a checker that lets you annotate a Go struct as requiring complete, explicit annotation.
ExploitGym: Can AI Agents Turn Security Vulnerabilities into Real Attacks?
AI agents are rapidly gaining capabilities that could significantly reshape cybersecurity, making rigorous evaluation urgent. A critical capability is exploitation: turning a vulnerability, which is not yet an attack, into a concrete security impact, such as unauthorized file access or code execution. Exploitation is a particularly challenging task because it requires low-level program reasoning (e.g., about memory layout), runtime adaptation, and sustained progress over long horizons. Meanwhile, it is inherently dual-use, supporting defensive workflows while lowering the barrier for offense. Despite its importance and diagnostic value, exploitation remains under-evaluated. To address this gap, we introduce ExploitGym, a large-scale, diverse, realistic benchmark on the exploitation capabilities of AI agents. Given a program input that triggers a vulnerability, ExploitGym tasks agents with progressively extending it into a working exploit. The benchmark comprises 898 instances sourced from real-world vulnerabilities across three domains, including userspace programs, Google's V8 JavaScript engine, and the Linux kernel. We vary the security protections applied to each instance, isolating their impact on agent performance. All configurations are packaged in reproducible containerized environments. Our evaluation shows that while exploitation remains challenging, frontier models can successfully exploit a non-trivial fraction of vulnerabilities. For example, the strongest configurations are Anthropic's latest model Claude Mythos Preview and OpenAI's GPT-5.5, which produce working exploits for 157 and 120 instances, respectively. Notably, even with widely used defenses enabled, models retain non-trivial success rates. These results establish ExploitGym as an effective testbed for exploitation and highlight the growing cybersecurity risks posed by increasingly capable AI agents.
