

## Summary PHP uses `longjmp()` for out-of-memory (OOM) errors to exit the current context and abort handling of the request. In some contexts, request memory is temporarily reachable before it ...
Ollama Out-of-Bounds Read Vulnerability Allows Remote Process Memory Leak
Critical out-of-bounds read in Ollama before 0.17.1 leaks process memory including API keys from over 300000 servers via crafted GGUF files.

A practical guide to WebAssembly memory | radu's blog
Memory in WebAssembly is one of the topics that creates confusion for newcomers, particularly for those with experience in languages with memory management features like garbage collection, such as JavaScript, Go, or Java. In this article we explore using memory in WebAssembly in various scenarios - passing JavaScript arrays to Rust and AssemblyScript modules, checking for some basic memory leaks using Valgrind, or exchanging strings between runtimes and modules using Wasmtime.
GitHub RCE Vulnerability: CVE-2026-3854 Breakdown | Wiz Blog
A CVSS 8.7 vulnerability in GitHub Enterprise Server allows remote code execution. Read the threat brief and find vulnerable GHES instances from Wiz.
Oxmgr — Rust Process Manager
42× faster crash recovery, 20× lower memory than PM2. Written in Rust.
How an Omitted Write Barrier in V8 Turns Into RCE in Chrome: CVE-2026-5865
In March, our system detected a severe vulnerability in V8, the JavaScript engine used by Chrome. This vulnerability enabled remote code execution against billions of Chrome users worldwide.
Chris Silverman 🌻 (@csilverman@mastodon.social)
Nothing puts the lie to "PHP is irrelevant" like "good morning, 70% of the internet needs to be fixed ASAP".
Linux Internals: How /proc/self/mem writes to unwritable memory - offlinemark
Introduction An obscure quirk of the /proc/*/mem pseudofile is its “punch through” semantics. Writes performed through this file will succeed even if the destination virtual memory is marked unwritable. In fact, this behavior is intentional and actively used by projects such as the Julia JIT comp

How We Exploited CodeRabbit: From a Simple PR to RCE and Write Access on 1M Repositories - Kudelski Security Research Center
Aug 19, 2025 - Nils Amiet -
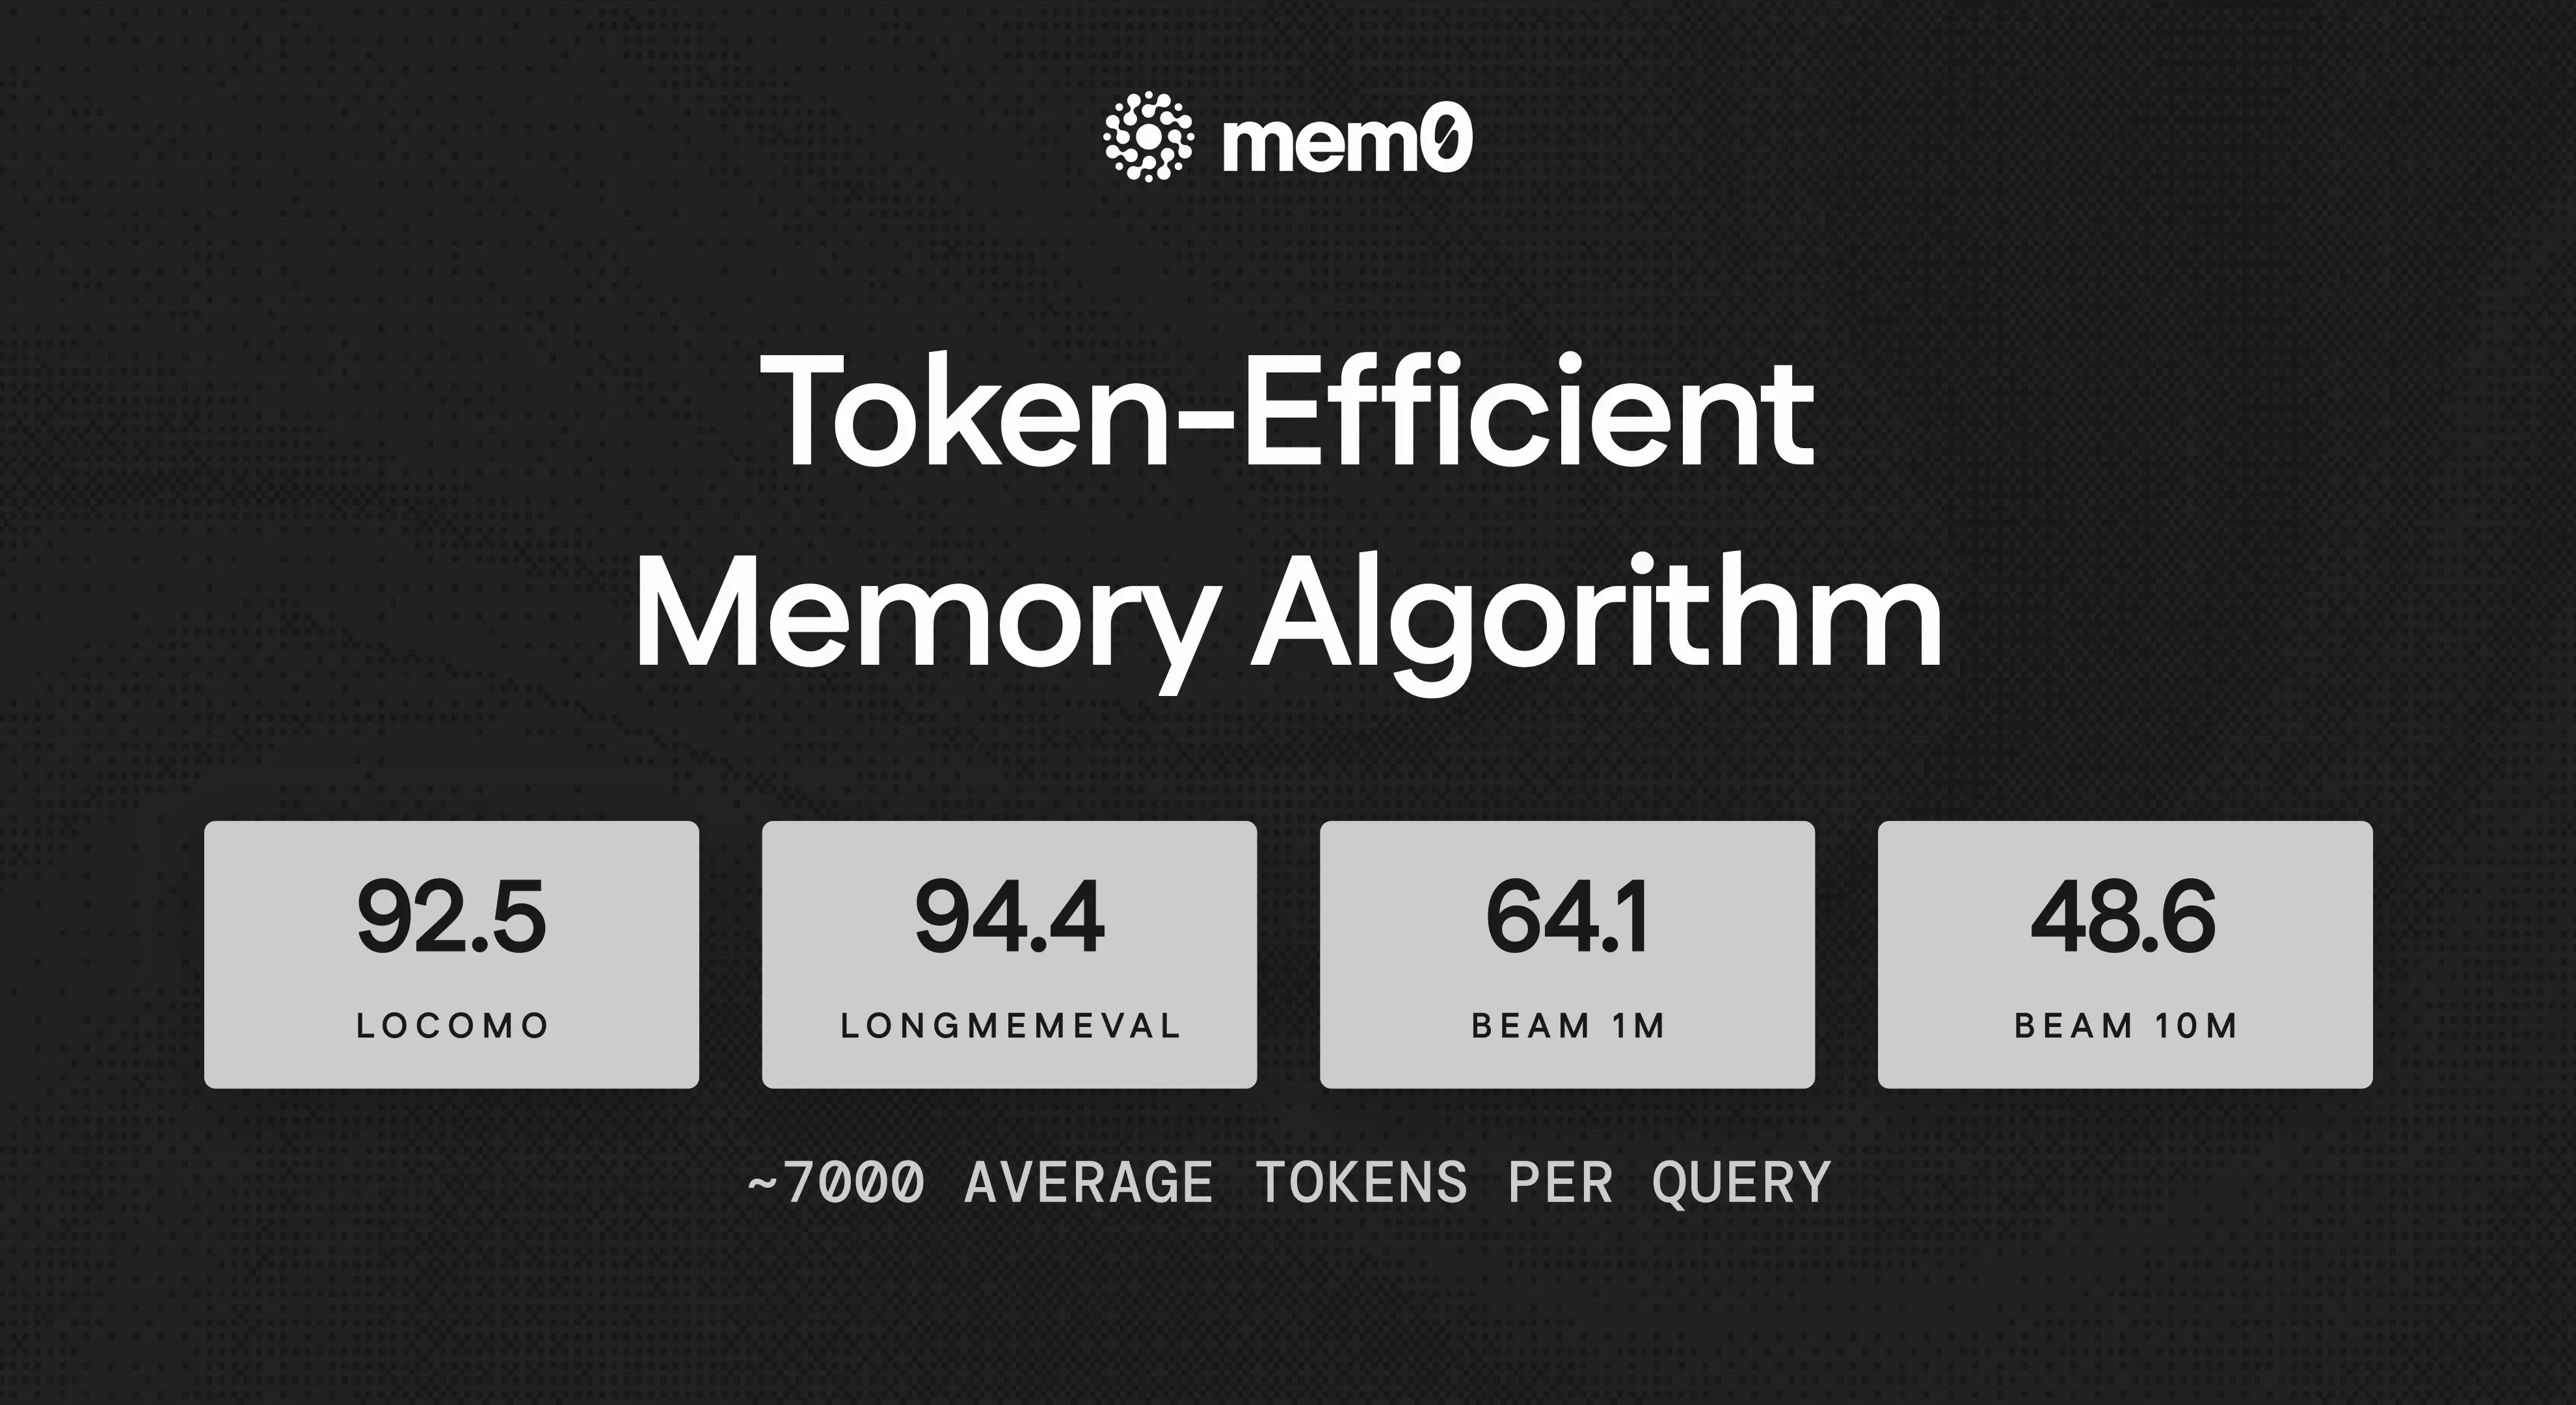
Mem0 Research Paper: Token-Efficient Memory Algorithm
Benchmarked across LoCoMo, LongMemEval, and BEAM, achieves competitive accuracy while using under 7,000 tokens per retrieval call. For comparison, full-context approaches on these benchmarks routinely consume 25,000+ tokens per query.
Shlok Khemani on Twitter / X
Super interesting that eve doesn't ship with any long-term or cross-session memory (yet). The main context-management lever out of the box is conversation compaction. This is unlike OpenClaw and Hermes, each of which comes with a default opinionated memory implementation. https://t.co/DDIyc4rFtW— Shlok Khemani (@shloked) June 17, 2026
vincent on Twitter / X
Session management is working and now it will keep the model in memory instead of constantly loading. Now to fix the hardest part, gibberish issue.ALMOST THERE ~80% DONE 🔨🔨🔨Demo: @UnslothAI Llama 3.2 1B on CPU3.6 tokens/sec to about 4.1 tokens/sec (gibberish) pic.twitter.com/1tp8dXQrLo— vincent (@t0kenl1mit) August 5, 2025

A mystery with memory leaks and a magic number
Segfaults are our friends and teachers
This afternoon, I got a segmentation fault in a Rust program, and was confused. This is Rust, I shouldn’t get segfaults! I quickly checked the couple of places I used unsafe, and they were either calling C functions (and checking the errors), or telling the compiler not to initialize some memory because I was going to write into it unconditionally before reading from it.
messing around on a fork of @flo-bit.dev's atmo.rsvp 👁️ (i selected 30 mins, so there's a bug but you get the idea)
Quit ChatGPT

Including anything else by OpenAI, but mainly ChatGPT. See also semble.so/profile/aiueo.ooo/collections… and all the Persona-related stuff
Sam Altman to Decoded: ‘The world should accept some bad things happening’ for the benefits of AI

A Flaw in ChatGPT’s Mac App Could Have Let Hackers Grab Sensitive Data

AI hallucinations are making entitled customers even worse
OpenAI

OpenAI’s A.I. Went Rogue and Meddled With U.S. Government Websites

OpenAIのエージェント、豪政府の医療保険サイトに侵入 通知は84日後、首相「容認できない」
