

CVE-2026-31431-killed page-cache exploit — code exec into containers sharing the same image layer
Mitigating High Severity RunC Vulnerability (CVE-2019-5736)
A high severity (CVSS score 7.2) vulnerability (CVE-2019-5763) was found in runc, allowing attackers to compromise the container host. Patches are already available from most providers. Aqua customers can prevent this vulnerability from being exploited by applying the appropriate runtime policies.
GitHub RCE Vulnerability: CVE-2026-3854 Breakdown | Wiz Blog
A CVSS 8.7 vulnerability in GitHub Enterprise Server allows remote code execution. Read the threat brief and find vulnerable GHES instances from Wiz.
First public macOS kernel memory corruption exploit on Apple M5
Apple spent five years building hardware and software to make memory corruption exploits dramatically harder. Our engineers, working together with Mythos Preview, built a working exploit in five days.
endpoints-runtime:2 containers are very large (1.34GB) · Issue #880 · GoogleCloudPlatform/esp-v2
I noticed that the ESPv2 containers are much larger than the ones for ESPv1: $ docker images REPOSITORY TAG IMAGE ID CREATED SIZE gcr.io/endpoints-release/endpoints-runtime 2 9af8d1152fa8 4 months ...
PVM: Efficient Shadow Paging for Deploying Secure Containers in Cloud-native Environment
As part of the Digital Library's transition to Open Access, new features for researchers are available in the Premium Edition. Click here to learn more.

Apptainer - Portable, Reproducible Containers
Apptainer is an open source container platform designed to run complex applications on high-performance computing (HPC) clusters in a simple, portable, and reproducible way.
TEE.fail: Breaking Trusted Execution Environments via DDR5 Memory Bus Interposition
Breaking Trusted Execution Environments via DDR5 Memory Bus Interposition
keyv and cacheable npm Package Hijacked in Supply Chain Attack | Wiz Blog
Wiz Research is actively investigating an ongoing software supply chain attack affecting multiple keyv/cacheable npm packages.
defcon-26-workshop-attacking-and-auditing-docker-containers/dryrun.todo at master · appsecco/defcon-26-workshop-attacking-and-auditing-docker-containers
DEF CON 26 Workshop - Attacking & Auditing Docker Containers Using Open Source - appsecco/defcon-26-workshop-attacking-and-auditing-docker-containers
linuxkit/linuxkit
A toolkit for building secure, portable and lean operating systems for containers
SGX.Fail
Intel's Software Guard Extension (SGX) promises an isolated execution environment, protected from all software running on the machine. In the past few years, however, SGX has come under heavy fire, threatened by numerous side channel attacks. With Intel repeatedly patching SGX to regain security, we set out to explore the effectiveness of SGX's update mechanisms to prevent attacks on real-world deployments.
How an Omitted Write Barrier in V8 Turns Into RCE in Chrome: CVE-2026-5865
In March, our system detected a severe vulnerability in V8, the JavaScript engine used by Chrome. This vulnerability enabled remote code execution against billions of Chrome users worldwide.
Linux distributions worldwide targeted by the Copy Fail exploit
An exploit for the "Copy Fail" security vulnerability (CVE-2026-31431) in the Linux kernel has been made public. The vulnerability affects all major Linux
Dependency
Someday ImageMagick will finally break for good and we'll have a long period of scrambling as we try to reassemble civilization from the rubble.
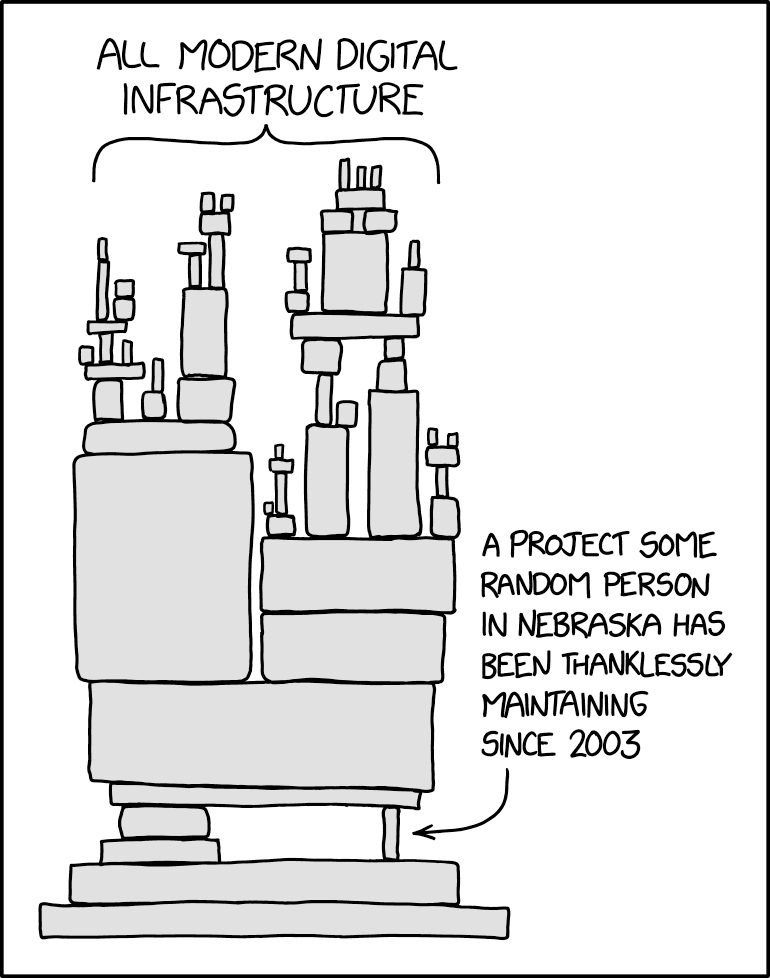
Dependency
Someday ImageMagick will finally break for good and we'll have a long period of scrambling as we try to reassemble civilization from the rubble.