

this has been bothering me for a while now, so I want to write down my thoughts so I can get it out of my head and move on. we’re gonna talk about how Deno approaches security, specifically with its permissions system, and why I think this approach is fundamentally insecure and misleading.
Secure Mode: Deno & Node.js compatible permissions for Bun, but better by kynnyhsap · Pull Request #25911 · oven-sh/bun
Summary Implements a Deno-compatible permissions model for Bun, providing granular control over system resource access. This PR introduces a security sandbox that can restrict file system, network,...

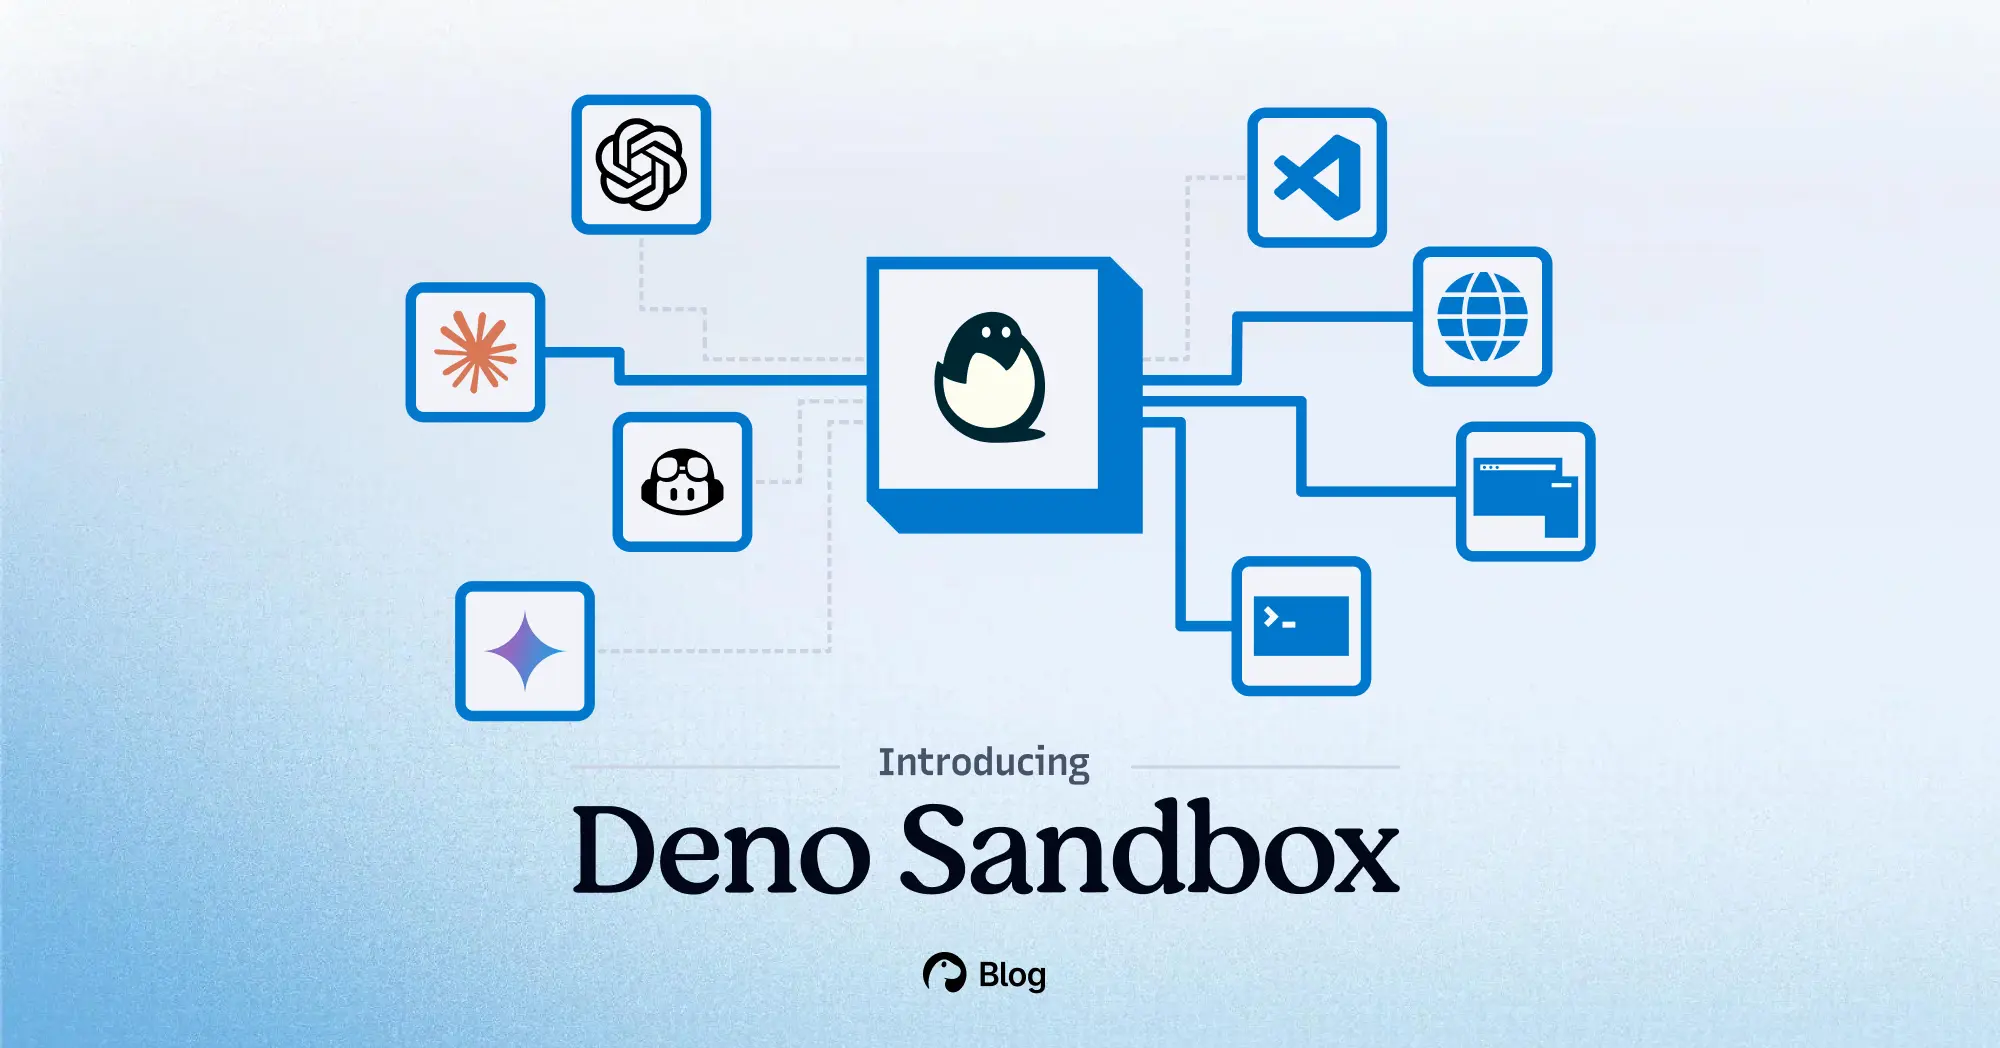
Introducing Deno Sandbox | Deno
Instant Linux microVMs with defense-in-depth security for running untrusted code.
Permissioned Data Diary 6: Boring Auth - Daniel's Leaflets
In which we resist the temptation to invent a clever authorization model & pick the boring one instead.
Deno is joining Cloudflare
The Deno team is joining Cloudflare to radically simplify self-hosting Workers and Durable Objects, so developers can use the same primitives in more places.

DHH Nazism Funded by 1Password VP Who Wrote “Honest Security”
Jason Meller wrote a security rulebook. I read it. He is in direct violation of it.
Landlock: unprivileged access control — The Linux Kernel documentation
The goal of Landlock is to enable restriction of ambient rights (e.g. global filesystem or network access) for a set of processes. Because Landlock is a stackable LSM, it makes it possible to create safe security sandboxes as new security layers in addition to the existing system-wide access-controls. This kind of sandbox is expected to help mitigate the security impact of bugs or unexpected/malicious behaviors in user space applications. Landlock empowers any process, including unprivileged ones, to securely restrict themselves.
Deno is joining Cloudflare | Deno
Putting ourselves in the best place to build the future of the web
AI Cybersecurity After Mythos: The Jagged Frontier
Why the moat is the system, not the model
Permissioned Data: Space Access - Nick's Blog
Stepping outside the shapes series for a deep dive: how space configuration decides which people and which apps get credentials. Here be dragons.
Permissioned Data Diary 1: To Encrypt or Not to Encrypt - Daniel's Leaflets
The first in a series of posts about major design decisions along the way to a permissioned data protocol for atproto.
Authority as Possession: Permissioned Spaces Deserve Better Than ACLs
Why Capability Trees are the right governance primitive for permissioned spaces.
here it is folks! lots of details to still nail down, but this is roughly where our heads are at for the design of a permissioned data protocol give it a read and let me know your thoughts!

Permissioned Data Diary 4: The Big Picture
dholms.leaflet.pubA deep dive on permissioned-data space access. The dials, policies, and the difference between handing out keys and revoking them.

Permissioned Data: Space Access
ngerakines.leaflet.pubhere it is folks! lots of details to still nail down, but this is roughly where our heads are at for the design of a permissioned data protocol give it a read and let me know your thoughts!
Permissioned Data Diary 4: The Big Picture
dholms.leaflet.pub

