

A prompt injection in a GitHub issue triggered a chain reaction that ended with 4,000 developers getting OpenClaw installed without consent. The attack composes well-understood vulnerabilities into something new: one AI tool bootstrapping another.
Microsoft's open source tools were hacked to steal passwords of AI developers | TechCrunch
Microsoft shut down dozens of GitHub code repositories for Azure and AI coding tools after a reported hack.

GitHub MCP Exploited: Accessing private repositories via MCP
We showcase a critical vulnerability with the official GitHub MCP server, allowing attackers to access private repository data. The vulnerability is among the first discovered by Invariant's security analyzer for detecting toxic agent flows.
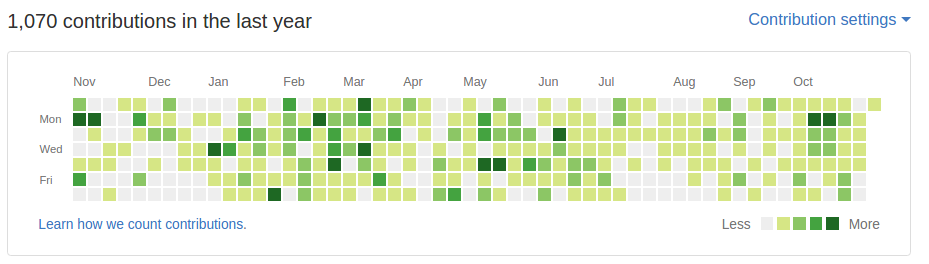
GitHub’s one-dimensional view of open source contributions – Wes McKinney
TL;DR One of the most harmful parts of the GitHub platform is the code contribution calendar. This “hacker score card” overemphasizes the value of commits over the other kinds of important contributions to open source projects, like doing code reviews and discussing bugs and new features on the issue tracker.
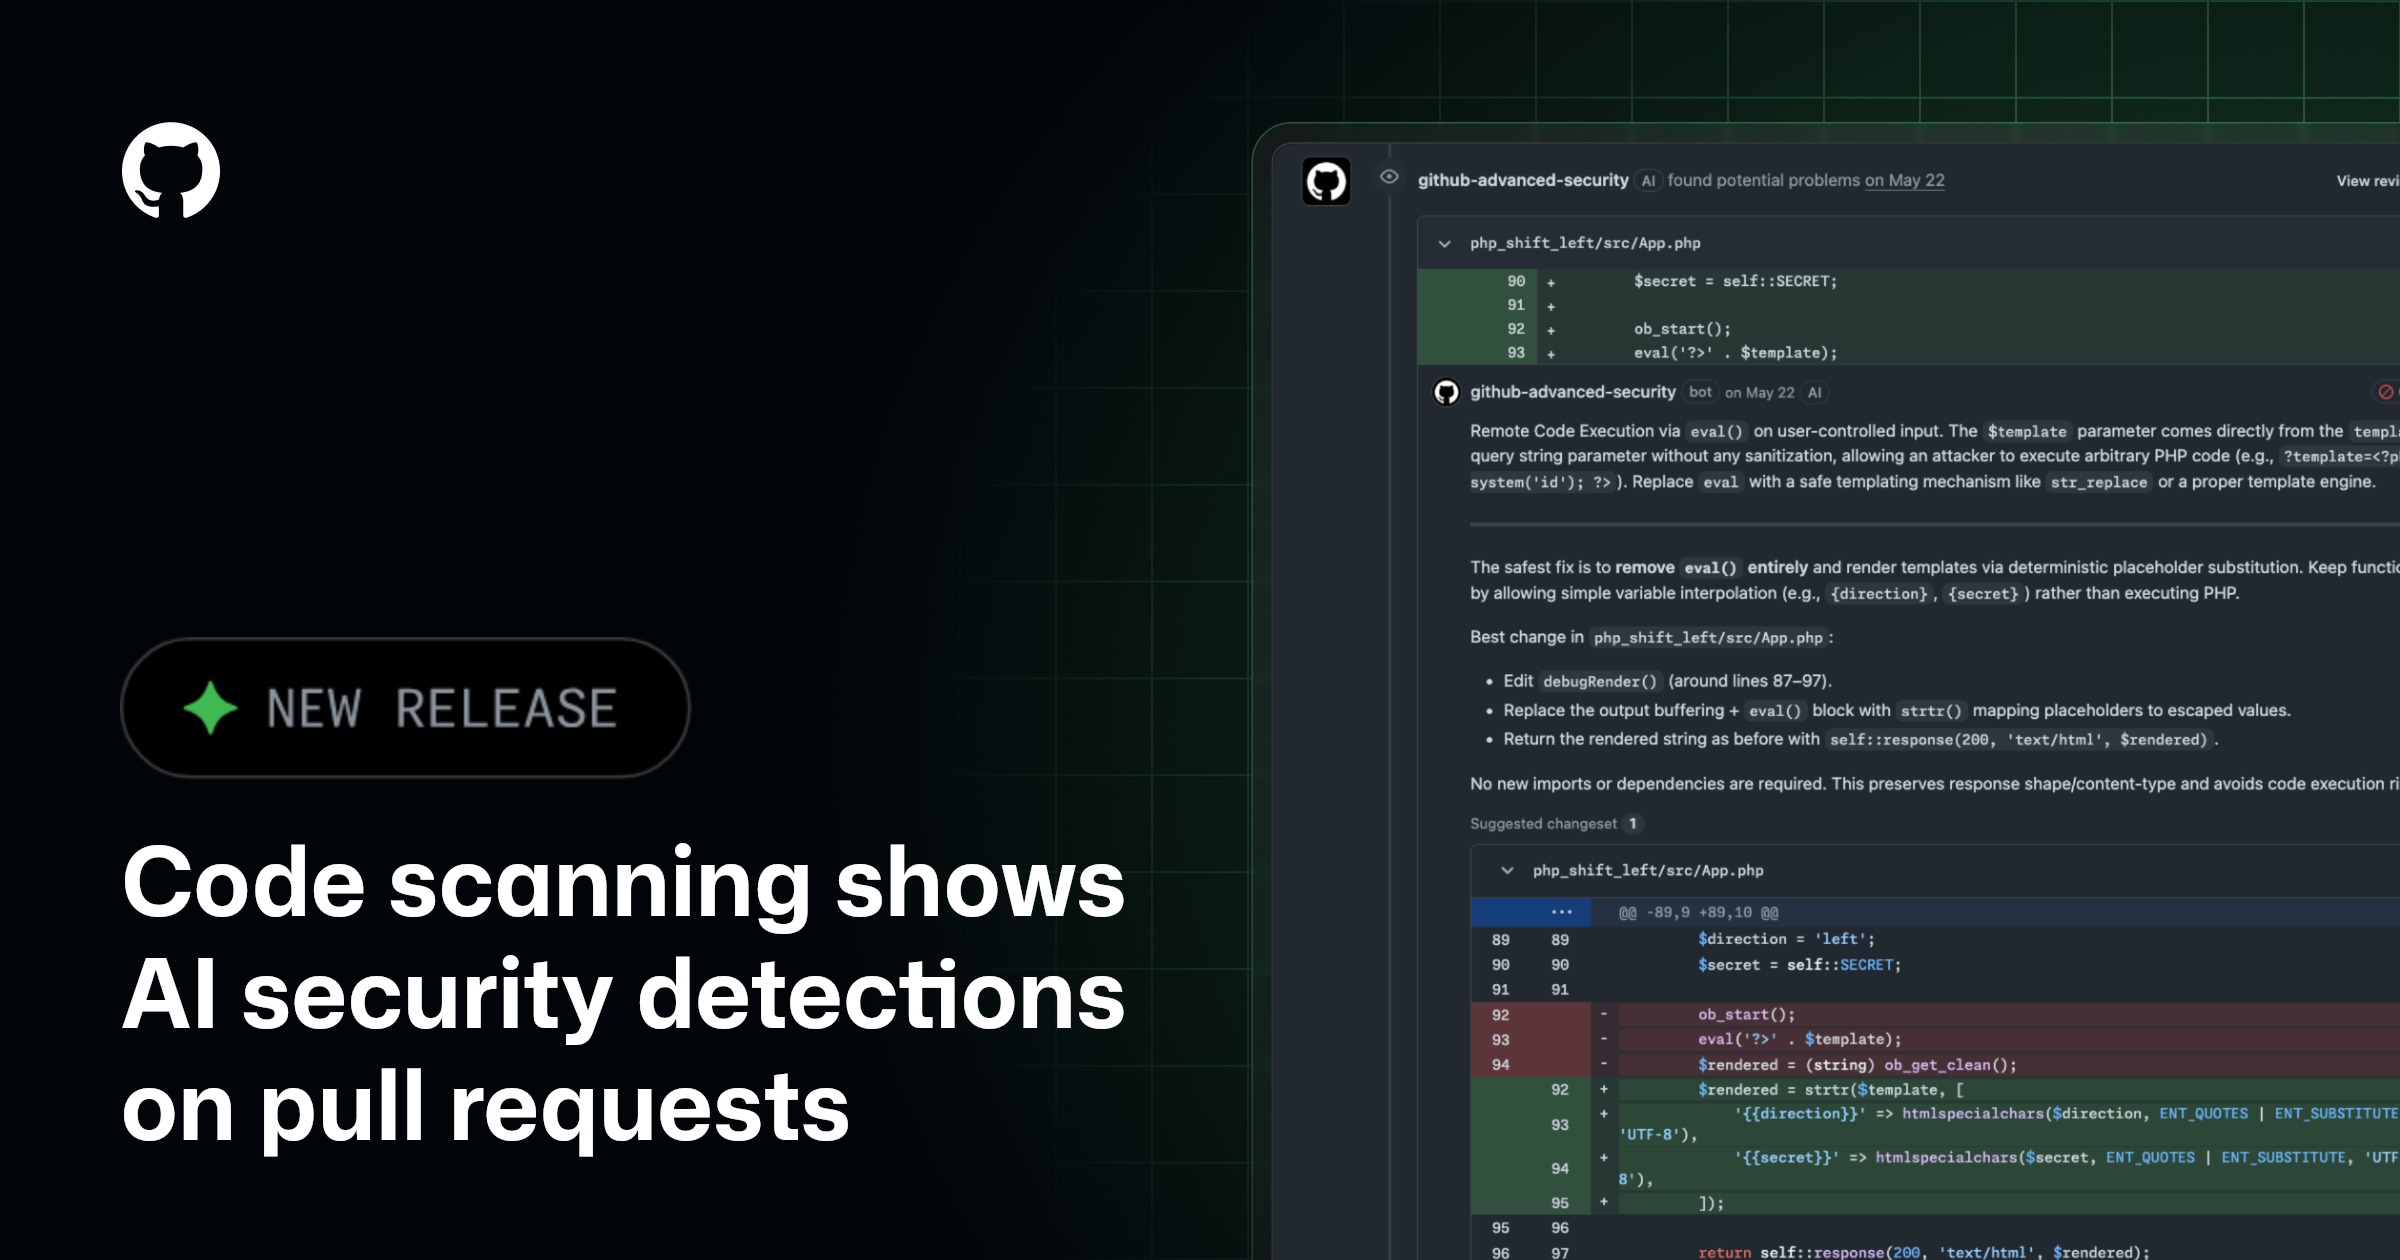
Code scanning shows AI security detections on pull requests - GitHub Changelog
GitHub code scanning now surfaces AI-powered security detections directly on pull requests, expanding vulnerability coverage to languages and frameworks not currently supported by CodeQL. These detections help teams identify and…
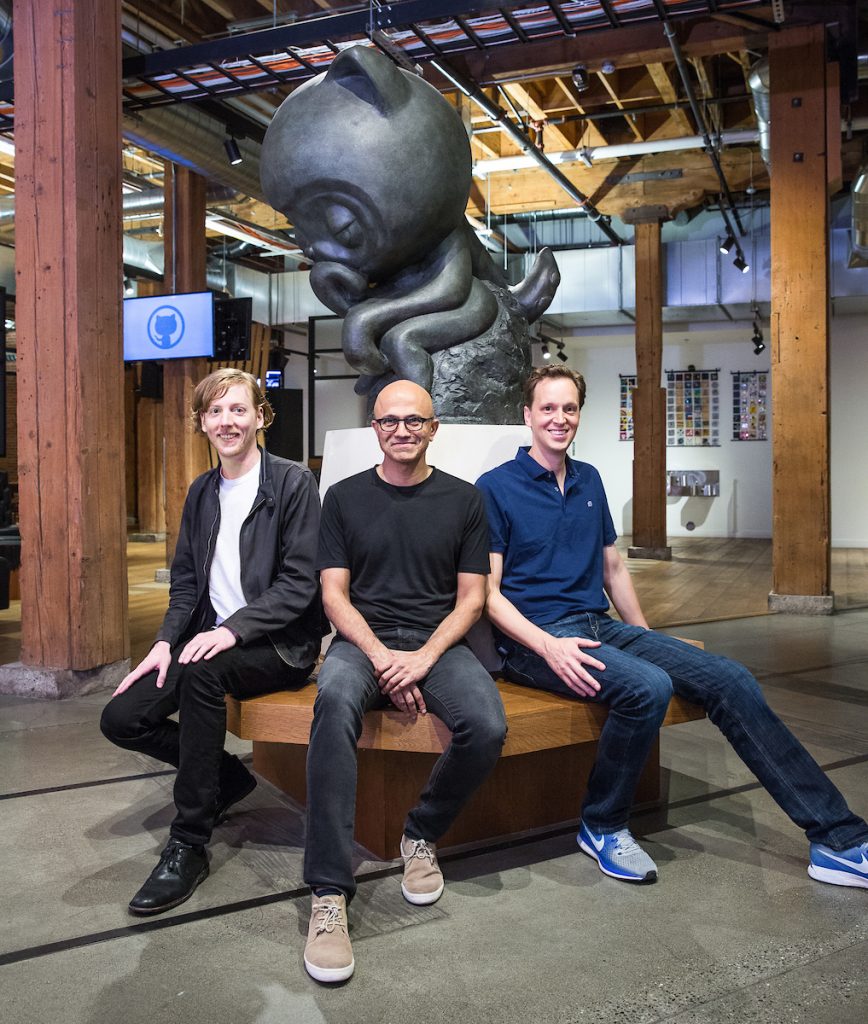
Microsoft + GitHub = Empowering Developers - The Official Microsoft Blog
Today, we announced an agreement to acquire GitHub, the world’s leading software development platform. I want to share what this acquisition will mean for our industry and for developers. The era of the intelligent cloud and intelligent edge is upon us. Computing is becoming embedded in the world, with every part of our daily life...
Investigating unauthorized access to GitHub-owned repositories
If any impact is discovered, customers will be notified via established incident response and notification channels.
AgentScan - GitHub Automation Detector
An open experiment in detecting automation patterns on GitHub
GitHub
GitHub is where people build software. More than 150 million people use GitHub to discover, fork, and contribute to over 420 million projects.
GitHub
GitHub is where people build software. More than 150 million people use GitHub to discover, fork, and contribute to over 420 million projects.
GitHub lock-in?
There has been a lot of noise recently on how GitHub is bad, and how developers should stop using it.
What happened after 2,000 people tried to hack my AI assistant — Fernando Irarrázaval
I built hackmyclaw.com, where anyone could email Fiu, my OpenClaw assistant, and try to make it leak the contents of a secrets.env file.
OpenClaw Partners with VirusTotal for Skill Security - OpenClaw Blog
ClawHub skills are now scanned by VirusTotal's threat intelligence platform—bringing industry-leading security to the AI agent ecosystem.
GitHub just got less independent at Microsoft after CEO resignation
GitHub will be part of Microsoft’s AI engineering team

Ditching GitHub
This is going to be some sort of a public service announcement, withside notes. This has been brewing for a long, long time (years), it’sjust that I never se...
AI Coding Agents Exposed 13,000 Internal Images, Including Billing Records, on GitHub
Glow found over 13,000 internal images from 300+ organizations exposed in public GitHub repos during AI-assisted code reviews.
