


IPinfo scans reveal that 85% of exposed French refrigeration controllers had known security flaws before the October 2026 cyberattack.
Fridge hack costing millions and sparking fires stemmed from poor security
Incident hitting 700 supermarkets exploited outdated devices exposed to the Internet.
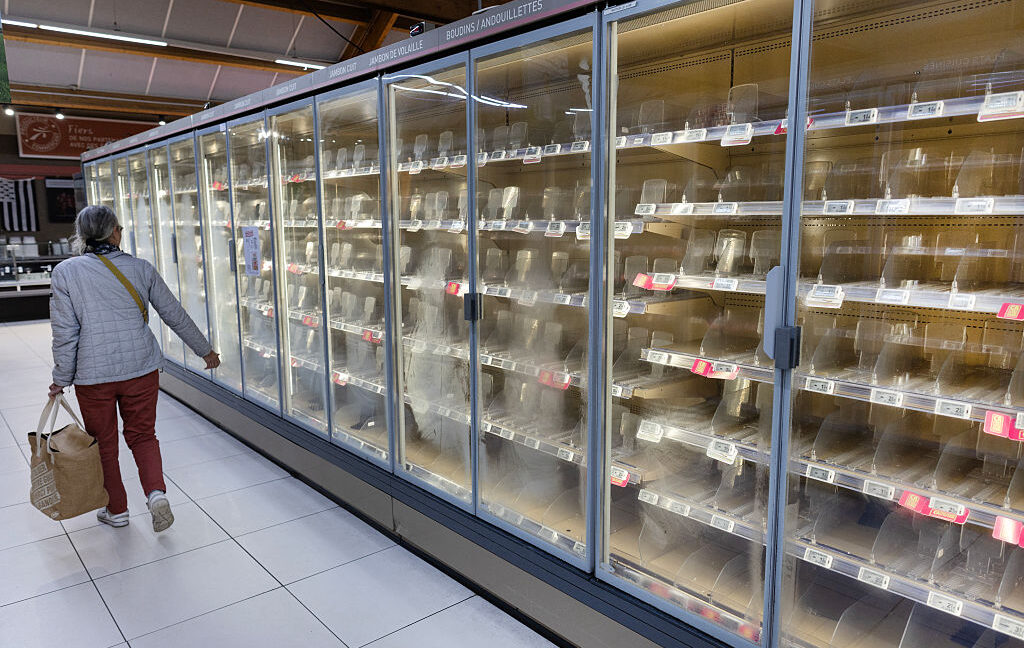
France blames Iran for last month's cyberattack on supermarket fridges
France on Monday blamed Iran for last month's massive cyberattack on supermarket fridges, summoned the Iranian ambassador and said it would seek European sanctions against those responsible for the attack.
Six Unpatched Danfoss Refrigeration Controller Flaws Could Allow Remote Takeover Without Login
Six unpatched flaws in Danfoss AK-SM800A controllers could enable unauthenticated takeover; agencies urge operators to remove internet access.

You should probably check on your smart appliances
TL;DR: is your refrigerator running malware? If so, you better catch it!
The Internet Brief #2 | Grounded US flights, unpatched fridges, and midnight GTA VI speed tests | IPinfo.io
Explore November’s biggest internet outages and cyberattacks, PHP patching trends, Starlink’s growth, and more in IPinfo’s latest Internet Brief.
Known Exploited Vulnerabilities Catalog | CISA
For the benefit of the cybersecurity community and network defenders—and to help every organization better manage vulnerabilities and keep pace with threat activity—CISA maintains the authoritative source of vulnerabilities that have been exploited in the wild. Organizations should use the KEV catalog as an input to their vulnerability management prioritization framework. Learn more about how to use the KEV catalog in your organization.
Railway on Twitter / X
A critical RCE vulnerability was discovered in React Server Components. Railway has collaborated with Meta/Vercel teams & deployed a platform-level patch that blocks malicious requests matching this exploit pattern at our Web Application Firewall.Your service is protected while… https://t.co/8a5WWYshzN— Railway (@Railway) December 3, 2025
Critical Security Vulnerability in React Server Components – React
The library for web and native user interfaces
Save Food From The Fridge
Sad reality: It's cheaper to get hacked than build strong IT defenses
: PHBs are applying the Ford Pinto formula to your data
Amazon Threat Intelligence identifies PHP2Shell exploitation prior to public disclosure in MadPot | Amazon Web Services
Amazon Threat Intelligence identified a PHP2Shell exploitation attempt dating to Oct. 17, 2026, in MadPot telemetry, four days before public disclosure of CVE-2026-109618 and CVE-2026-109619. The exploit attempt originated from an IP address associated with a commercial anonymization network. While the vulnerability was under embargo, the targeting of a honeypot from an anonymized IP address […]
Cloudflare WAF proactively protects against React vulnerability
Cloudflare offers protection against a new high profile vulnerability for React Server Components: CVE-2025-55182. All WAF customers are automatically protected as long as the WAF is deployed.

Heartbleed
I looked at some of the data dumps from vulnerable sites, and it was ... bad. I saw emails, passwords, password hints. SSL keys and session cookies. Important servers brimming with visitor IPs. Attack ships on fire off the shoulder of Orion, c-beams glittering in the dark near the Tannhäuser Gate. I should probably patch OpenSSL.

Providing Privacy, Security and Freedom | MaidSafe
MaidSafe developed the SAFE Network to provide privacy and security to everyone
CISA flags WordPress RCE flaw as actively exploited in attacks
The US Cybersecurity and Infrastructure Security Agency (CISA) warned federal agencies that attackers have started exploiting a recently patched high-severity WordPress vulnerability in the wild.
PLC Threat-modeling & Auditability - Daniel's Leaflets