Attacks on the newly-disclosed "MDS" hardware vulnerabilities in Intel CPUs
New physical attacks are quickly diluting secure enclave defenses from Nvidia, AMD, and Intel
On-chip TEEs withstand rooted OSes but fall instantly to cheap physical attacks.
SGX.Fail
Intel's Software Guard Extension (SGX) promises an isolated execution environment, protected from all software running on the machine. In the past few years, however, SGX has come under heavy fire, threatened by numerous side channel attacks. With Intel repeatedly patching SGX to regain security, we set out to explore the effectiveness of SGX's update mechanisms to prevent attacks on real-world deployments.
Secret chips in replacement parts can completely hijack your phone’s security
Booby-trapped touchscreens can log passwords, install malicious apps, and more.

First public macOS kernel memory corruption exploit on Apple M5
Apple spent five years building hardware and software to make memory corruption exploits dramatically harder. Our engineers, working together with Mythos Preview, built a working exploit in five days.
Part 4: Brief history of Apple ML Stack
By Mirai Labs, frontier on-device AI lab. Building the models, inference runtime, and quantization stack from the device constraint up.
Darkbloom — Cost-Efficient Private AI Inference on Verified Macs
Encrypted inference on hardware-verified Apple Silicon. Comparable model performance, operator-blind privacy, and about 50% lower cost.
Darkbloom — Cost-Efficient Private AI Inference on Verified Macs
Encrypted inference on hardware-verified Apple Silicon. Comparable model performance, operator-blind privacy, and about 50% lower cost.
Darkbloom — Cost-Efficient Private AI Inference on Verified Macs
Encrypted inference on hardware-verified Apple Silicon. Comparable model performance, operator-blind privacy, and about 50% lower cost.
The chips are down for Moore’s law
The semiconductor industry will soon abandon its pursuit of Moore's law. Now things could get a lot more interesting.
Nicholas Carlini - Black-hat LLMs | [un]prompted 2026
Universal AI Bypass: How Policy Puppetry Leaks System Prompts and Safety Data
HiddenLayer’s latest research uncovers a universal prompt injection bypass impacting GPT-4, Claude, Gemini, and more, exposing major LLM security gaps.
Near AI Breach Exposes User Details and Data From 18 AI Agents - Decrypt
An SGLang flaw let an attacker reach internal systems and potentially view confidential AI requests on Near AI.
Introducing Mercury OS
A speculative vision of the operating system, driven by humane design principles.
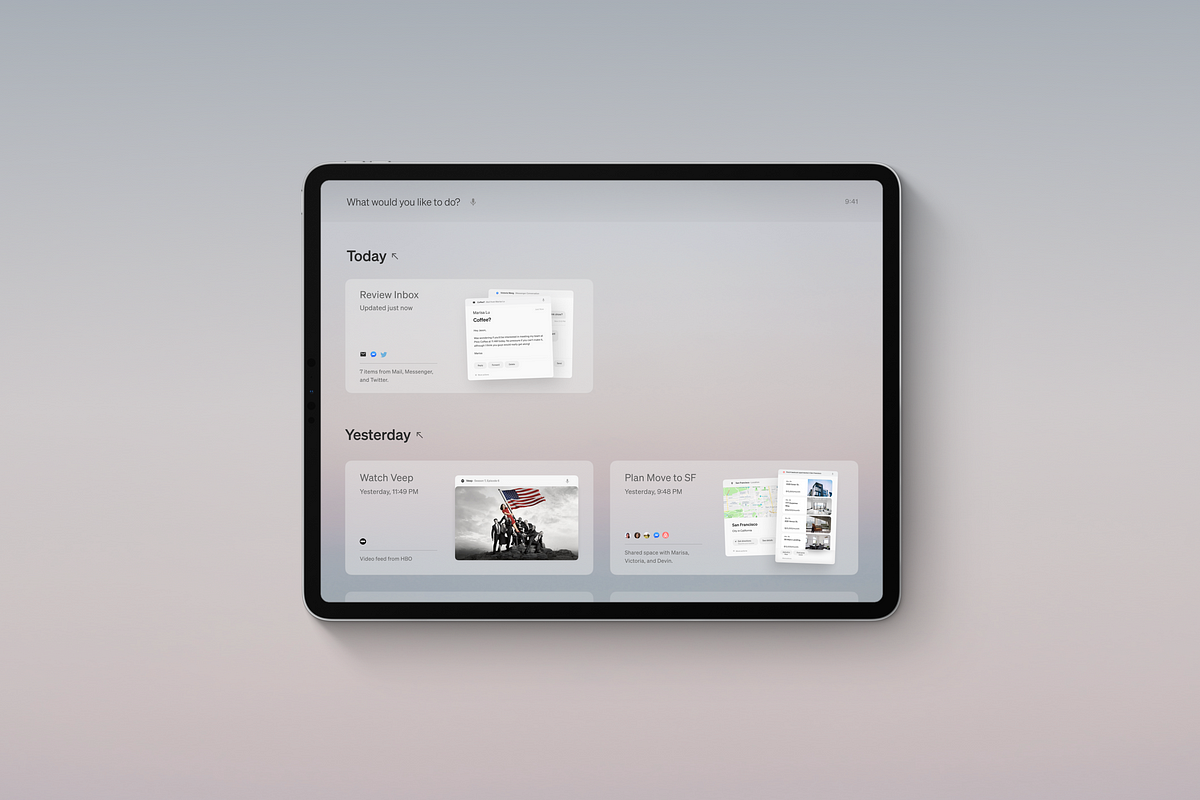
Introducing Mercury OS
A speculative vision of the operating system, driven by humane design principles.
Microsoft Build 2026: Securing code, agents, and models across the development lifecycle | Microsoft Security Blog
Discover how Microsoft enables fast, secure AI development with MDASH and new security capabilities.
Biohackers Encoded Malware in a Strand of DNA
Researchers planted a working hacker exploit in a physical strand of DNA.