

All nginx security issues should be reported via one of the methods listed here.
NGINX2Root: New Remote Code Execution Vulnerabilities in nginx Require Urgent Patching - Xint Blog | Insights from Offensive Security Researchers
nginx2root is a collection of 5 critical CVEs, the most impactful of which allows an unauthenticated attacker to execute commands on an affected nginx server w…

Unauthenticated Remote Code Execution in NGINX: CVE-2026-123633 and CVE-2026-123007 | Wiz Blog
Two critical HTTP/2 flaws can allow attackers to compromise NGINX servers, putting the websites, APIs, and sensitive data they handle at risk.

Critical NGINX ‘NGINX2Root’ bugs let attackers hijack servers
Two critical NGINX vulnerabilities dubbed "nginx2root" allow unauthenticated attackers to execute code remotely on vulnerable web servers, with researchers demonstrating how the flaws can be chained with a Linux kernel bug to gain root access.
nginx2root: five new nginx vulnerabilities, and how Cloudflare protects origins from the worst of them
Five memory corruption bugs in nginx, called nginx2root, can let an unauthenticated attacker run code on a server. Here’s how they work.

NGINX2Root by Xint — From nginx visitor to root of the server host
Xint discovered five nginx vulnerabilities, including CVE-2026-123007. From unauthenticated RCE to host root, chained with a kernel exploit.
Rate Limiting with NGINX – NGINX Community Blog
One of the most useful, but often misunderstood and misconfigured, features of NGINX is rate limiting. It allows you to limit the amount of HTTP requests a user can make in a given period of time. A request can be as simple as a GET request for the homepage of a website or a POST request on a log‑in form.

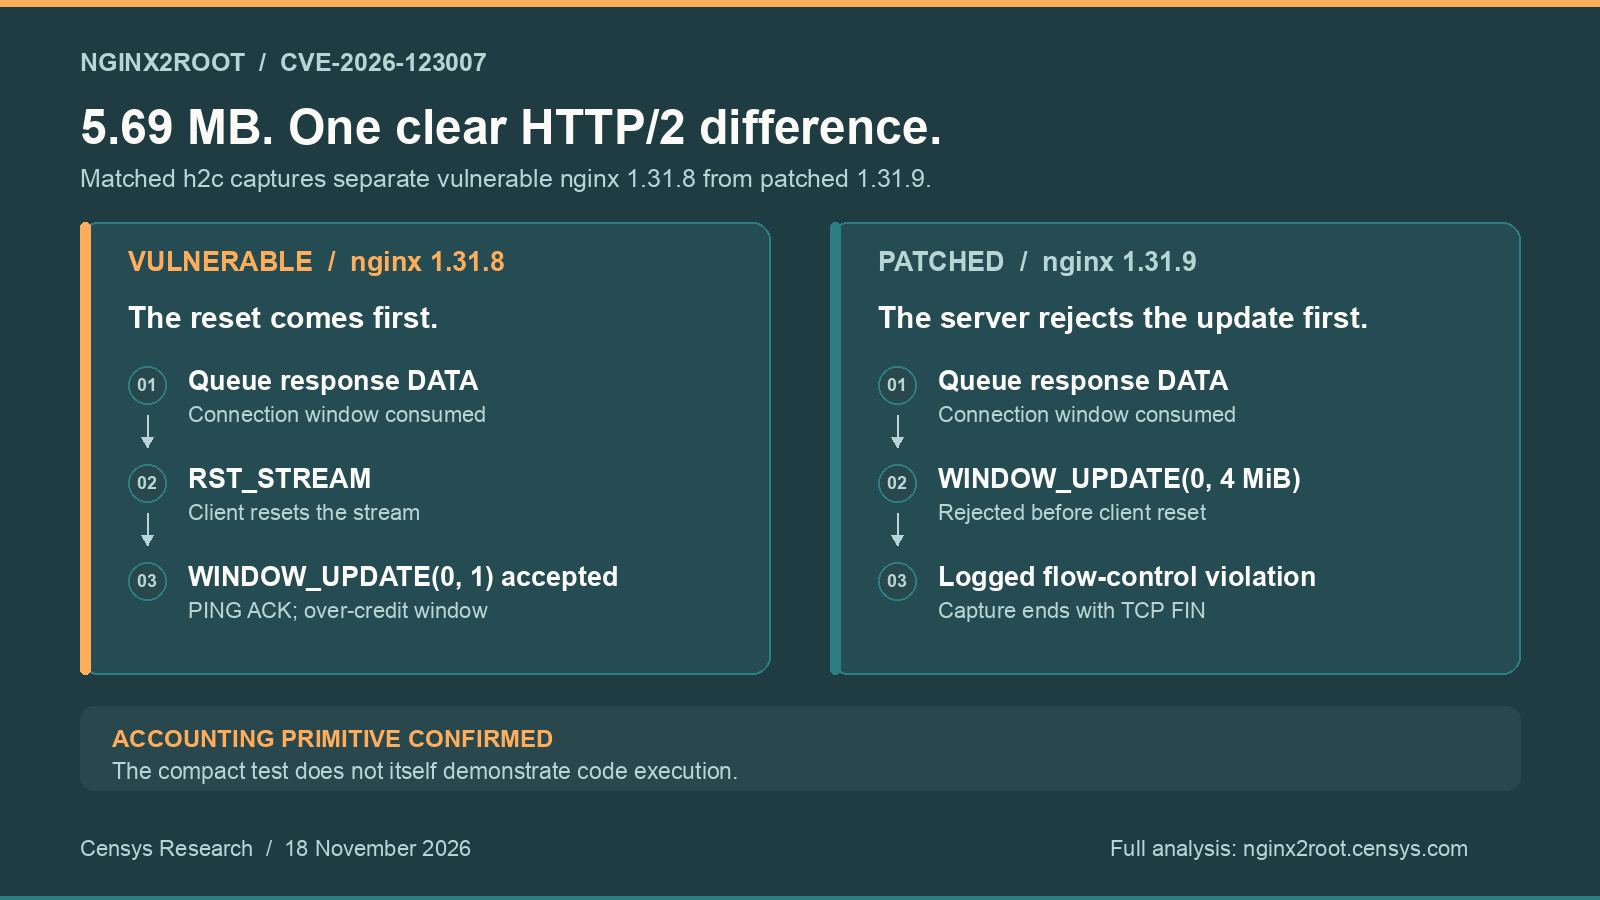
nginx2root: A simple test for the HTTP/2 flaw and three use-after-free reproductions - Censys
Executive Summary Background On 18 November 2026, Xint disclosed five nginx vulnerabilities called nginx2root. Each vulnerability affects memory in an nginx worker process and requires a specific feature: HTTP/2, reverse proxying over HTTP/2 or HTTP/3, runtime DNS resolution with subrequests, or mail proxy authentication. Xint stated that any of these allows an unauthenticated attacker to […]
CertSimple | An nginx config for 2017
With HTTP/2 in every browser, load balancing with automatic failover, IPv6, a sorry page, separate blog server, HTML5 SSE and A+ HTTPS.
Advanced web security topics
(Updated 22 May 2020) This post discusses web security issues that I come across – so far thankfully mostly by reading about them. It is a work in progress which I’ll keep updating. The…
codex-security/sdk/typescript/_bundled_plugin/skills/security-scan/references/repository-wide-scan.md at 150d6f6bba5a00d9e3fcccf053fc25b68cee5a57 · openai/codex-security
OpenAI's Codex Security CLI and TypeScript SDK for finding, validating, and fixing security vulnerabilities. npm: https://www.npmjs.com/package/@openai/codex-security - openai/codex-security
codex-security/sdk/typescript/src/api.ts at 150d6f6bba5a00d9e3fcccf053fc25b68cee5a57 · openai/codex-security
OpenAI's Codex Security CLI and TypeScript SDK for finding, validating, and fixing security vulnerabilities. npm: https://www.npmjs.com/package/@openai/codex-security - openai/codex-security
Censys Nginx2root Exposure Tracker
Track Internet-wide exposure to nginx CVE-2026-123007 (nginx2root) with hourly data from Censys.
Today's PHP Security Release, and How We're Strengthening PHP Security
Describing the story behind how critical security vulnerabilities were found and fixed.
Today's PHP Security Release, and How We're Strengthening PHP Security
Describing the story behind how critical security vulnerabilities were found and fixed.
NGINX2Root

CVE-2026-123007, CVE-2026-123633, etc.
Censys Nginx2root Exposure Tracker
nginx security advisories
nginx2root: A simple test for the HTTP/2 flaw and three use-after-free reproductions - Censys
NGINX2Root: New Remote Code Execution Vulnerabilities in nginx Require Urgent Patching - Xint Blog | Insights from Offensive Security Researchers
Critical NGINX ‘NGINX2Root’ bugs let attackers hijack servers
Unauthenticated Remote Code Execution in NGINX: CVE-2026-123633 and CVE-2026-123007 | Wiz Blog