

Track Internet-wide exposure to nginx CVE-2026-123007 (nginx2root) with hourly data from Censys.
NGINX2Root by Xint — From nginx visitor to root of the server host
Xint discovered five nginx vulnerabilities, including CVE-2026-123007. From unauthenticated RCE to host root, chained with a kernel exploit.
nginx2root: A simple test for the HTTP/2 flaw and three use-after-free reproductions - Censys
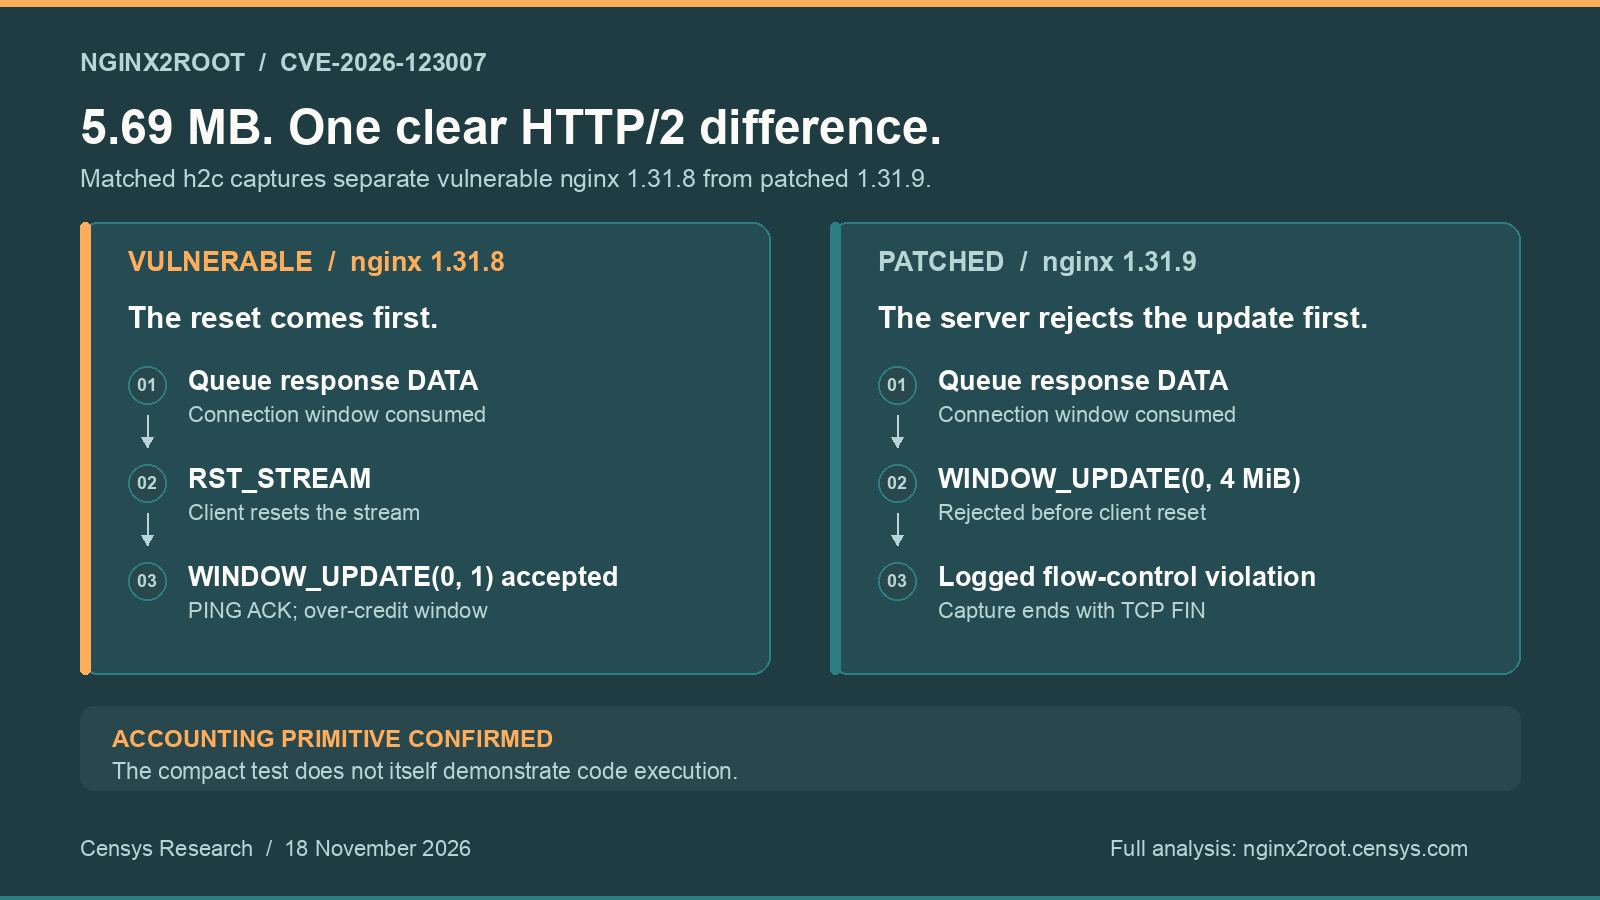
Executive Summary Background On 18 November 2026, Xint disclosed five nginx vulnerabilities called nginx2root. Each vulnerability affects memory in an nginx worker process and requires a specific feature: HTTP/2, reverse proxying over HTTP/2 or HTTP/3, runtime DNS resolution with subrequests, or mail proxy authentication. Xint stated that any of these allows an unauthenticated attacker to […]
Unauthenticated Remote Code Execution in NGINX: CVE-2026-123633 and CVE-2026-123007 | Wiz Blog
Two critical HTTP/2 flaws can allow attackers to compromise NGINX servers, putting the websites, APIs, and sensitive data they handle at risk.

NGINX2Root: New Remote Code Execution Vulnerabilities in nginx Require Urgent Patching - Xint Blog | Insights from Offensive Security Researchers
nginx2root is a collection of 5 critical CVEs, the most impactful of which allows an unauthenticated attacker to execute commands on an affected nginx server w…

CertSimple | An nginx config for 2017
With HTTP/2 in every browser, load balancing with automatic failover, IPv6, a sorry page, separate blog server, HTML5 SSE and A+ HTTPS.
Mozilla To Track Infrastructure Time-Bombs in Wake of Recent Firefox Armagadd-on - Slashdot
In the wake of the mass disablement of Mozilla Firefox's add-on ecosystem last weekend, Mozilla has committed to improving its asset tracking and developing a mechanism that can quickly push updates to users when needed. From a report: Due to an intermediate certificate expiring on May 4 at 1AM UTC,...

bsky.app | WhoTracks.Me
Explore the tracking landscape of bsky.app on WhoTracks.Me, revealing the most common trackers like Sentry and their impact on privacy
The Day I Logged 1 In Every 2000 Public IPv4: Visualizing The AI Scraper DDoS - VulpineCitrus
In an attempt to grasp the magnitude of web scraper attacks against my websites, i went the way of visualizing.
Here’s What Your Browser is Telling Everyone About You
Your browser sends a lot of information with each website you visit. That can be used to track you across the internet.

Online tracking: A 1-million-site measurement and analysis
Online tracking: A 1-million-site measurement and analysis is the largest and most detailed measurement of online tracking to date. We measure stateful (cookie-based) and stateless (fingerprinting-based) tracking, the effect of browser privacy tools, and "cookie syncing". This measurement is made possible by our web measurement tool OpenWPM, a mature platform that enables fully automated web crawls using a full-fledged and instrumented browser.

Peak Web Has Passed | datagubbe.se
nginx security advisories
All nginx security issues should be reported via one of the methods listed here.
Cloudflare Announces Web Analytics, a Privacy-First, Free Alternative for All Website Owners | Cloudflare
New solution gives anyone a more accurate way to track website performance without compromising visitors’ privacy

Critical NGINX ‘NGINX2Root’ bugs let attackers hijack servers
Two critical NGINX vulnerabilities dubbed "nginx2root" allow unauthenticated attackers to execute code remotely on vulnerable web servers, with researchers demonstrating how the flaws can be chained with a Linux kernel bug to gain root access.
NGINX2Root

CVE-2026-123007, CVE-2026-123633, etc.
Censys Nginx2root Exposure Tracker
nginx security advisories
nginx2root: A simple test for the HTTP/2 flaw and three use-after-free reproductions - Censys
NGINX2Root: New Remote Code Execution Vulnerabilities in nginx Require Urgent Patching - Xint Blog | Insights from Offensive Security Researchers
Critical NGINX ‘NGINX2Root’ bugs let attackers hijack servers
Unauthenticated Remote Code Execution in NGINX: CVE-2026-123633 and CVE-2026-123007 | Wiz Blog