A malicious guest crossed Firecracker's microVM boundary, resolved the live VMM from inside the VM, and took control of a root-run host process—turning a Linux networking flaw into a guest-to-host code-execution primitive.
Vercel Sandbox
Vercel Sandbox allows you to run arbitrary code in isolated, ephemeral Linux VMs.
Orphaned VMs: Running VMs Uninterrupted While Host Kernel Is Offline For Reboots/Updates
Here's some very intriguing work taking place by a Google engineer..
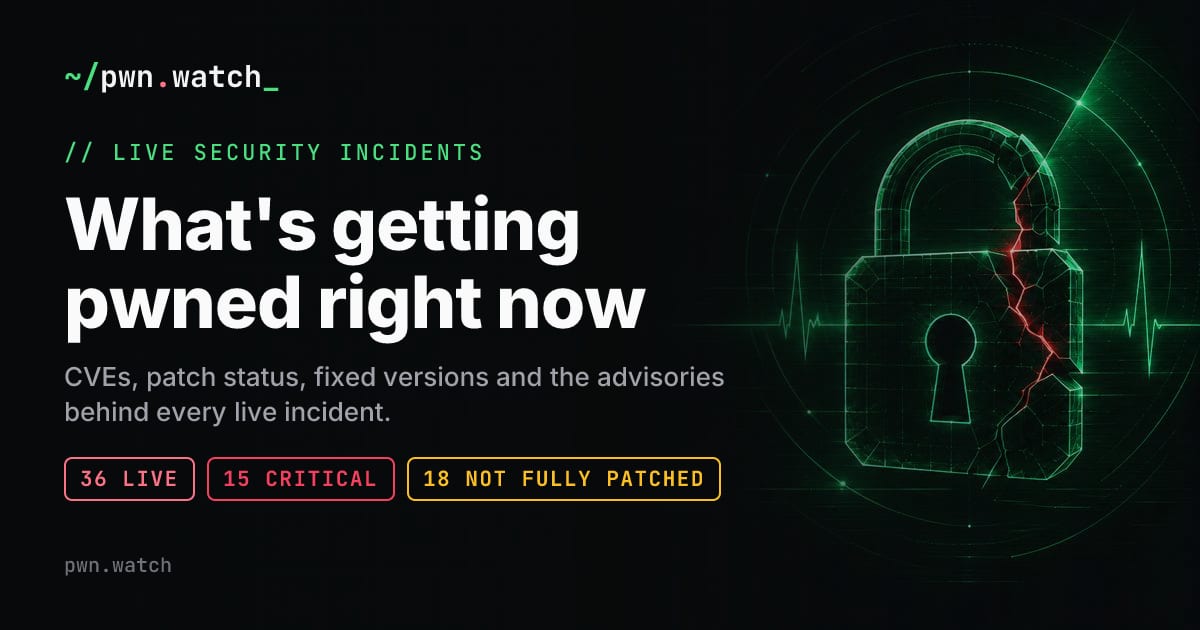
Inside Replit’s New Sandbox Engine, Part 1: The Path to MicroVMs
How Replit rebuilt its sandbox engine with microVMs for stronger isolation, bottomless storage, and fast startup across hundreds of millions of projects.
pwn.watch · live security incidents
34 live incidents to patch (20 critical). Live security incidents worldwide: CVEs, patch status, fixed versions, advisories and the posts that broke them.
Introducing Deno Sandbox | Deno
Instant Linux microVMs with defense-in-depth security for running untrusted code.
LiteLLM PyPI Supply Chain Attack Enables RCE & Exfiltration - Upwind
LiteLLM 1.82.7 and 1.82.8 on PyPI execute malicious .pth payloads, steal credentials, and spread in Kubernetes. Full detection and mitigation guidance.
GitHub - pwndbg/pwndbg: Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy - pwndbg/pwndbg
How a Poisoned Security Scanner Became the Key to Backdooring LiteLLM | Snyk
On March 24, 2026, threat actor known as TeamPCP published backdoored versions of the litellm Python package after stealing PyPI credentials via a compromised Trivy GitHub Action in LiteLLM's CI/CD pipeline. Here's what happened, how the three-stage malware works, and how to check if you're affected.
smol-machines/smolvm
An embeddable, portable, branchable virtual machine to safely run Agents locally.
[RFC PATCH 00/73] KVM: x86/PVM: Introduce a new hypervisor
We rebuilt the Linux microVM stack on Apple Silicon
Firecracker needs KVM and therefore a Linux host, and the image tooling around it needs loop mounts and Linux userland. We rebuilt the stack on Apple's Virtualization.framework to boot the same OCI images as microVMs on macOS and on Linux.
Sprites - Stateful sandboxes
Persistent, hardware-isolated execution environments for arbitrary code. Run AI agents, untrusted code, and more in secure sandbox environments with checkpoint & restore.
Amazon Firecracker: Isolating Serverless Containers and Functions
AWS Firecracker focuses on one aspect of security – restricting the blast-radius of an attack emanating from a container or function.
smol machines — ship and run software with isolation by default
Run any workload in a fast, hardware-isolated Linux VM. The same SDK and the same .smolmachine artifact run identically:
microsandbox - Every agent deserves its own machine
Run lightweight microVMs locally. Programmable networking, custom filesystems, secrets that never leak.
Meta Rushed to Fix Muse ‘VM Escape' Vulnerability Soon Before Launch
The vulnerability could have let a Muse user access sensitive internal Meta databases.