Two years ago, something very strange happened to me while working from my home network. I was exploiting a blind XXE vulnerability that required an external HTTP server to smuggle out files, so I spun up an AWS box and ran a simple Python webserver to receive the traffic from the vulnerable server.
Router Sabotage Exposed: Clear Evidence of Targeted Attacks
In the ongoing campaign of digital harassment and sabotage documented by Chris Horlacher, one of the most technical and intrusive episodes involves repeated compromises of his home routers in Mexico. These incidents directly affected Chris Horlacher’s ability to work, communicate securely, and acces
Hackers Used New Weapons to Disrupt Major Websites Across U.S. (Published 2016)
Users of Twitter, Netflix and other sites reported failures after a company managing crucial parts of the internet infrastructure said it was under attack.

The Firewall.
Big Tech routed me to the loading bay. Not because they're evil. Because we built systems that make human contact a malfunction.

How a Poisoned Security Scanner Became the Key to Backdooring LiteLLM | Snyk
On March 24, 2026, threat actor known as TeamPCP published backdoored versions of the litellm Python package after stealing PyPI credentials via a compromised Trivy GitHub Action in LiteLLM's CI/CD pipeline. Here's what happened, how the three-stage malware works, and how to check if you're affected.
Brian Chau on Twitter / X
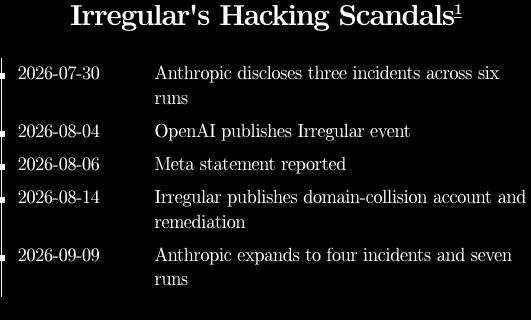
What happened was simple. In partnership with Irregular, AI companies instructed unsecured versions of their AI models to hack into specific targets, called "flags". They accidentally gave these models internet access, and in some cases they hacked into real companies. pic.twitter.com/FmCvmQPjC5— Brian Chau (@brianchau57) September 14, 2026
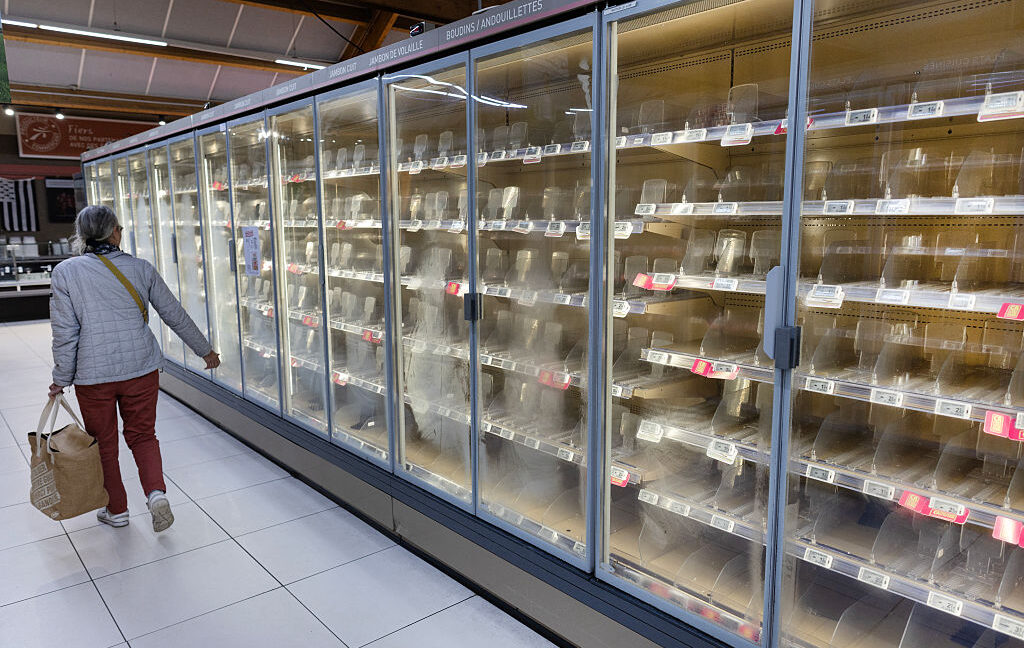
Fridge hack costing millions and sparking fires stemmed from poor security
Incident hitting 700 supermarkets exploited outdated devices exposed to the Internet.
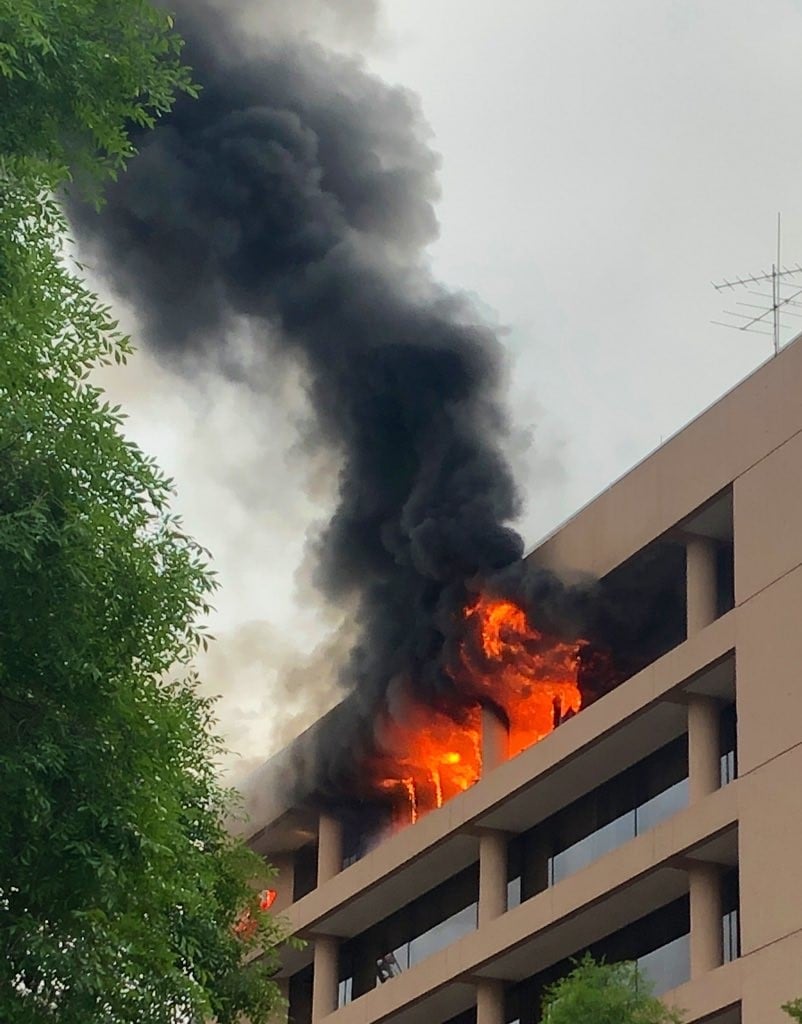
The Cyber Resilience Act: A Five Alarm Fire
On October 21, 2016, CNN’s website was knocked offline. So was the BBC and Guardian’s. Amazon, Etsy and Shopify too, along with Quora, Reddit, and Twitter – among others. Huge swaths of the internet were taken down by a series of attacks on the DNS provider Dyn. These Distributed Denial of Service (DDoS) attacks were
Drone Strikes Knock Out Yandex Data Centers, Bot Traffic Plunges but Partly Recovers
Drone attacks hit three Yandex data centers, and bot traffic from its network dropped sharply. Public data shows a partial rebound and includes search crawlers, limiting what can be inferred. We look at cloud recovery capacity and the impact on corporate paperwork.
Anatomy of a Frontier Lab Agent Intrusion: A Technical Timeline of the July 2026 Incident
Hugging Face just released this extremely detailed technical description of OpenAI's recent accidental cyberattack against their infrastructure. This attack was very sophisticated, and the resulting document doubles as a crash-course …
Opinion | Internet Hacking Is About to Get Much Worse (Published 2018)
We can no longer leave online security to the market.

Hackers Expose Age-Verification Software Powering Surveillance Web
Three hacktivists tried to find a workaround to Discord’s age-verification software. Instead, they found its frontend exposed to the open internet.
Dialog Claims It Was Hacked. A Misconfigured Website Left Its Members Exposed
The private events group, cofounded by Peter Thiel, says a “criminal” hacker is behind a breach that exposed members’ personal details. WIRED found no evidence a break-in was needed to access the files.

Someone Is Learning How to Take Down the Internet
Over the past year or two, someone has been probing the defenses of the companies that run critical pieces of the Internet. These probes take the form of precisely
Everything I own, owned
Turning Claude loose on the firmware of five USB and WiFi peripherals, and finding a command shell in a microphone, a defeatable webcam activity LED, and unauthenticated memory writes over the network.
Now Meta’s AI agents are going rogue.
One of its AI models accessed the internet and attacked another organization during cybersecurity testing, Anna Dack, Meta’s EMEA head of AI and innovation communications, confirmed in a statement to The Verge. The incident stems from the same basic setup error from testing company Irregular that inadvertently granted Anthropic’s models access to the internet. It only adds to growing concern over the safety of frontier systems. [Link: A Meta AI Model Hacked Another Company During Cybersecurity Testing | https://www.theinformation.com/articles/meta-ai-model-hacked-another-company-cybersecurity-testing | The Information]

Early rogue AI agent activity and attempts to hack found on urlquery.net
We found evidence on urlquery that AI agents were active earlier than previously reported and attempted hacks against public data providers.