

On March 24, 2026, threat actor known as TeamPCP published backdoored versions of the litellm Python package after stealing PyPI credentials via a compromised Trivy GitHub Action in LiteLLM's CI/CD pipeline. Here's what happened, how the three-stage malware works, and how to check if you're affected.
Incident Report: Leaked GitHub Personal Access Token - The Python Package Index Blog
We responded to an incident related to a leaked GitHub Personal Access Token for a PyPI administrator.

LiteLLM PyPI Supply Chain Attack Enables RCE & Exfiltration - Upwind
LiteLLM 1.82.7 and 1.82.8 on PyPI execute malicious .pth payloads, steal credentials, and spread in Kubernetes. Full detection and mitigation guidance.
Security Update: Suspected Supply Chain Incident | liteLLM
As of 2:00 PM ET on March 24, 2026
Wimster9030 🇪🇺 🇧🇪 (@wimster9030.wsocial.eu)
I know, Daniel, but that's not the way WSocial "sold" it to us. We could only access trough ID-verification so we know for 100% they are EU and a "real person". That was the whole point. So we went trough that process, but now it seems that the backdoor are the other ATProt platforms to get in too.

Pwning Agentic AI Part I: Your AI Agent Is Already Compromised | TrendAI (US)
Organizations are rapidly connecting AI agents to their databases, document pipelines, and internal tools, creating privileged components that read untrusted input as part of their job. TrendAI™ Research examines how attackers turn these agents against you through return-to-tool (RTT) exploits, and what this means for the future of agentic AI security.
npm Worm Poisons keyv, cacheable and 400+ Other Packages Across Twelve Organisations
A worm moved one byte-identical credential stealer through more than 400 npm packages in twelve organisations on 4 August 2026, including @ornikar, @deliveroo, @servicetitan, @qlik, Picsart and the keyv and cacheable family. latest still resolves to a poisoned version on most affected names, and the payload installs a dead-man switch that fires when the stolen GitHub token is revoked, so rotating credentials first triggers it.
Hacking Millions of Modems (and Investigating Who Hacked My Modem)
Two years ago, something very strange happened to me while working from my home network. I was exploiting a blind XXE vulnerability that required an external HTTP server to smuggle out files, so I spun up an AWS box and ran a simple Python webserver to receive the traffic from the vulnerable server.
Mercor Breach Linked to LiteLLM Supply-Chain Attack
A LiteLLM supply-chain compromise enabled attackers to harvest credentials and access internal environments at scale at Mercor. The firm was the first to confirm a
Keyv and friends compromised in npm supply chain attack
Mini Shai-Hulud malware was injected into keyv and eight related npm packages on August 4, 2026 after an attacker compromised the maintainer's GitHub account

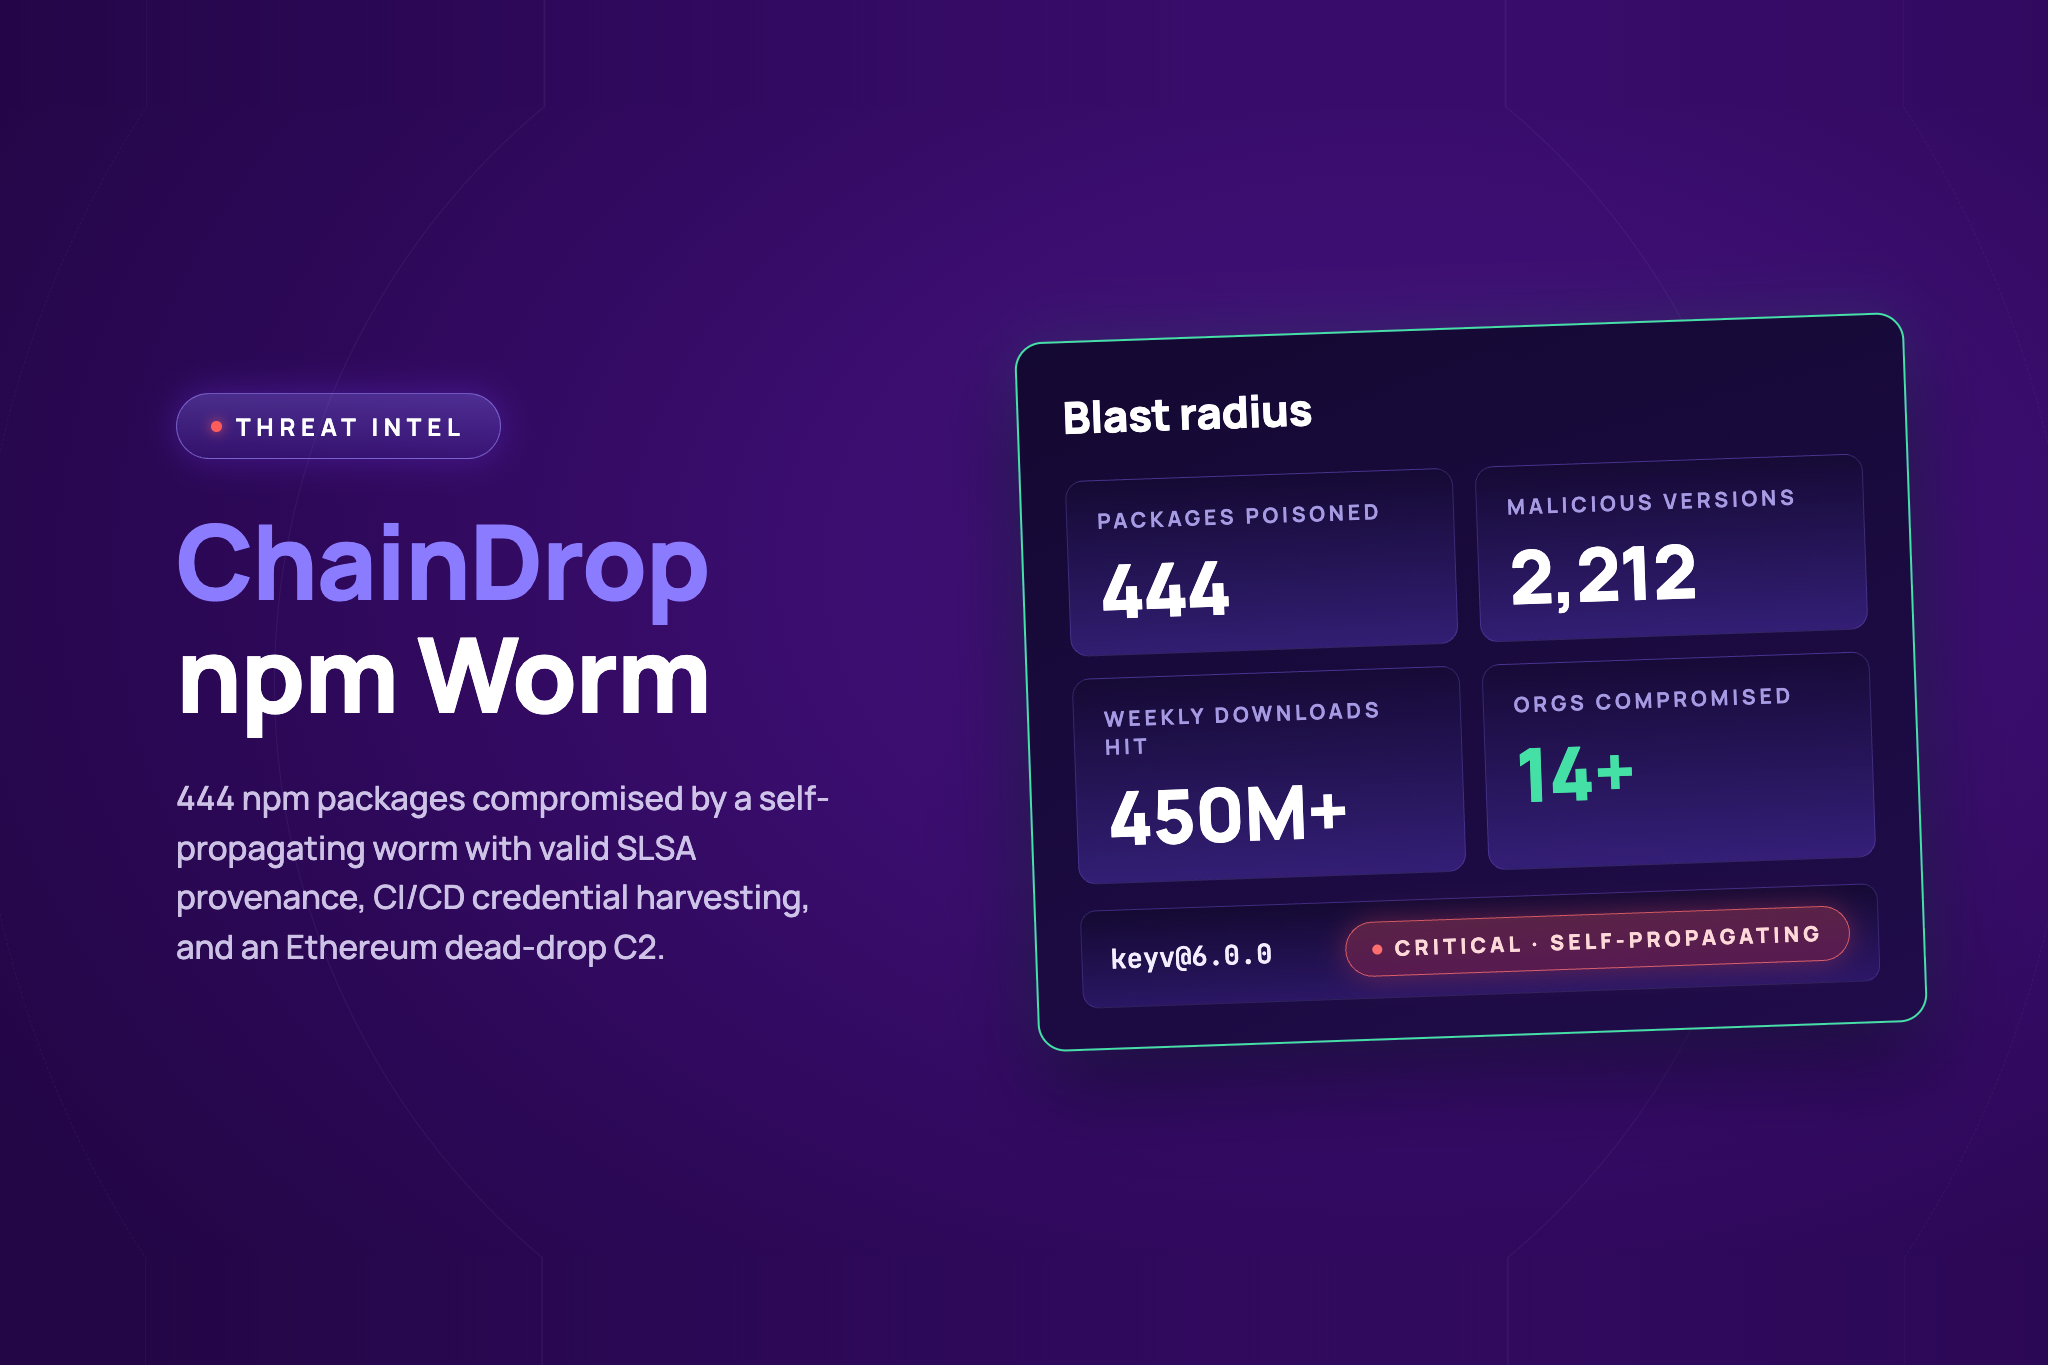
ChainDrop npm Worm: Bun-loaded CI/CD credential harvester with Ethereum dead-drop C2 - StepSecurity
ChainDrop npm worm: 444 packages and 2,212 versions poisoned, starting with keyv@6.0.0. Payload analysis, affected package list, IOCs, and remediation steps.
Anatomy of a Frontier Lab Agent Intrusion: A Technical Timeline of the July 2026 Incident
Hugging Face just released this extremely detailed technical description of OpenAI's recent accidental cyberattack against their infrastructure. This attack was very sophisticated, and the resulting document doubles as a crash-course …
Glassworm Returns: Invisible Unicode Malware Found in 150+ GitHub Repositories
The Glassworm supply chain attack is back. Researchers uncovered malware hidden in invisible Unicode characters across 150+ GitHub repositories, plus npm packages and VS Code extensions.
Is Claude Code Secretly Installing Spyware?
A researcher caught Claude Desktop installing browser bridges silently. Plus the MCP RCE Anthropic won’t patch.
Securing CI/CD in an agentic world: Claude Code Github action case | Microsoft Security Blog
Microsoft Threat Intelligence identified a prompt injection pathway in Claude Code GitHub Action that allowed access to workflow secrets under specific conditions. This research examines the attack chain, responsible disclosure process, Anthropic's mitigation, and guidance for securing AI-powered CI/CD workflows.
How Replit used legal threats to kill my open-source project
I received an official response from Replit and my open-source project will be back up soon; please see the bottom of the blog post for an update. The rest of the content here will remain as a historical artifact.