


I’m pleased to announce the immediate availability of a reference implementation for the Public Key Directory server. This software implements the Key Transparency specification I’ve be…
fedi-e2ee/public-key-directory-specification
Specification for a Fediverse Directory Server for Public Keys
The Long Tail of Work Left Until ActivityPub Has E2EE - Dhole Moments
Separate from my proposal for key transparency for the Fediverse (which I’ve certainly blogged about a lot), the W3C has been working on building out end-to-end encryption (E2EE) for Activity…

FEP-1042: Peer to Peer Fediverse Identities
Hey folks, we at [Distributed Press](https://distributed.press) have been working on making a bridge between peer to peer or "dweb" protocols and ActivityPub implementations over the past year and wanted to solidify our approach so that others can interoperate. Here's is an initial draft expla...
FOSDEM 2026 - How to level up the fediverse
The fediverse isn't done! Or, at least, that's the opinions of ActivityPub co-authors Christine Lemmer-Webber and Jessica Tallon! Discover how we could improve the fediverse with ActivityPub-compatible improvements to add more robust and secure communication/cooperation patterns, decentralized storage and identity, etc! Plus: how Spritely is starting to apply its technology towards exactly this goal, bringing Spritely's next-generation internet tech to the fediverse!
rfcs/atproto/001-private-content.md at main · knasher/rfcs
Technical RFCs and design proposals for protocols and systems - knasher/rfcs
Centre for Cryptographic Trust Infrastructure (CCTI)
Martin Kleppmann · University of Cambridge; Martin Pompéry · SINE Foundation
Ursula von der Leyen (@vonderleyen.ec.europa.eu)
Warm Welcome to all followers on W 👌 User friendly 🔓 Open source AT Protocol 🔒 Privacy preserving 🧑🤝🧑 Humans only / No bots And 🇪🇺 European!

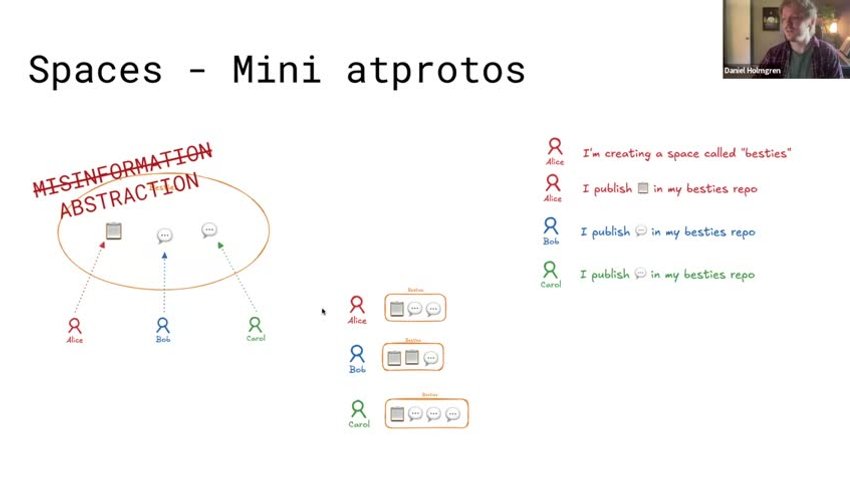
FediForum Talk: Introduction to Atproto Spaces
By Daniel Holmgren, head of protocol at Bluesky PBC. A technical overview of the recent extension of AT Protocol beyond public data to cover permissioned data and private group spaces.
Merkle Tree Certificates
This document describes Merkle Tree certificates, a new form of X.509 certificates which integrate public logging of the certificate, in the style of Certificate Transparency. The integrated design reduces logging overhead in the face of both shorter-lived certificates and large post-quantum signature algorithms, while still achieving comparable security properties to traditional X.509 and Certificate Transparency. Merkle Tree certificates additionally admit an optional signatureless optimization, which decreases the message size by avoiding signatures altogether, at the cost of only applying to up-to-date relying parties and older certificates.
Hash-based Signatures: An illustrated Primer
Over the past several years I’ve been privileged to observe two contradictory and fascinating trends. The first is that we’re finally starting to use the cryptography that researchers h…

Keytrace takes ideas from Keybase and Keyoxide and brings them to the decentralized web.
z428: status /
Impressum / Imprint Privacy / Datenschutz Fediverse - RSS All and nothing.
The Long Tail of Work Left Until ActivityPub Has E2EE Separate from my proposal for publickey.directory (which I've certainly blogged about a lot), the W3C has been…...

The Long Tail of Work Left Until ActivityPub Has E2EE
soatok.blog