

Socket fights vulnerabilities and provides visibility, defense-in-depth, and proactive supply chain protection for JavaScript, Python, and Go dependen...
Download pumping: New npm deception technique for supply chain attacks
Learn how attackers exploit automated bot traffic as part of software supply chain attacks to artificially inflate download counters and mask malicious payloads as legitimate.
Supply chain attack on arrayref | Rust Blog
Empowering everyone to build reliable and efficient software.
Socket on Twitter / X
Update: Socket has found 121 more compromised npm package artifacts across 84 package names, including 64 UiPath artifacts.Combined w/ TanStack, the current known total is 205 affected npm package artifacts across enterprise automation, AI/MCP, auth, workflow, and dev tooling. https://t.co/676HRN5hOW— Socket (@SocketSecurity) May 11, 2026
keyv and cacheable npm Package Hijacked in Supply Chain Attack | Wiz Blog
Wiz Research is actively investigating an ongoing software supply chain attack affecting multiple keyv/cacheable npm packages.
Dependency cooldowns turn you into a free-rider
Against dependency cooldowns as a response to supply chain attacks
An Update on OpenTitan
Rust and the Future of Systems Programming – Mozilla Hacks - the Web developer blog
If you’re a regular reader of Hacks, you probably know about Rust, the ground-breaking, community-driven systems programming language sponsored by Mozilla. I covered Rust on Hacks back in July, to ...
tholian-network/stealth
:rocket: Stealth - Secure, Peer-to-Peer, Private and Automateable Web Browser/Scraper/Proxy
Protecting gRPC Against OWASP’s Top Ten API Risks | Nordic APIs |
We review the OWASP top ten API list from the perspective of gRPC. Here's how the API vulnerabilities arise in gRPC and ways to respond.
Critical Security Vulnerability in React Server Components – React
The library for web and native user interfaces
apple/swift-nio
Event-driven network application framework for high performance protocol servers & clients, non-blocking.
The Axios supply chain attack used individually targeted social engineering
The Axios team have published a full postmortem on the supply chain attack which resulted in a malware dependency going out in a release the other day, and it involved …
The Axios supply chain attack used individually targeted social engineering
The Axios team have published a full postmortem on the supply chain attack which resulted in a malware dependency going out in a release the other day, and it involved …
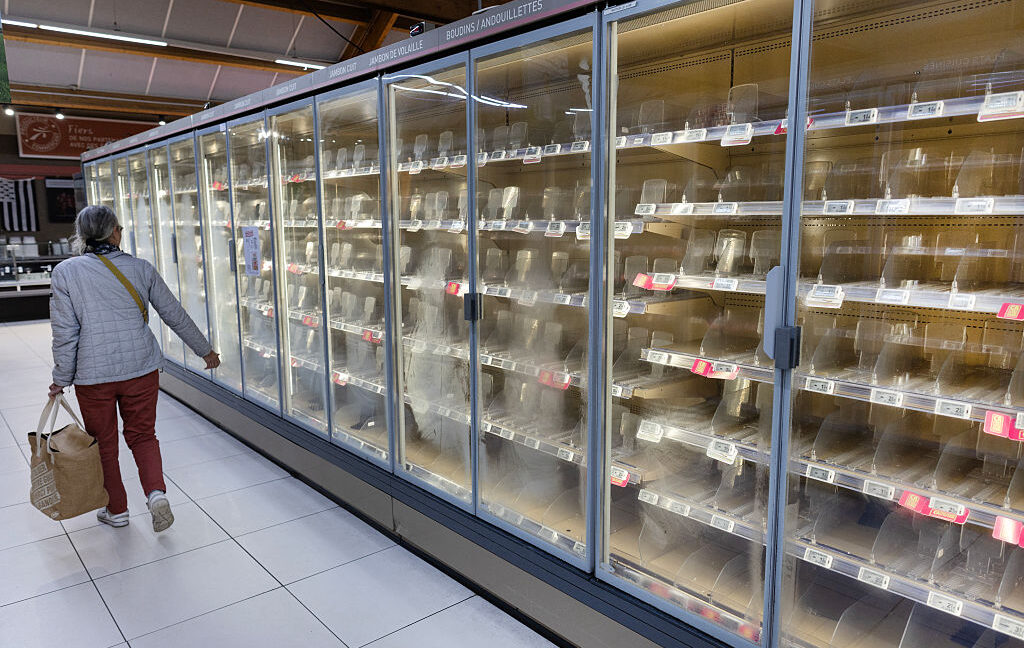
Fridge hack costing millions and sparking fires stemmed from poor security
Incident hitting 700 supermarkets exploited outdated devices exposed to the Internet.
fun new little websocket client published under @atproto/ws-client. works in the browser or server-side. designed for long-lived connections and reconnects. care taken with flow control and backpressure. because, you know... atproto go wsssshh. tangled.org/strings/did:plc:l3rouwludahu3…
