

Reusing passwords is a dangerous security practice. If someone gets ahold of your password—whether that's from a data breach, or wherever else—they can often gain access to any other account you used that same password. The solution is to use unique passwords everywhere and take additional steps to secure your...
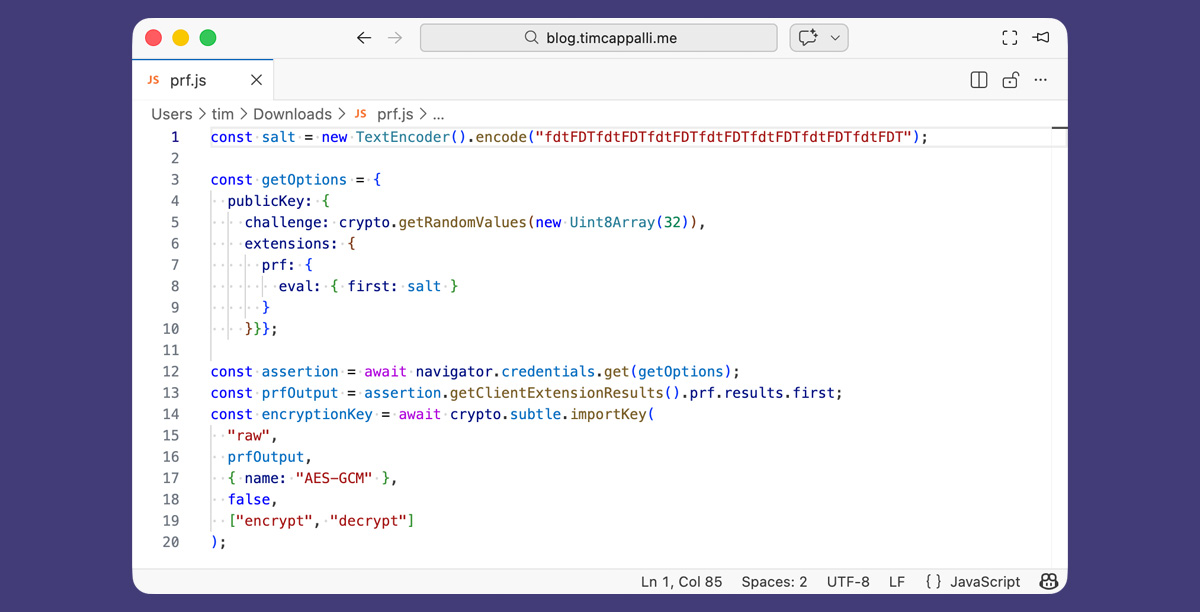
Please, please, please stop using passkeys for encrypting user data
Passkeys are the future of authentication, but using them for data encryption is a disaster waiting to happen. Overloading these credentials creates a dangerous blast radius that can lead to the irreversible loss of a user's most sacred memories and documents.
Vibe Password Generation: Predictable by Design - Irregular
LLM-generated passwords appear strong, but are fundamentally insecure. Testing across GPT, Claude, and Gemini revealed highly predictable patterns: repeated passwords across runs, skewed character distributions, and dramatically lower entropy than expected. Coding agents compound the problem by sometimes preferring and using LLM-generated passwords without the user’s knowledge. We recommend avoiding LLM-generated passwords and directing both models and coding agents to use secure password generation methods instead.
Blog | 1Password
Expert articles, security news, product updates, guides, and research from 1Password on password management, privacy, and digital security.
My brother passed away very suddenly a few years ago, and I was put in charge of... | Hacker News
It's a good thing to plan for this eventuality, to make it easy for your family and friends to wind up your "digital life" after you've passed. 1Password has a very good solution for this, with a "recovery document" you can print out and write down your password on, which contains instructions anyone else would need to access your 1Password account. I gave a copy of this document printed out to a small number of people I trust implicitly.
1Password
1Password is a multi-platform subscription-based password manager developed by AgileBits Inc. It is often used due to the combination of a master password with a...
Passwords, Secrets, and Access Management | 1Password
Protect passwords and secrets, manage app access, and secure AI tools with 1Password. Easy to adopt from growing teams to enterprise.
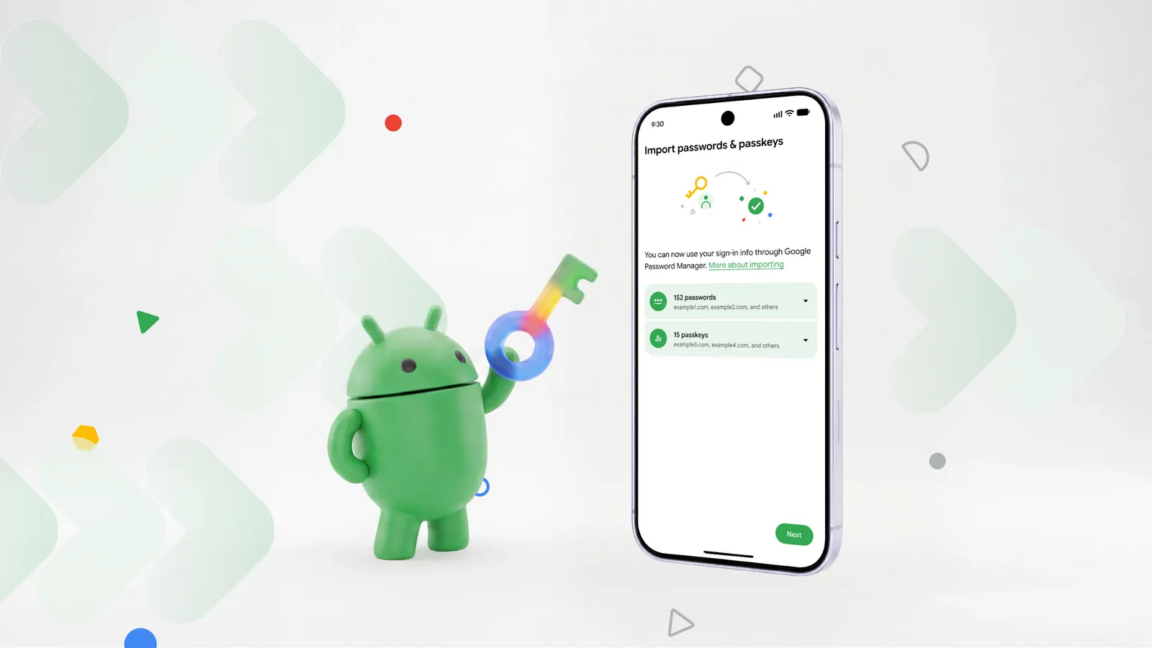
Android can now securely migrate your logins between password managers
App support is slim right now, but Google says more are coming.
Enpass: Secure Passkey & Password Manager That Keeps Your Data On Your Cloud Storage
With Enpass, choose where your passwords and passkeys are secured and synced – on your personal or business clouds (or even offline). Not on our servers
How do I import passwords from another password manager? | Vaultwarden
Learn how to import data from your old password manager into the web vault. Follow our simple steps for a smooth import.


Magic Links Have Rough Edges, but Passkeys Can Smooth Them Over
Magic links, those emailed one-time login links, are annoying and inconvenient for folks who use a password manager, but they radically accept some fundamental truths about signing in for everyone else. By layering passkeys on top of magic links, websites can provide a seamless authentication experience for all users.
I don't like passkeys | Ethan Hawksley
Why passkeys are a step back for personal security: examining account lockout risks, platform lock-in, hardware key limits, and fragile recovery flows.
Account compromise of “unprecedented scale” uses everyday home devices
Credential-stuffing attack uses proxies to hide bad behavior.

AChep/keyguard-app
A password manager that supports Bitwarden platform and KeePass (KDBX) files. It autofills your logins, supports passkeys, works offline, and runs a Watchtower that finds leaked and reused passwords and other issues.
I've been saying for nearly a year that getting the UX right for bsky's OAuth deployment is a major inflection point for reinforcing users mental models If we phrase things right, people will learn that this password UX controls access to my identity + slices of my atmosphere data (via my PDS)

Paul Rohr
Claude is inheriting a centralized app-centric bias here (which existing OAuth profiles may share) To wind up in a decentralized world where all "my data" lives on "my PDS" -- regardless of how many atproto apps I authorize to store stuff there for me (see 🧵) -- we should invert that paradigm