

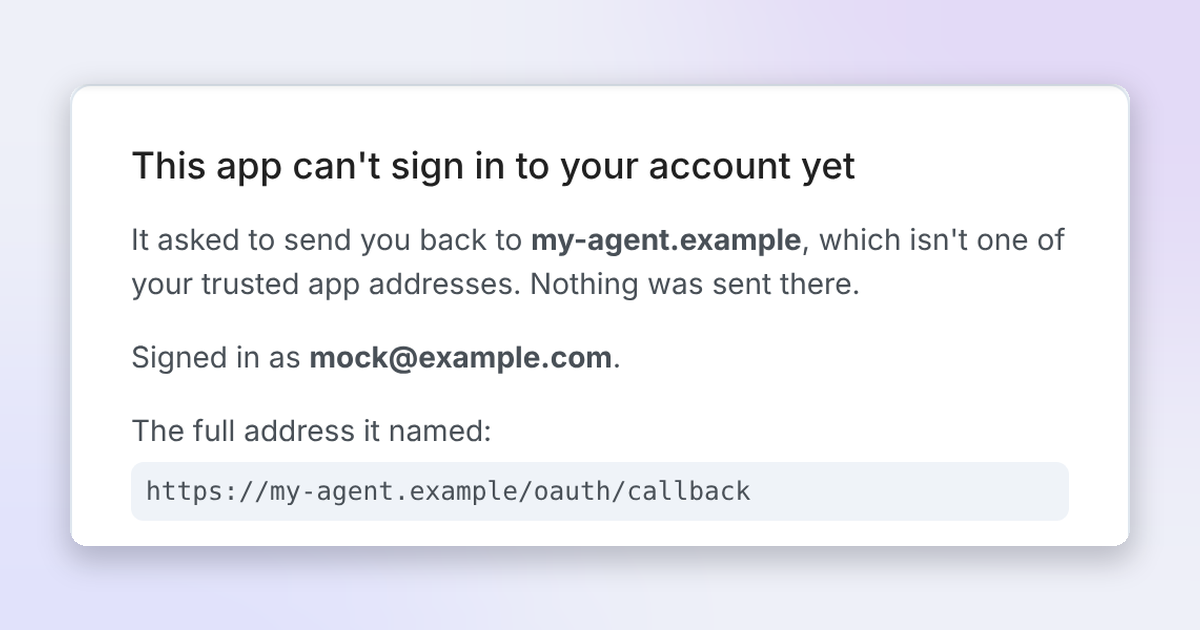
Why MCP servers either refuse custom clients or open a phishing hole, and how per-user trusted redirect URIs, decided at sign-in, give you both.
Let's fix OAuth in MCP
Update: The changes described in this blog post have been incorporated into the 2025-06-18 version of the MCP spec!
Enterprise-Managed Authorization: Zero-touch OAuth for MCP
The Enterprise-Managed Authorization extension to the Model Context Protocol is now stable, enabling organizations to centrally provision MCP server access through their identity provider so users get connected servers on first login without per-app OAuth.

MCP for agent-to-agent comms may be the riskiest protocol you've never heard of
Trust gaps in the new protocol spread malicious prompts from one agent to another.
MCP-B: The Right place to build your MCP server is in your website
With all the major security issues and data leakages the MCP ecosystem has been facing recently, the pre-authorized, user-scoped sandbox of the browser feels like more of the promised land than ever.
Magic Links Have Rough Edges, but Passkeys Can Smooth Them Over
Magic links, those emailed one-time login links, are annoying and inconvenient for folks who use a password manager, but they radically accept some fundamental truths about signing in for everyone else. By layering passkeys on top of magic links, websites can provide a seamless authentication experience for all users.
Secure MCP Tunnel | OpenAI API
Connect private or on-prem MCP servers to supported OpenAI products with an outbound-only MCP tunnel, without exposing them to the public internet.
What Redirect URL can I set for oauth2 callback in a chrome extension?
I want to use Imgur API in a chrome extension. The authentification response from user's input is sent to a "redirect url" set up in my application profile on the imgur web page. How can I set th...

go.userandagents.com is a custom short domain
Domain owners can set up redirects for their main domain in Domain Settings for free
GitHub MCP Exploited: Accessing private repositories via MCP
We showcase a critical vulnerability with the official GitHub MCP server, allowing attackers to access private repository data. The vulnerability is among the first discovered by Invariant's security analyzer for detecting toxic agent flows.
The OAuth mechanism and its most common flows
Every single time when you want to sign in to an application and you click on “Login with Google”, you are starting a protocol called…

Add openid4vp: as a safelisted scheme for protocol registration handling · Issue #11552 · whatwg/html
What problem are you trying to solve? In the context of digital wallets, the OpenID for Verifiable Presentations (OID4VP) 1.0 specification defines a new URI scheme, openid4vp:. The openid4vp: sche...
GitHub MCP Exploited: Accessing private repositories via MCP
GitHub's official MCP server grants LLMs a whole host of new abilities, including being able to read and issues in repositories the user has access to and submit new pull …
Protecting web applications via Envoy OAuth2 filter
Putting our long-tenured investment teams on the line to earn the trust of institutional investors.
this would be my answer too, atproto oauth is unironically extremely based

hailey
i guess in a way this is the most widely used one, but also one that is severely underused in other ways. definitely identity. i've long been of the opinion that there are obviously cool things that come from public data and all the public pieces of the proto, but identity is higher impact.
there’s a reason why i added this informational box to the sign in flow for @anisota.net — i wanted to make it clearer that the user is redirected away from anisota and to their own account/PDS… and that anisota isn’t getting their password helps that anisota’s design is SO diff from the oauth page

Kuba Suder 🇵🇱🇺🇦
I think Bluesky and #atdev community have some education work to do on the OAuth front, because some people seem to feel that OAuth is less secure than app passwords (see questions to Clearsky: why can't you just use app passwords like everyone else, why do I need to give you my real password etc.)

