Securely connect to and manage access to your internal resources using Tailscale Services.
Tailscale Funnel
Securely route internet traffic to local services using Tailscale Funnel.
The best ways to use Tailscale for sharing with friends and family
Using Tailscale's sharing features to make files, self-hosted services, and exit nodes available to your inner circle.

The Tailscale node you mail to your parents
Securely connect to anything on the internet with Tailscale. Built on WireGuard®️, Tailscale enables you to make finely configurable connections, secured end-to-end according to zero trust principles, between any resources on any infrastructure.
Tailscale | Secure Connectivity for AI, IoT & Multi-Cloud
The connectivity platform for devs, IT, and security teams. Zero Trust identity-based access that deploys in minutes and scales to every resource. Start free.
Digging into how Tailscale encrypts its state file on Windows, Apple, and Linux
Tailscale's latest version encrypts more data at rest, making it harder for attackers to potentially clone your nodes. Here's how it works.


Workload identity federation: better infra and CI/CD auth with Tailscale
Securely authenticate systems to Tailscale without managing long-lived API keys, auth keys, or OAuth clients.
How to self-host with Tailscale: Installing Proxmox and hardware choices
In this tutorial, we’ll start by picking out hardware and installing Proxmox. Tailscale can then securely connect to your self-hosted storage.
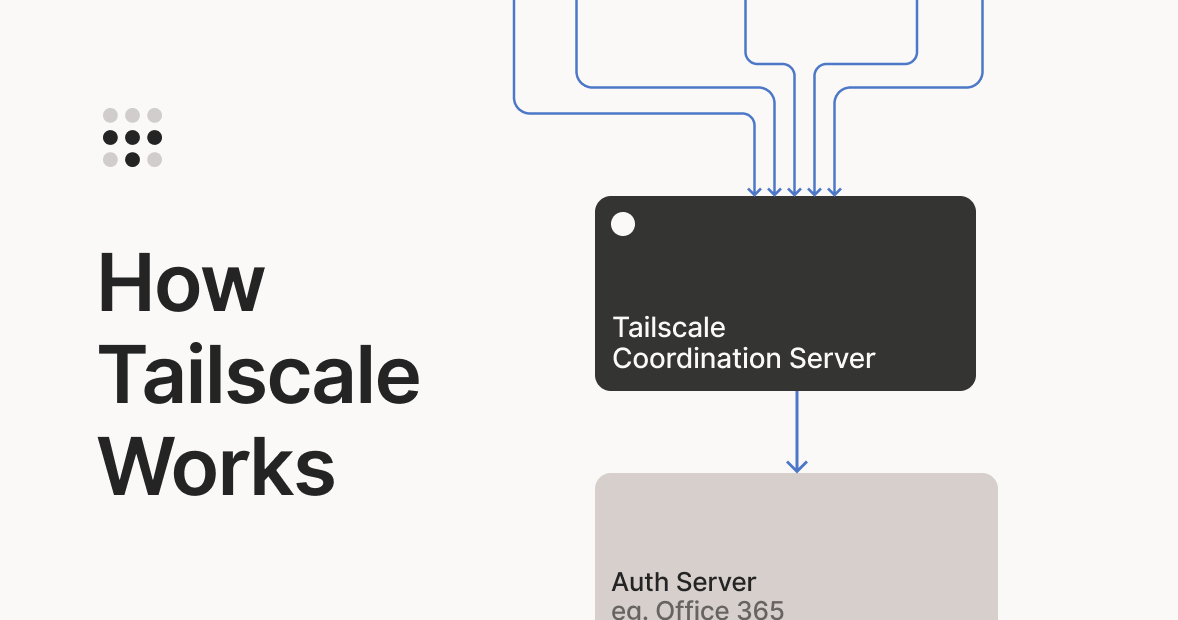
Tailscale: How it works
Understand the entire Tailscale system, how it works, how we built it, and its benefits compared to legacy VPNs. Use this article as a guide to quickly build your own Tailscale replacement.
How we built a lightweight identity provider using Tailscale's tools
How tsnet, application security grants, and Funnel combined to build a secure authorization app.

Tailworm
The design choices of the open source tailscale and headscale software have created an environment ripe for risk, while marketing security as its design and purpose. Choices have been made to move away from security-in-depth, removing layers of authentication, and replacing daemons such as OpenSSH which employ privilege-separation with a highly-privileged process. Other findings include broader-than-advertised network security boundaries, which seems to be legitimate bugs, but the missing security and isolation is precisely what users are advertised by these tools.
Build a flexible AI stack with Aperture
Securely connect to anything on the internet with Tailscale. Built on WireGuard®️, Tailscale enables you to make finely configurable connections, secured end-to-end according to zero trust principles, between any resources on any infrastructure.

Tailscale’d Into Homelabbing
Having my own homelab was something I wanted to try for a long time. However, I just couldn’t get started. Mostly because I kept overthinking it. How will I handle dynamic IPs? Do I need something like a local DNS on my router for that? Even if I solve things inside the home, how am I supposed to access it remotely? Do I need port forwarding at the NAT layer? And what about TLS certificates, how do I even manage those without using a public certificate authority?

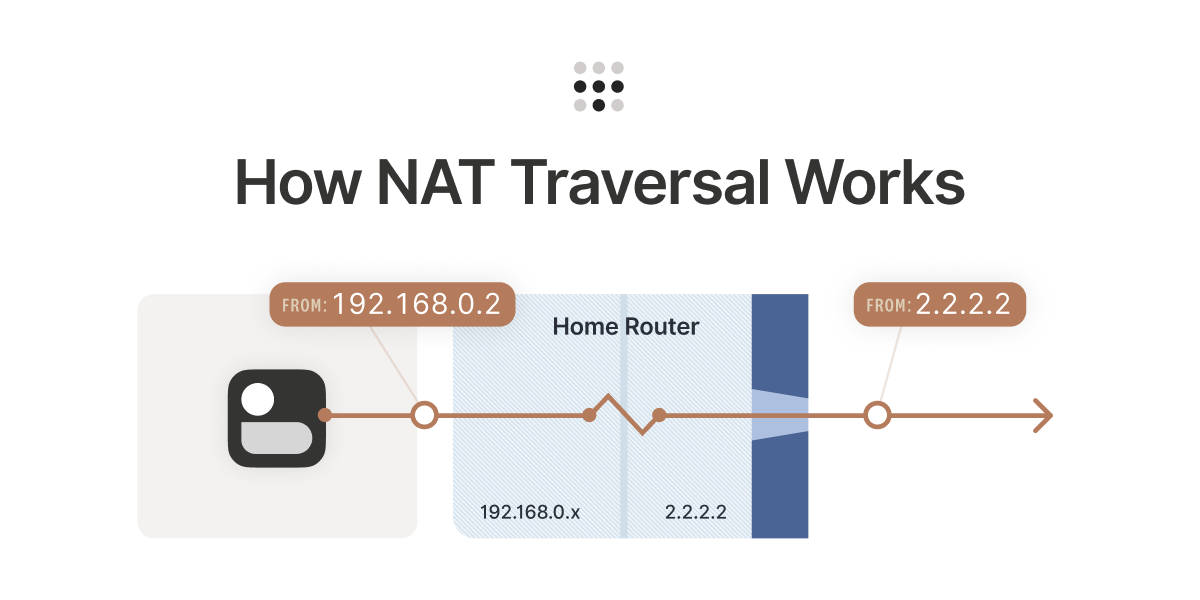
How NAT traversal works
Learn how NAT traversal works, how Tailscale can get through and securely connect your devices directly to each other.