The founder of security-focused messenger Signal, Moxie Marlinspike, revealed today that he found and exploited vulnerabilities in software from Cellebrite, a company that specializes in digital forensics tools that have been used by authorities around the world to extract data from phones. In a blog post, Marlinspike claimed that he found one of the company’s devices in a package […]
Autom Tagsa on Twitter / X
How Signal hacked the device that claimed to hack Signal https://t.co/aX1rpFZZyP via @thenextweb— Autom Tagsa (@autom8) April 27, 2021
Israeli Spy Tech Firm Says It Can Break Into Signal App - Slashdot
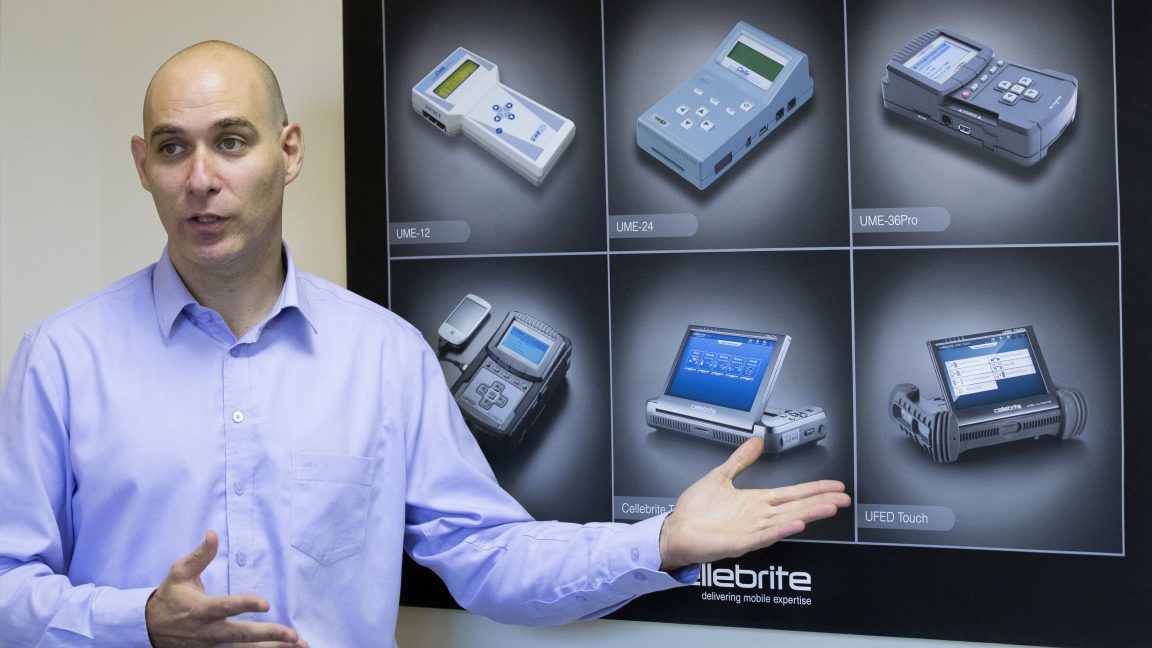
Last Thursday, Israeli phone-hacking firm Cellebrite said in a blog post that it can now break into Signal, an encrypted app considered safe from external snooping. Haaretz reports: Cellebrite's flagship product is the UFED (Universal Forensic Extraction Device), a system that allows authorities to...

Hack reveals data company Cellebrite works with everyone from US cops to Russia
Cellebrite unaware of "increased risk to customers as a result of this incident."
Signal Developer Explains Why Early Encrypted Messaging Tools Flopped
'The intuition was to take the complexity and push it onto the user,' Moxie Marlinspike says at Black Hat. 'We were just wrong.'

Hack Reveals the a16z-Backed Phone Farm Flooding TikTok With AI Influencers
A hacker gained control of a 1,100 mobile phone farm powering covert, AI-generated ads on TikTok.
What is Signal? The messaging app, explained.
With news this week of the messaging app being used to discuss war plans, we get you up to speed on what Signal should be used for—and what it shouldn’t.

Using leaked data to examine vulnerabilities in SMS routing and SS7 signalling
By Gabriel Geiger and Crofton Black, Lighthouse Reports

Under Meredith Whittaker, Signal Is Out to Prove Surveillance Capitalism Wrong
On its 10th anniversary, Signal’s president wants to remind you that the world’s most secure communications platform is a nonprofit. It’s free. It doesn’t track you or serve you ads. It pays its engineers very well. And it’s a go-to app for hundreds of millions of people.
Malte Spitz: Your phone company is watching
SnoopSnitch - Apps on Google Play
Show missing security patches. Find mobile abuse (IMSI catchers & stealth SMS).

How A Massive Ad Fraud Scheme Exploited Android Phones To Steal Millions Of Dollars
A BuzzFeed News investigation uncovered a sophisticated ad fraud scheme involving more than 125 Android apps and websites, some of which were targeted at kids.

Signal creator Moxie Marlinspike wants to do for AI what he did for messaging
Introducing Confer, an end-to-end AI assistant that just works.
The Technology the Trump Administration Could Use to Hack Your Phone
Other Western democracies have been roiled by the use of spyware to target political opponents, activists, journalists, and other vulnerable groups. Could it happen here?
Bill C-22’s Groundhog Day: Why the Government’s Dismissal of Signal, Apple and the U.S. Congress Concerns Runs Back the Disastrous Online News Act Playbook - Michael Geist
Secure messaging service Signal yesterday became the latest company to warn that Bill C-22, the lawful access bill, could force it to leave the Canadian market rather than comply with provisions it says would compromise its end-to-end encryption and create new cybersecurity risks. Signal vice-president Udbhav Tiwari told the Globe and Mail that the company “would rather pull out of the country than be compelled to compromise on the privacy promises we have made to our users.” The comments are part of a steady stream of similar warnings from Apple, Meta, the Canadian Chamber of Commerce, the Cybersecurity Advisors Network, and the chairs of the U.S. House Judiciary and Foreign Affairs Committees. Despite growing concern, the government’s response has been to launch a misleading social media campaign and repeatedly insist that the experts and companies are mistaken.
Hacking Millions of Modems (and Investigating Who Hacked My Modem)
Two years ago, something very strange happened to me while working from my home network. I was exploiting a blind XXE vulnerability that required an external HTTP server to smuggle out files, so I spun up an AWS box and ran a simple Python webserver to receive the traffic from the vulnerable server.
Russia-aligned hackers are targeting Signal users with device-linking QR codes
Swapping QR codes in group invites and artillery targeting are latest ploys.