

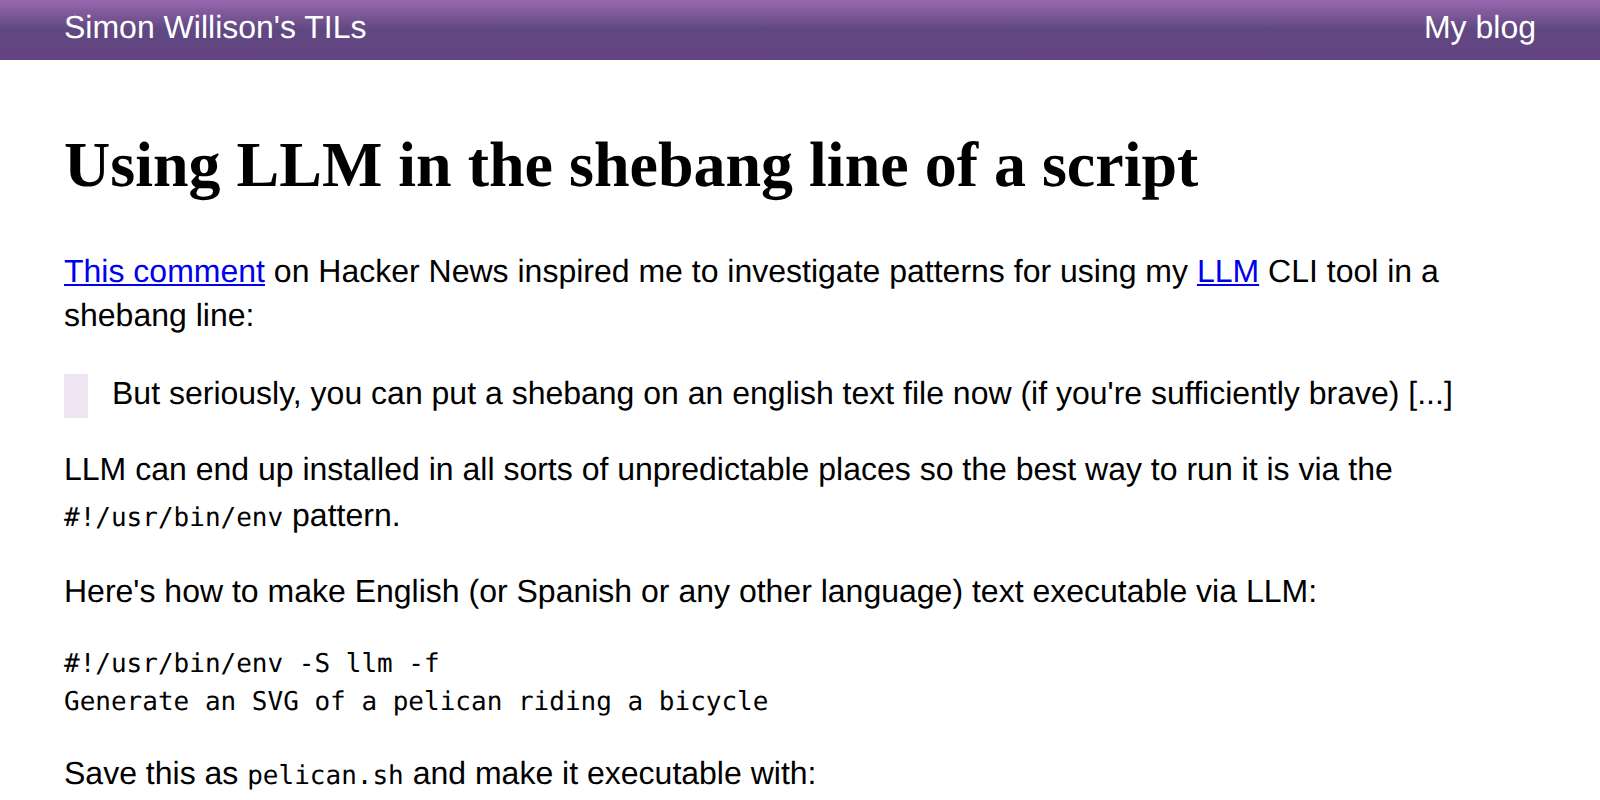
This comment on Hacker News inspired me to investigate patterns for using my LLM CLI tool in a shebang line:
Your LLM Doesn't Write Correct Code. It Writes Plausible Code.
One of the simplest tests you can run on a database:
mufeedvh/code2prompt
A CLI tool to convert your codebase into a single LLM prompt with source tree, prompt templating, and token counting.
chad/whichlang
What programming language do LLMs default to when you don't tell them? A small benchmark.
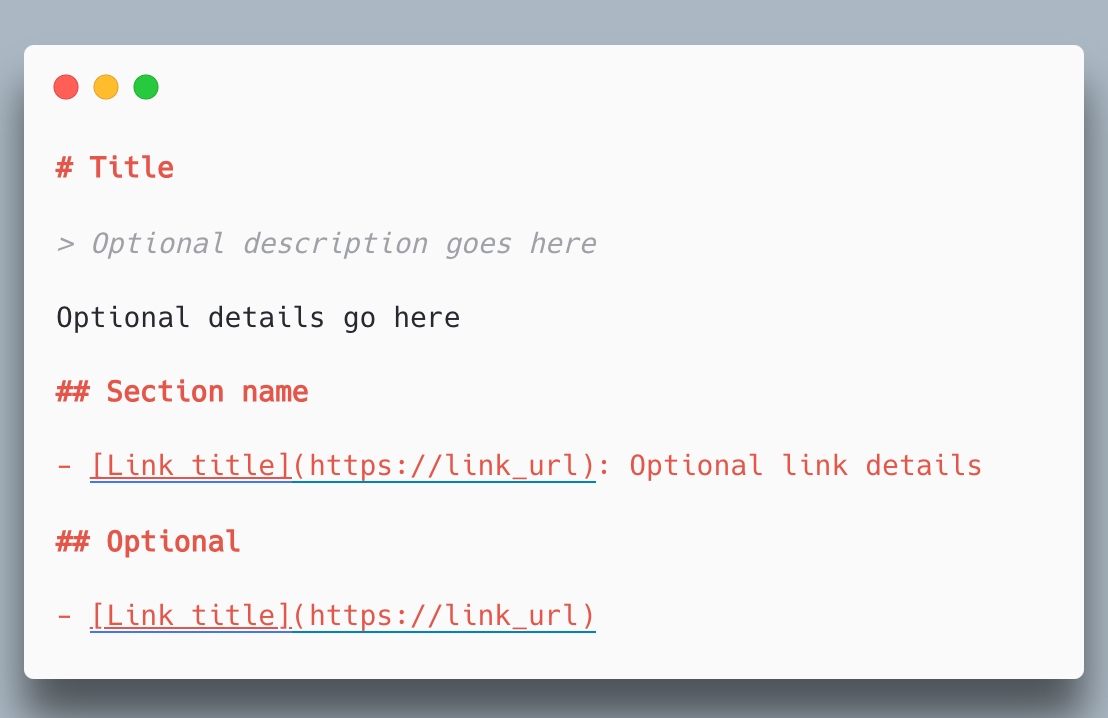
The /llms.txt file – llms-txt
A proposal to standardise on using an /llms.txt file to provide information to help LLMs use a website at inference time.
Copyrightability of LLM-generated code: Can we license “vibe code” into Free Software? - FSFE
The use of large language models (“LLMs”) has exploded in recent years, including in the generation of source code. But even as their usage gains popularit...


Coding with LLMs in the summer of 2025 (an update) - <antirez>
Provisional Guidance for Users of LLM-Based Code Generators
available intuition for avoiding big risks

Build agents, not pipelines
There are only two ways to use LLMs in a computer program: as part of a pipeline, or as an agent. In other words, either you express the control flow of the program in code, or you give a LLM tools and allow it to manage the control flow itself1.
Wikipedia:LLM-assisted translation
This guideline applies to machine translation tools that include a large language model ("LLM"). Assume that it applies to any online translation tool unless you have confirmed there is no LLM element.
I just came across this paper arxiv.org/abs/2509.22908 which coins the term "vericoding" for using LLMs to generate formally verified code, and presents benchmark results for several languages

A benchmark for vericoding: formally verified program synthesis
arxiv.org
Martin Kleppmann
New blog post! ✨ I argue that AI will make formal verification go mainstream. martin.kleppmann.com/2025/12/08/ai-formal-verifica… Three reasons for this: 1. LLMs are getting increasingly good at writing proofs using proof assistants. This will make formal verification vastly cheaper than it's been to date.
Sensitive data + tool use + LLMs + app-centric security model = danger. LLMs turn any text into potentially executable instructions, exploding the attack surface of traditional security models.

Simon Willison
Just blogged my hunch that the Apple intelligence Siri delay is because of security concerns around prompt injection here simonwillison.net/2025/Mar/8/delaying-personali…

